Connected medical devices and health software are now reviewed for cybersecurity before they reach the market. The EU MDR and IVDR include IT security in their general safety and performance requirements, and the FDA expects a cybersecurity section in premarket submissions, including a software bill of materials for cyber devices.
Security often arrives late, as a document written for the submission rather than a practice in development. Missing threat models, an incomplete SBOM or no plan for vulnerabilities after launch then delay approval and leave risks in the field.
What we do
Healthcare & MedTech Security
Map your obligations
We work out which rules apply to each product and market: EU MDR or IVDR, FDA premarket cybersecurity, NIS2 for your organisation and the EU Cyber Resilience Act for connected products that are not medical devices.
Assess your secure development lifecycle
We compare your development and maintenance processes with IEC 81001-5-1 and give you a prioritised gap list.
Threat modelling and security risk management
We model threats to the device, its interfaces and its cloud services, assess security risks and link them to your safety risk management.
SBOM and vulnerability management
We build a software bill of materials, set up monitoring for known vulnerabilities and define how you assess, fix and disclose them after launch.
Testing and documentation
We test the product, including penetration testing, and prepare the security risk management file and cybersecurity documentation for your technical file or premarket submission.
How we deliver
Consulting · Professional services · Managed services
Consulting
We map your regulatory obligations, assess your secure development lifecycle and plan the work for each product.
Professional services
We carry out threat modelling, security risk assessments, SBOM creation and testing, and write the documentation with your engineering and regulatory teams.
Managed services
We run postmarket vulnerability monitoring for you: tracking new vulnerabilities in your SBOM, assessing their impact and keeping the documentation current.
AI automation in this service
Automated SBOM generation from your build pipeline, with components matched against public vulnerability databases.
Automated first-pass triage of new vulnerabilities by affected component and product, ready for a security engineer to assess.
Automated pre-fill of threat model and security risk documentation templates from your architecture and component data.
What you get
Regulatory obligation map per product and market
Gap analysis against IEC 81001-5-1
Threat model and security risk assessment
Security risk management file
Software bill of materials and vulnerability management process
Penetration test report
Cybersecurity documentation for the technical file or premarket submission
Frameworks
EU MDR
EU IVDR
IEC 81001-5-1
EU CRA
NIS2
GDPR
In detail
Regulations and standards we help you meet
EU MDR (Regulation (EU) 2017/745)
EU IVDR (Regulation (EU) 2017/746)
FDA premarket cybersecurity requirements
IEC 81001-5-1
EU Cyber Resilience Act (Regulation (EU) 2024/2847)
NIS2
Product security activities
Threat modelling
Security risk management
Software bill of materials (SBOM)
Vulnerability management and coordinated disclosure
Penetration testing
Secure development lifecycle
Platform
After the project, the Fidempli platform keeps it running
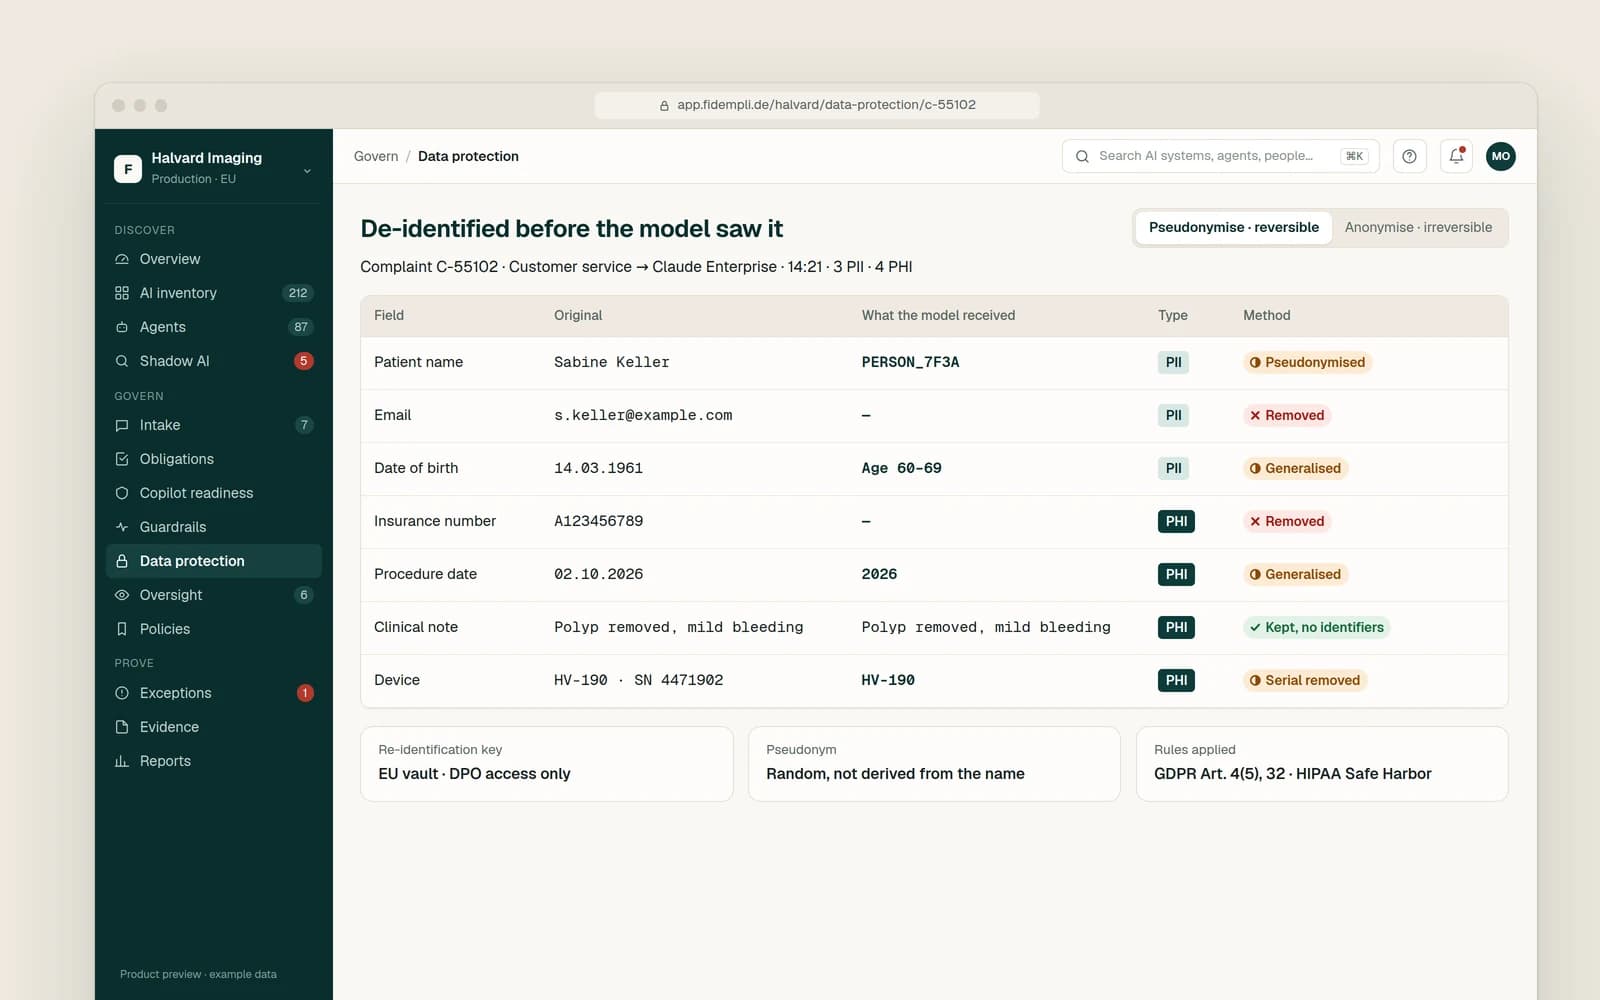
From December 2026, the Fidempli platform removes or pseudonymises patient and health data before any AI model sees it, with the re-identification key kept in the EU. That protects the AI tools your teams use in development, support and complaint handling.
Which cybersecurity rules apply to medical devices in the EU?
The EU MDR and IVDR include IT security in their general safety and performance requirements. IEC 81001-5-1 describes security activities across the health software lifecycle. NIS2 may apply to your organisation, depending on your size and sector.
Does the EU Cyber Resilience Act apply to medical devices?
Products covered by the MDR and IVDR are excluded from the Cyber Resilience Act. Connected products you make that are not medical devices, such as companion apps or accessories, may fall under it. We help you sort each product.
What does the FDA expect for cybersecurity?
Premarket submissions for devices with cybersecurity risk need documentation such as a threat model, security risk assessment, an SBOM and a plan for monitoring and addressing vulnerabilities after launch.
What is a security risk management file?
It documents the security risks you identified, how you assessed and controlled them and what risk remains. It sits alongside your safety risk management and is updated throughout the product's life.
Can you help with products already on the market?
Yes. We build the SBOM and threat model retrospectively, set up vulnerability monitoring and close documentation gaps before your next submission or audit.