
Platform
After the project, the Fidempli platform keeps it running
The managed service runs on the Fidempli platform, which launches in December 2026. You keep full access to your data, decisions and evidence at all times.
Explore the platform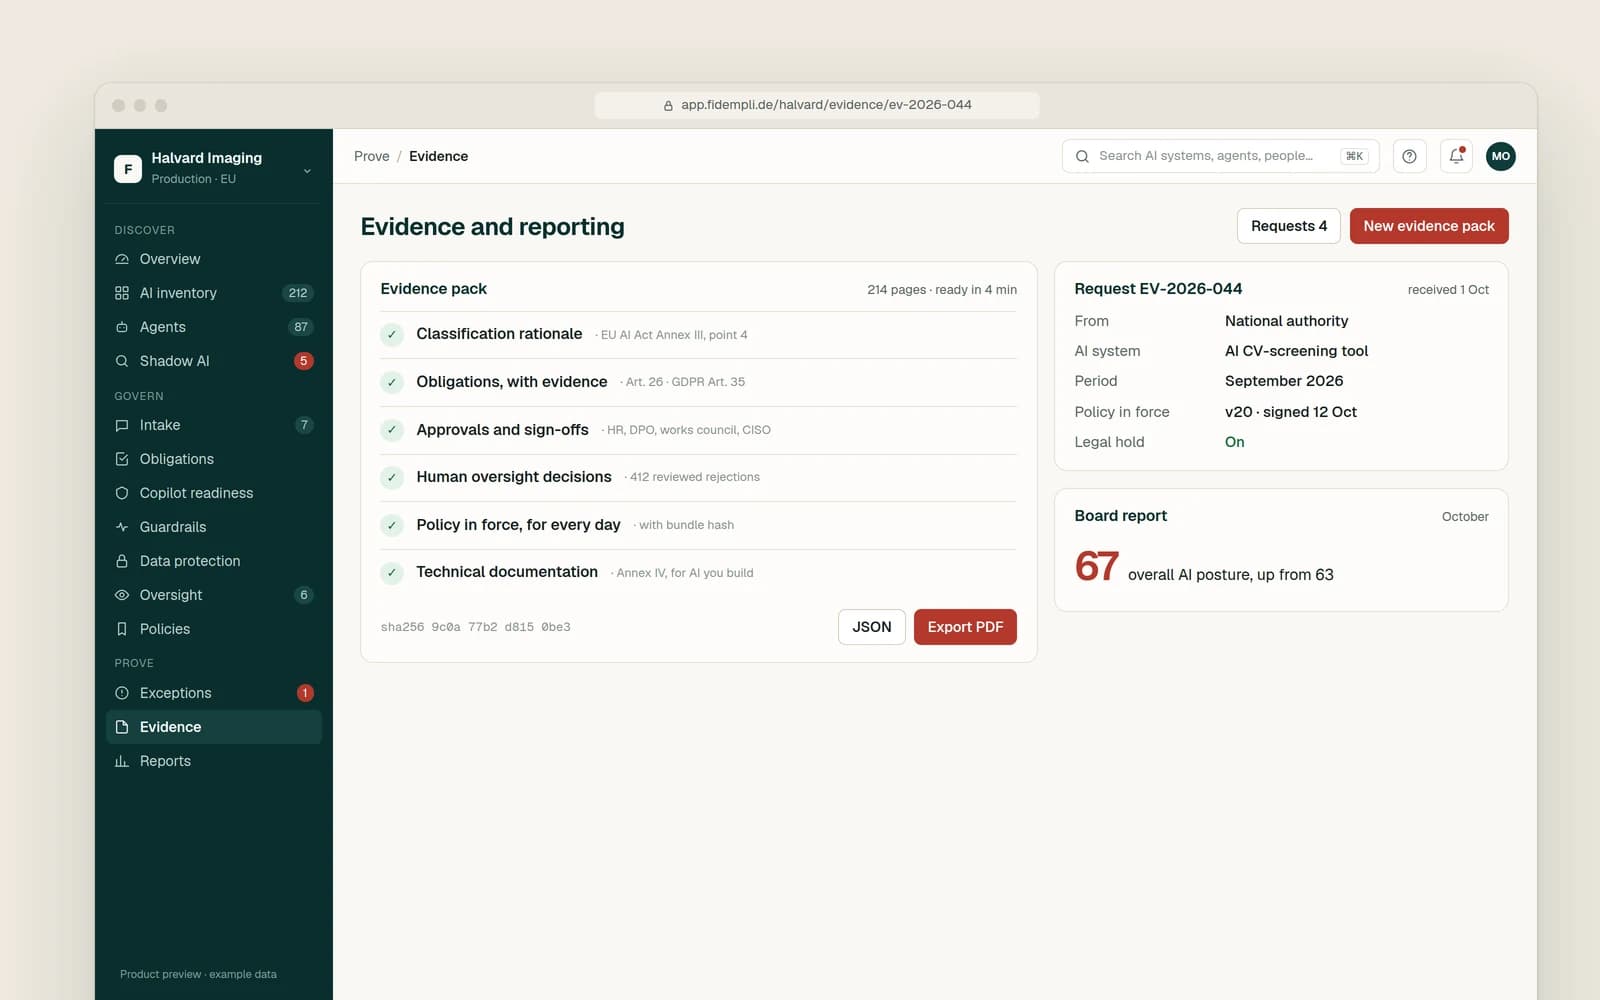
AI Governance, Privacy & AI Security
AI governance that runs every week, without building a new team for it.
The problem
AI governance is not a project with an end date. New tools, agents and use cases arrive every week, owners change, and accepted risks expire. Someone has to keep up.
Few organisations have the people to review AI requests, watch for shadow AI, chase owners and prepare evidence on top of their day jobs. When that work slips, the register goes stale and the next audit or authority request becomes a scramble.
What we do
We agree scope, roles, approval limits and reporting with you, and take over your existing AI register and policies.
We review new AI requests, pre-classify them by EU AI Act tier, check vendors and route decisions to your named approvers.
We watch for shadow AI, ownerless agents, failing controls and expiring exceptions, and follow up with the owners.
We collect and maintain evidence for each AI system and obligation, so it is ready when an auditor or authority asks.
We prepare regular reports on AI risk, open findings and decisions for management and the board, on the schedule you set.
How we deliver
We help you decide which governance tasks to keep in-house and which to hand to us, and set the rules we work by.
We set up the platform, workflows and reporting that the managed service runs on.
We run intake, monitoring, evidence and board reporting for you, while decisions stay with your named owners.
Frameworks
Platform
The managed service runs on the Fidempli platform, which launches in December 2026. You keep full access to your data, decisions and evidence at all times.
Explore the platformYou do. We prepare, review and route requests, but approvals and accepted risks stay with your named owners.
Yes. We can run the service with your existing tools and move it to the platform when it launches in December 2026.
We agree the reporting schedule and format with you during onboarding, for example monthly for management and quarterly for the board.
Yes. Your data, workflows and evidence stay in your platform tenant, so your team can take over at any time.
No. We support them with the daily governance work, and they keep their responsibilities and reporting lines.
A senior consultant replies within one business day. Or join the 3–5 design partners shaping the platform before launch.