Home Solutions ISO/IEC 42001 ISO/IEC 42001
Run an AI management system you can certify. ISO/IEC 42001 asks for an AI management system: an inventory, risk assessment, controls, roles and records. Fidempli gives you the records an auditor asks for, kept current by live data.
Product preview with example data How Fidempli handles it
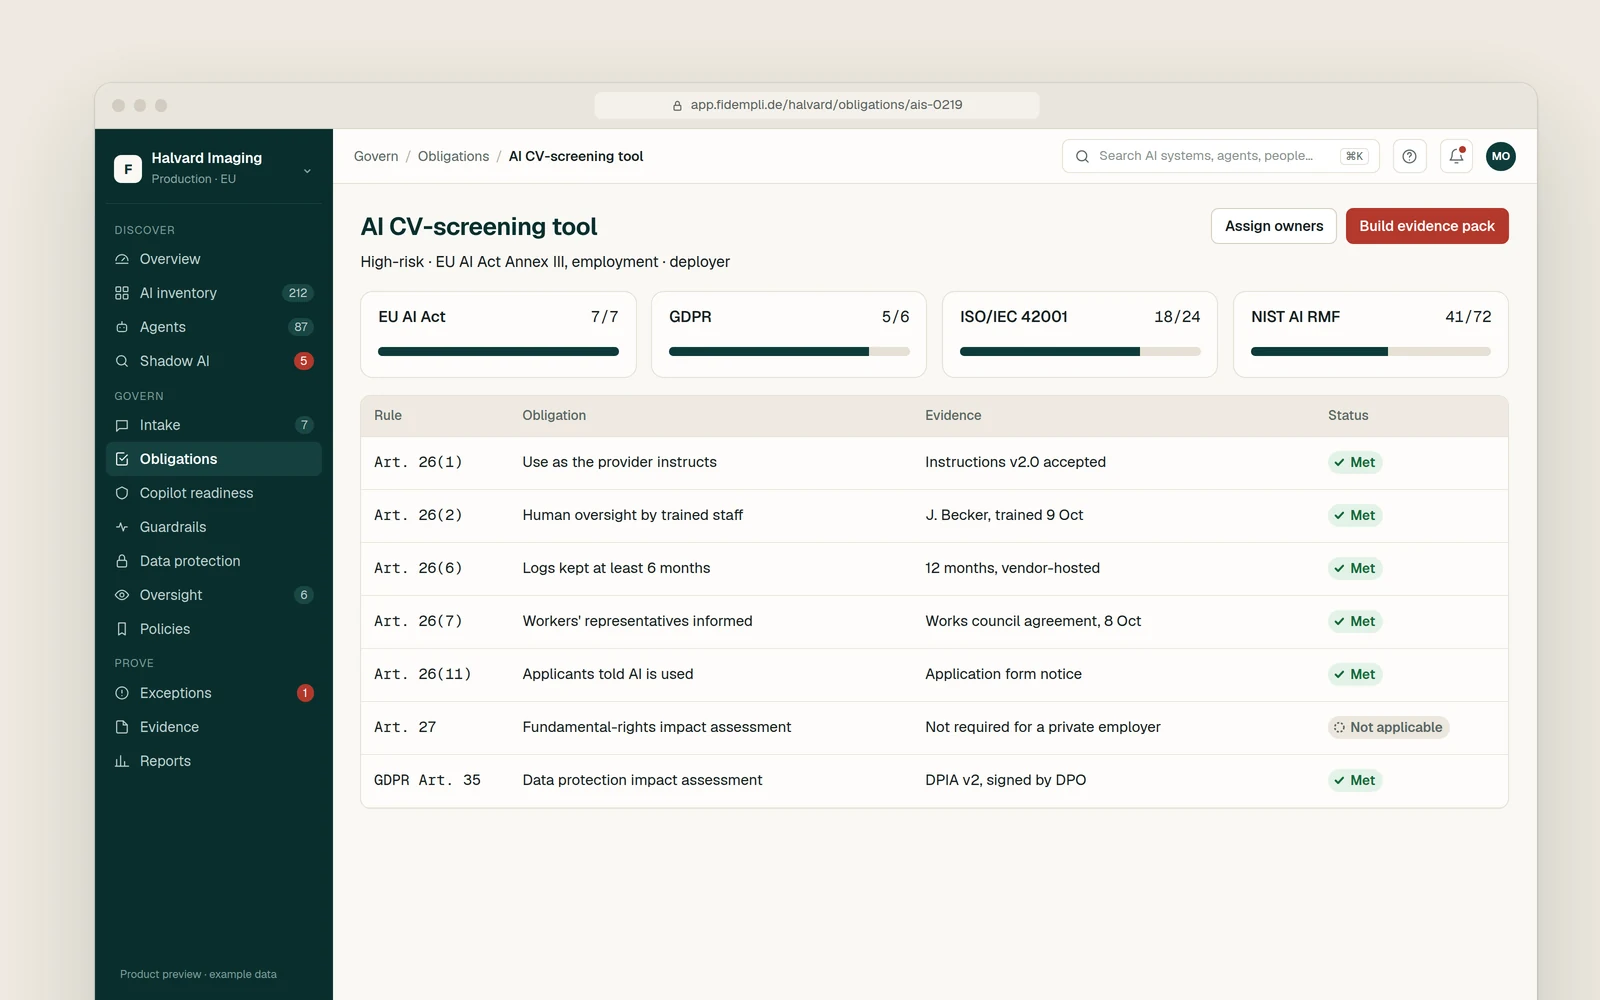
ISO/IEC 42001 requirements, mapped to the platform. Requirement How Fidempli handles it Capability Scope and inventory of AI systems One inventory of AI tools, models and agents across providers AI inventory Roles and responsibilities Every AI system and agent has a named owner, with attestation Agent governance AI risk and impact assessment Risk-based intake with classification and reviewer sign-off Intake and approval Annex A controls Controls mapped to each AI system with status and evidence Compliance mapping Monitoring and nonconformity Live checks behind accepted risks; failing conditions raise an alert Exceptions and accepted risk Documented information and management review Evidence packs and a board report from the decision log Evidence and reporting
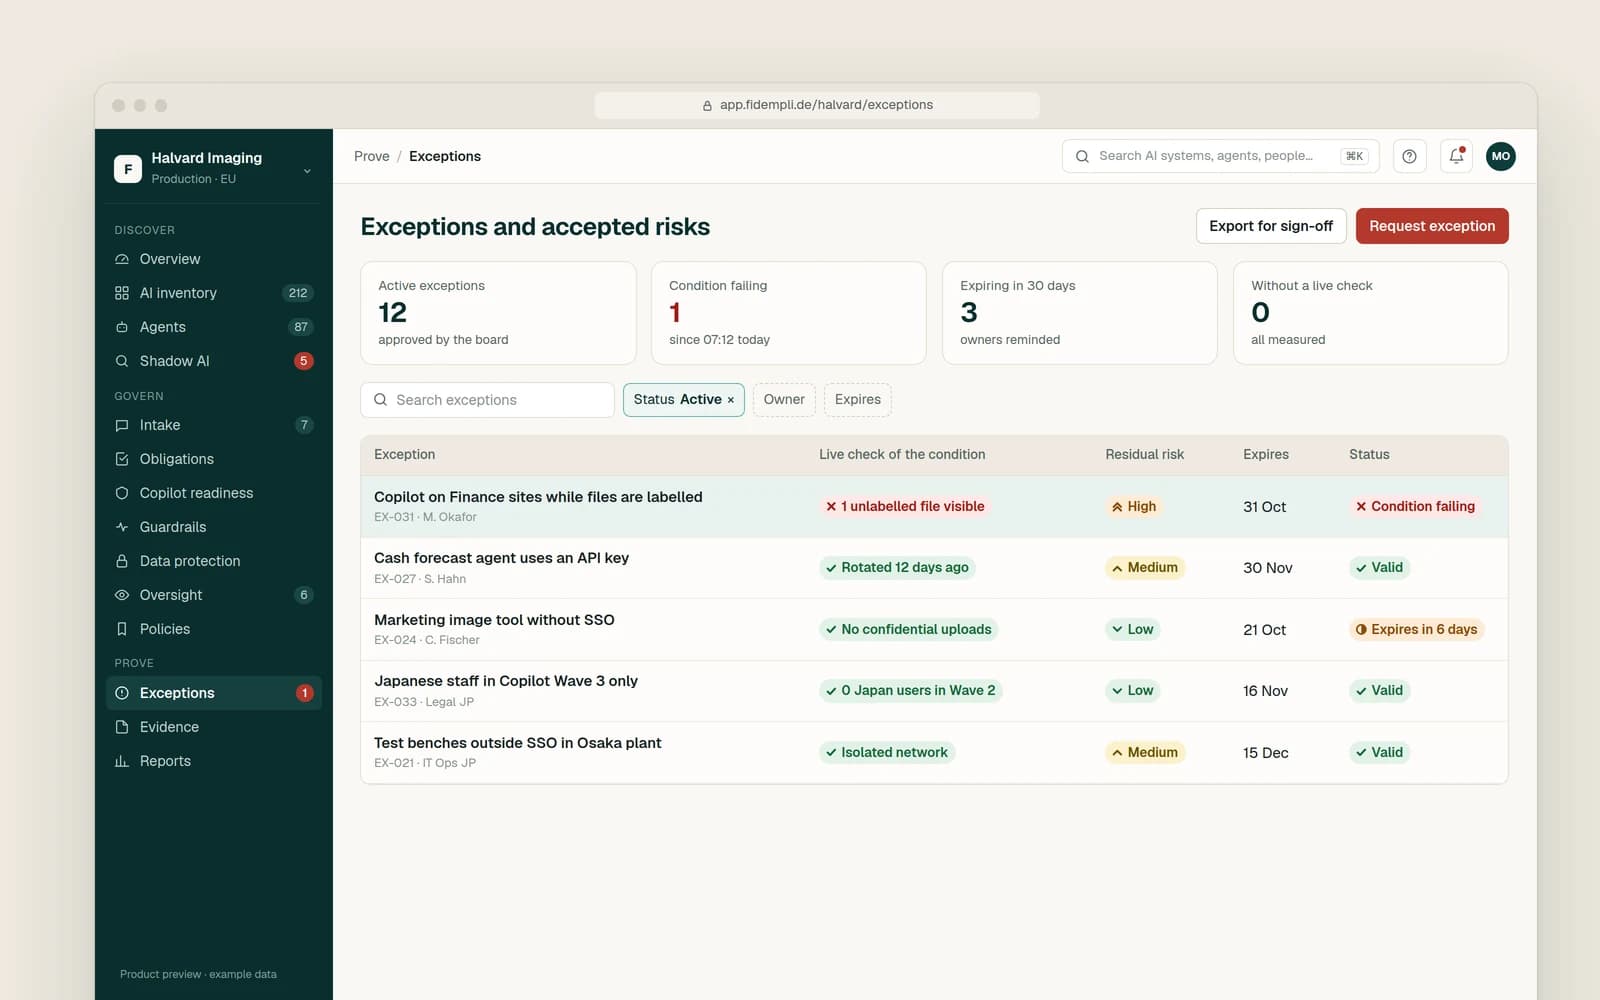
Accepted risks that stay true. Every exception has an owner, an expiry date and a live check, so the risk you accepted is the risk you still have.
Compensating control and residual risk for each exception Alerts when a condition fails Reminders before an exception expires Product preview with example data Related services
Consulting · Professional services · Managed services Other solutions Fidempli provides governance, risk and compliance advisory and works alongside your legal counsel. We do not provide legal advice.
Start with the framework that matters most to you. Our consultants assess where you stand; the platform keeps it current.