The Fidempli AI governance platform launches in December 2026. Design-partner places are open.Apply now →
Fidempli

Platform

The AI governance platform for privacy and security – in your cloud or ours.

One record per AI system, shared by every team. Connected to Microsoft 365, OpenAI, Anthropic, Google and AWS, so what you see is live data, not a questionnaire.

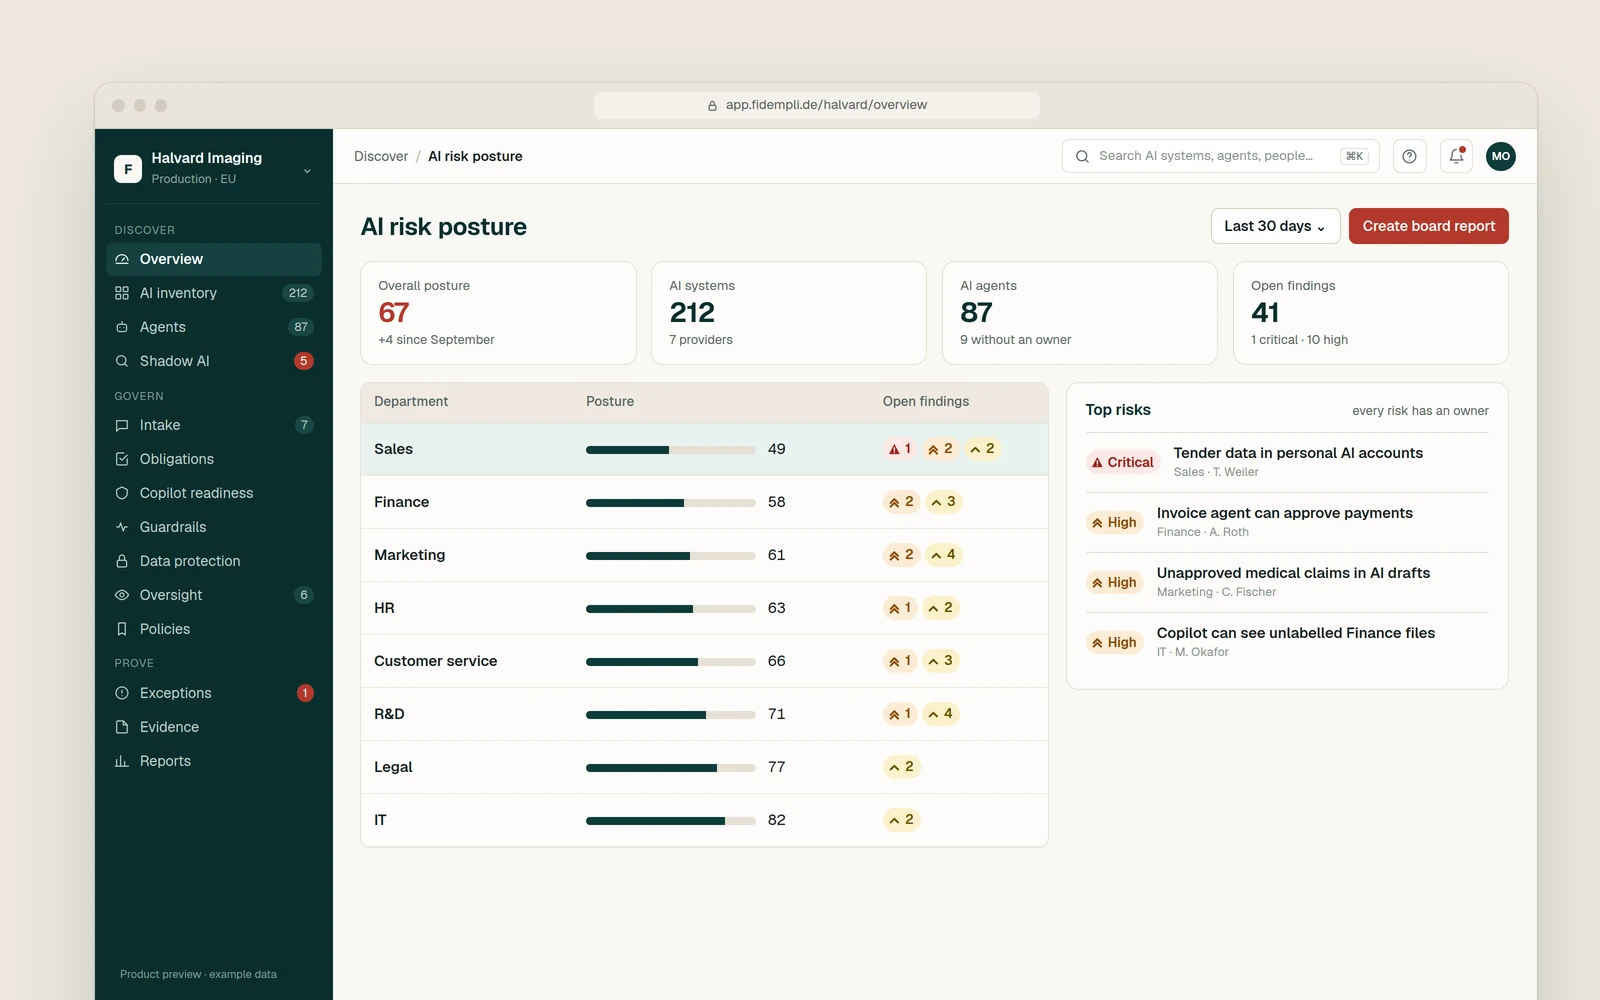
Fidempli AI risk posture dashboard with posture by department and the top risks
Product preview with example data

01 · Discover

Know every AI system, agent and app in use.

Fidempli connects to the platforms your company already uses and builds one inventory: AI tools, models, agents and the apps staff use without approval, each with an owner.

Learn more: Discover
Discover

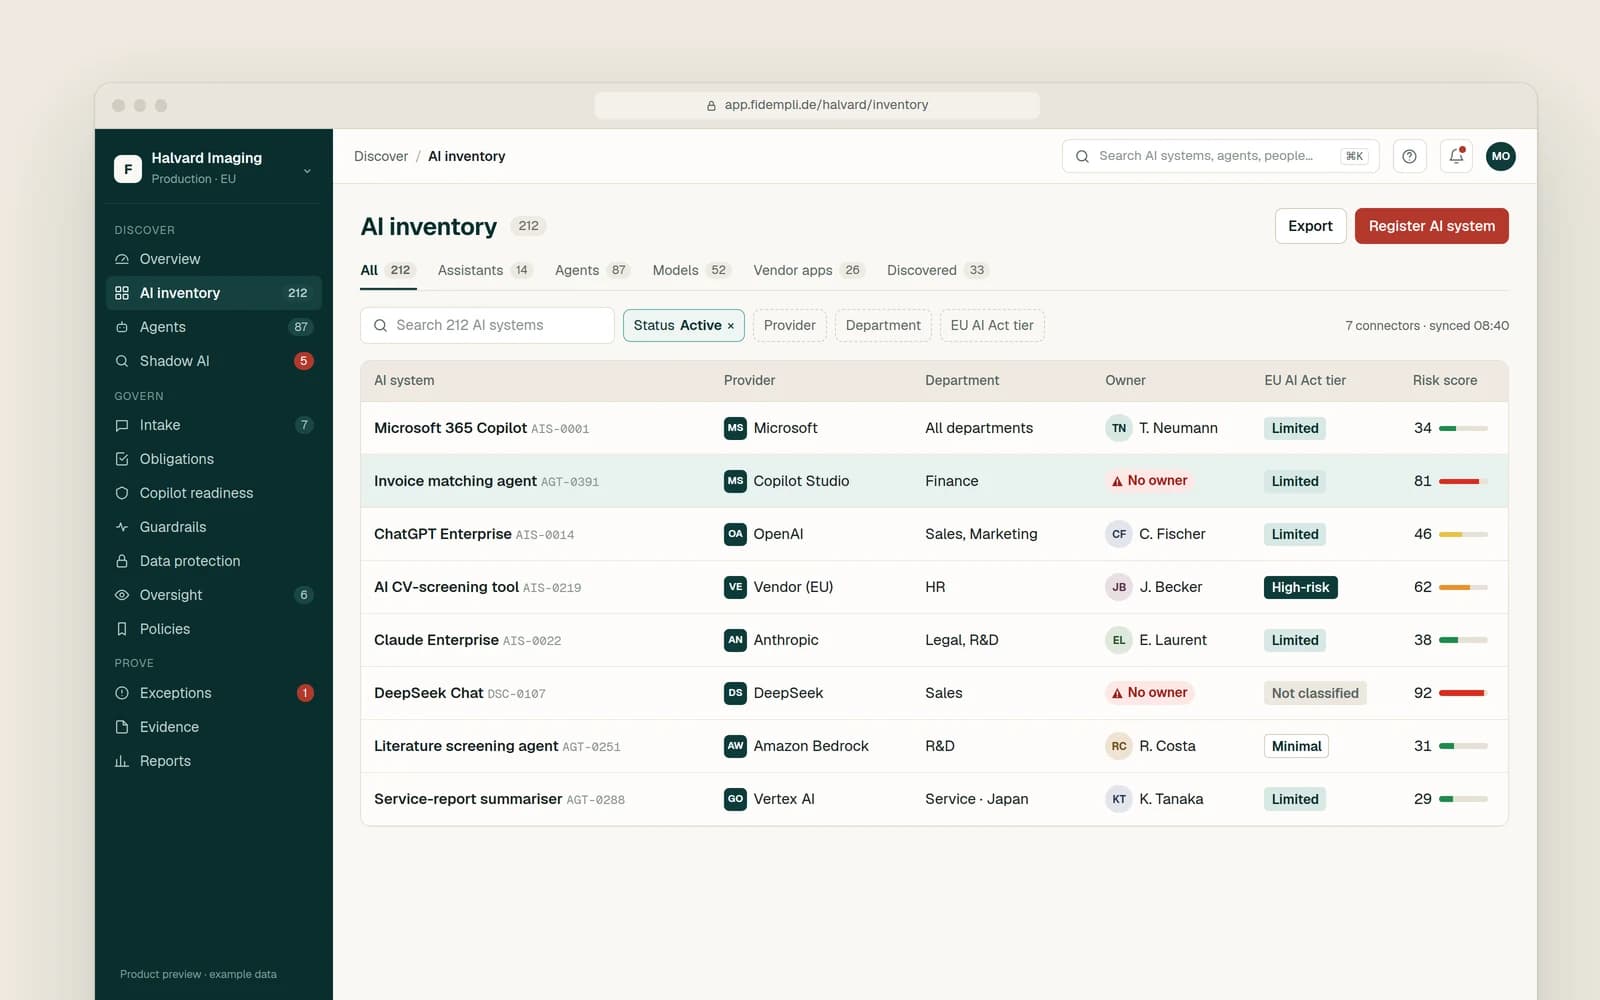
AI inventory

See every AI tool, model and agent in the company, from Microsoft and OpenAI to your own.

  • Connectors for Microsoft 365, Copilot Studio, Azure, OpenAI, Anthropic, Google and AWS
  • Owner, department, provider and EU AI Act tier for every record
  • Records without an owner or a classification are flagged
Learn more: AI inventory
AI inventory listing AI systems from several providers with department, owner, EU AI Act tier and risk score
Product preview with example data
Discover

Shadow AI

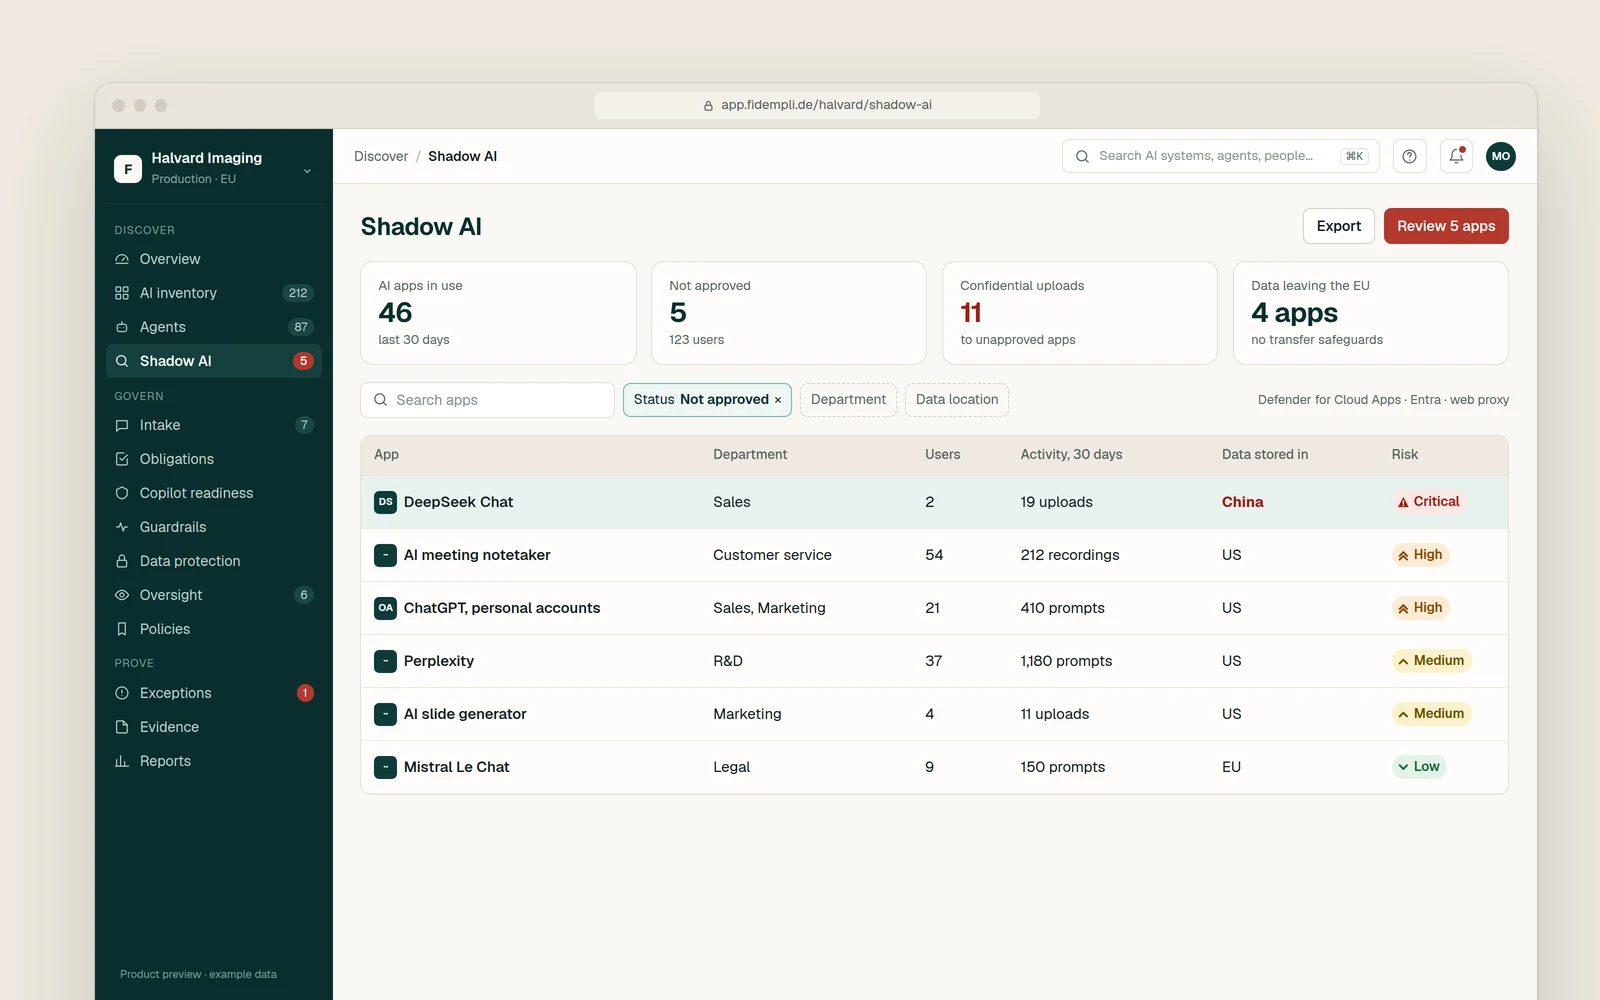
Find out which AI apps staff use without approval, and what data they send.

  • Discovery from Defender for Cloud Apps, Entra sign-ins and your web proxy
  • Users, uploads and data location for each unapproved app
  • Approve, move users to an approved tool or block, with the decision recorded
Learn more: Shadow AI
Shadow AI view ranking unapproved AI apps by risk, with users, activity and data location
Product preview with example data
Discover

Agent governance

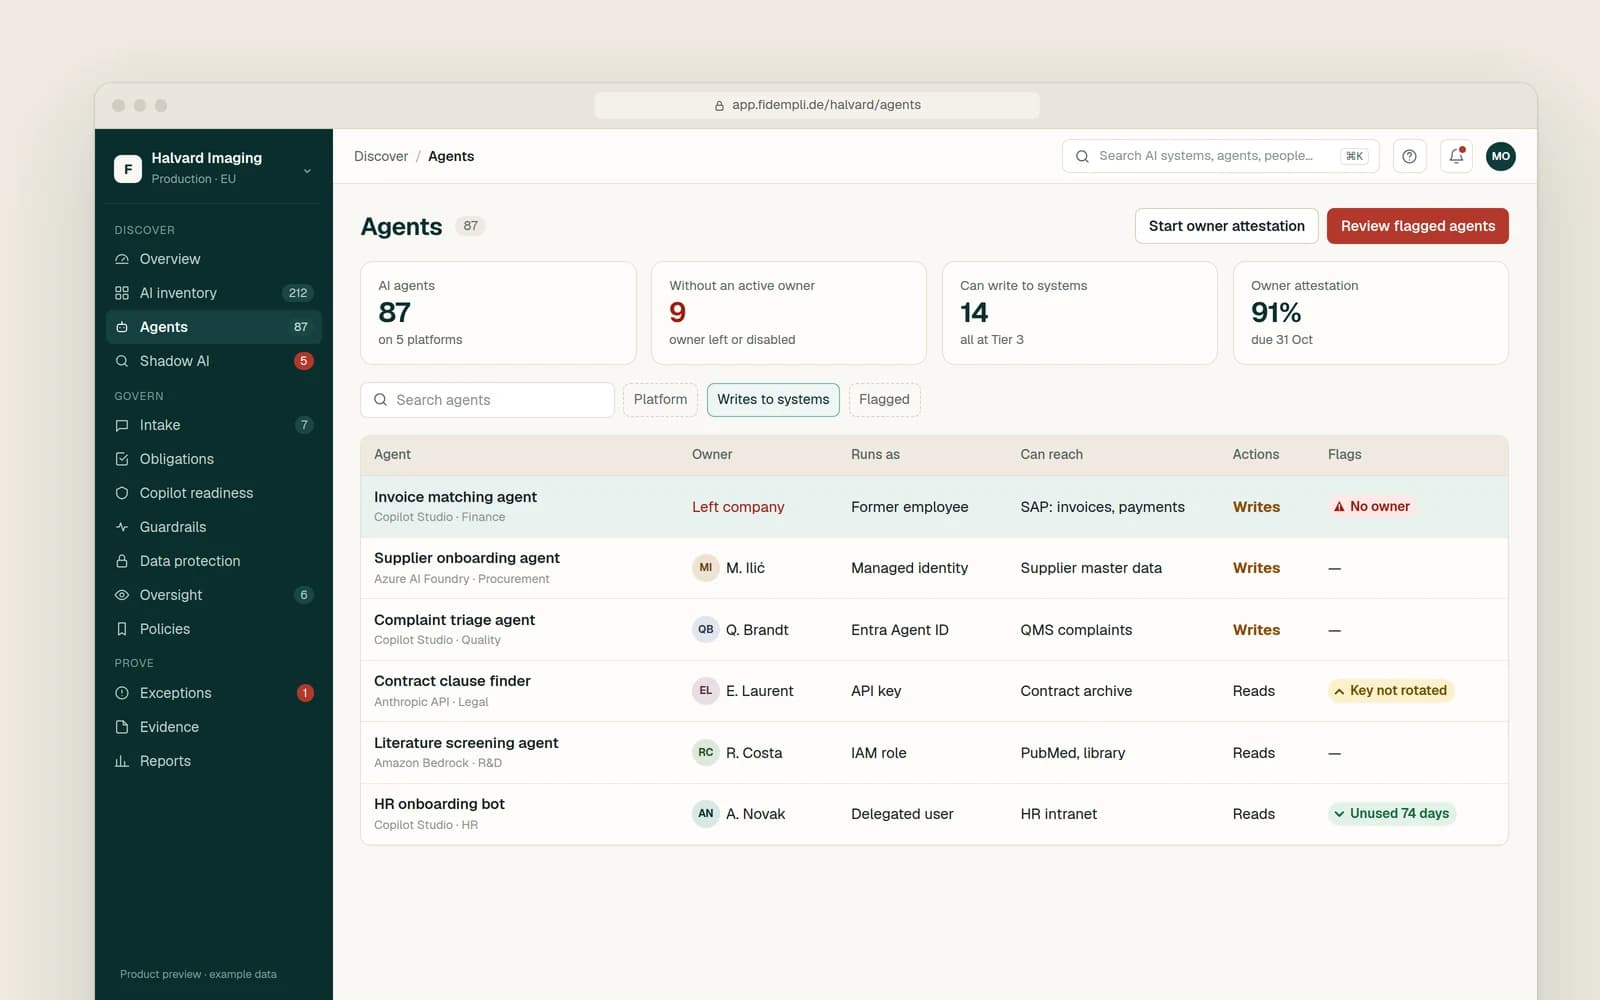
Every AI agent has an owner, its own identity and only the access it needs.

  • Agents from Copilot Studio, Azure AI Foundry, ChatGPT Enterprise, Amazon Bedrock and Anthropic
  • Flags agents whose owner left, that run as a person or that can write to business systems
  • Owner attestation on a schedule you set
Learn more: Agent governance
Agents across five platforms with owner, identity, reach, actions and flags
Product preview with example data

02 · Govern

Decide on each AI use in proportion to its risk.

One intake for every new AI use. Each request is classified, routed to the right reviewers and mapped to the obligations that apply, with the evidence attached.

Learn more: Govern
Govern

Intake and approval

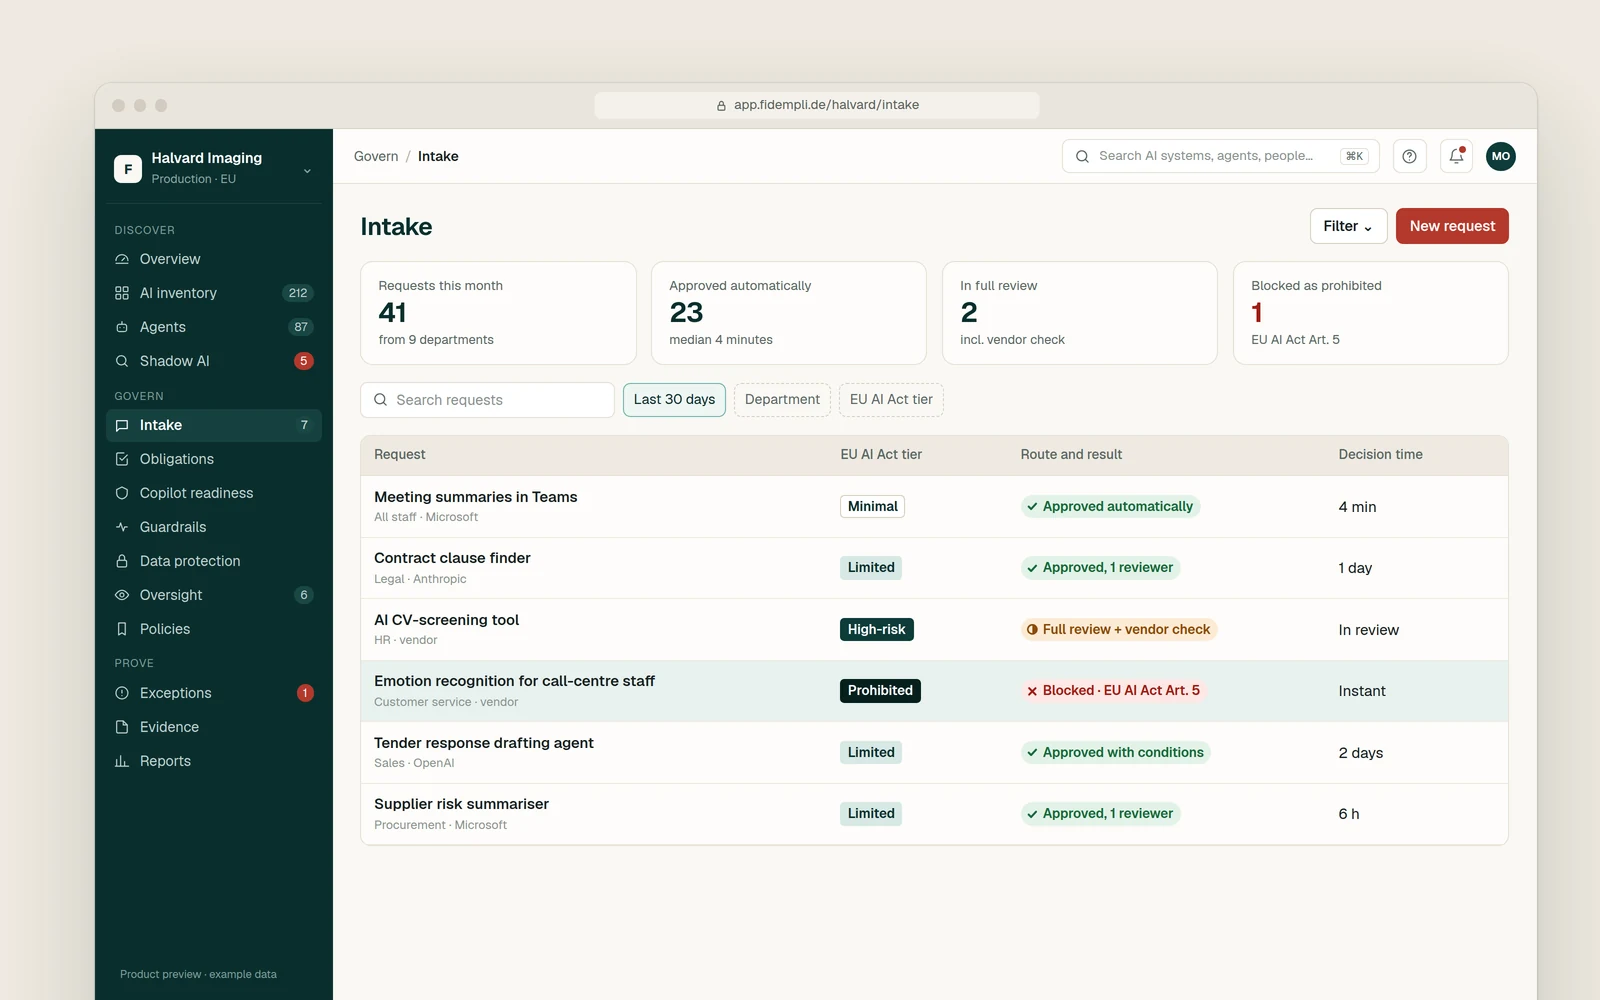
Approve low-risk AI in minutes, review high-risk AI properly, and block prohibited uses outright.

  • One intake form for new AI use cases, tools and agents
  • Automatic classification by EU AI Act tier, with the reasoning recorded
  • Vendor review and approvals routed by risk; prohibited practices cannot be approved
Learn more: Intake and approval
Intake queue with requests routed by EU AI Act tier, from automatic approval to a blocked prohibited use
Product preview with example data
Govern

Compliance mapping

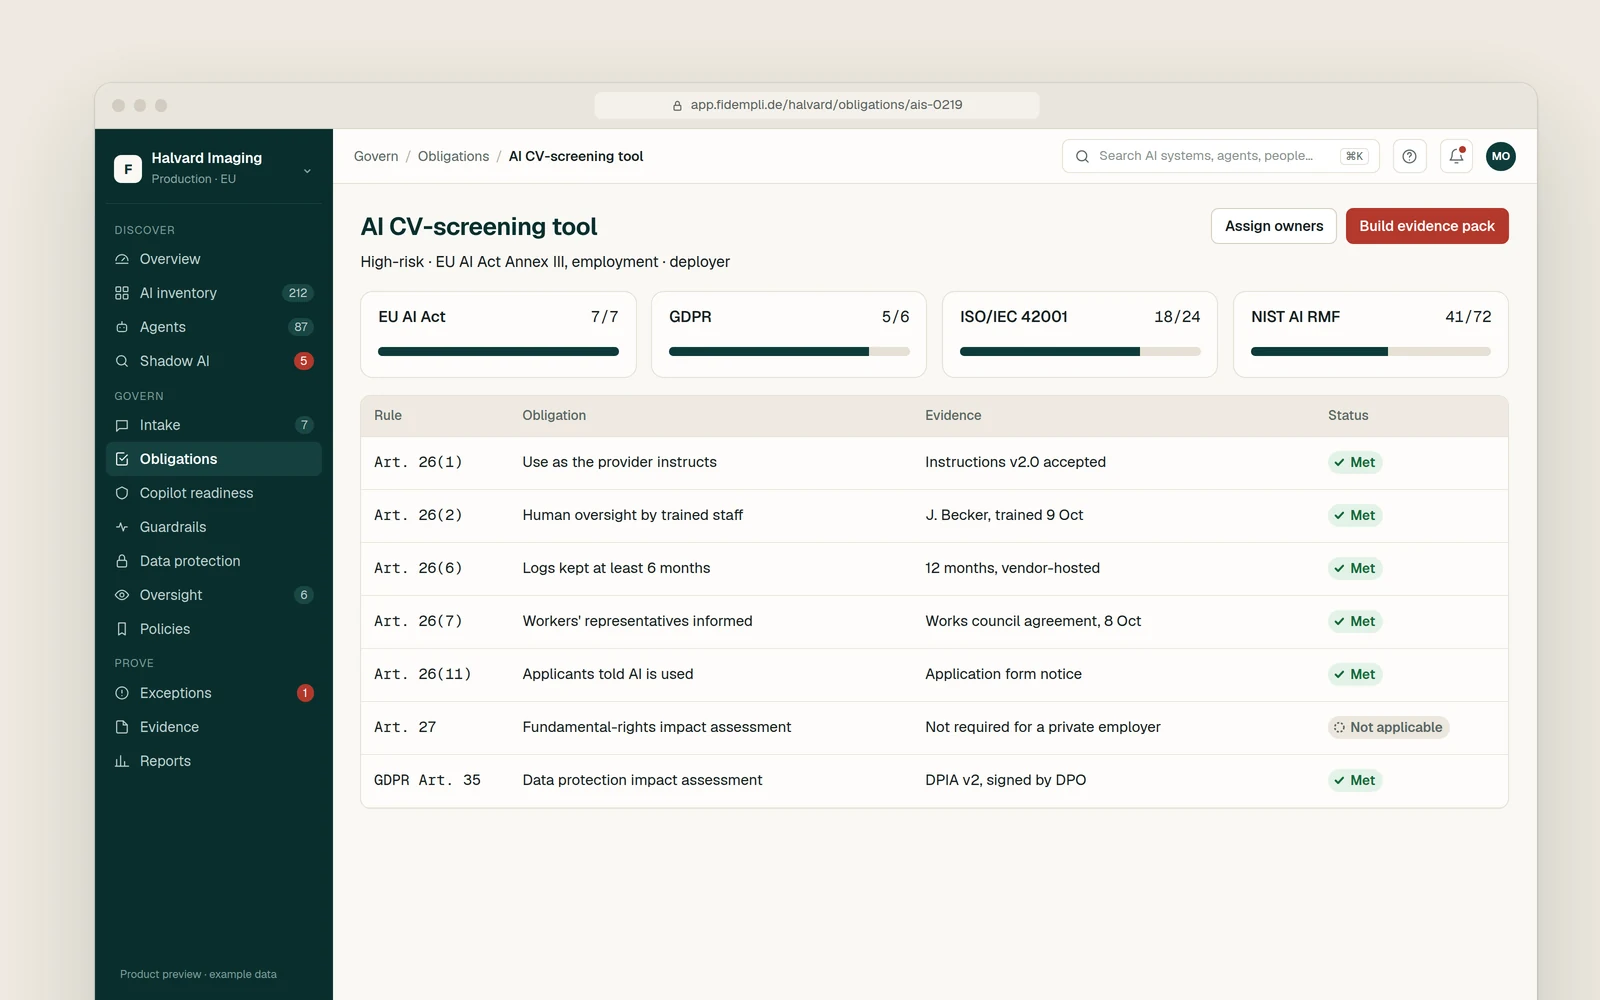
Map each AI use to its EU AI Act duties, plus GDPR, ISO/IEC 42001 and NIST AI RMF, with evidence.

  • Obligations per AI system, with owner, status and evidence
  • Coverage per framework and per AI system
  • "Not applicable" recorded with the reason
Learn more: Compliance mapping
Obligations for a high-risk HR tool with coverage per framework and evidence per obligation
Product preview with example data
Govern

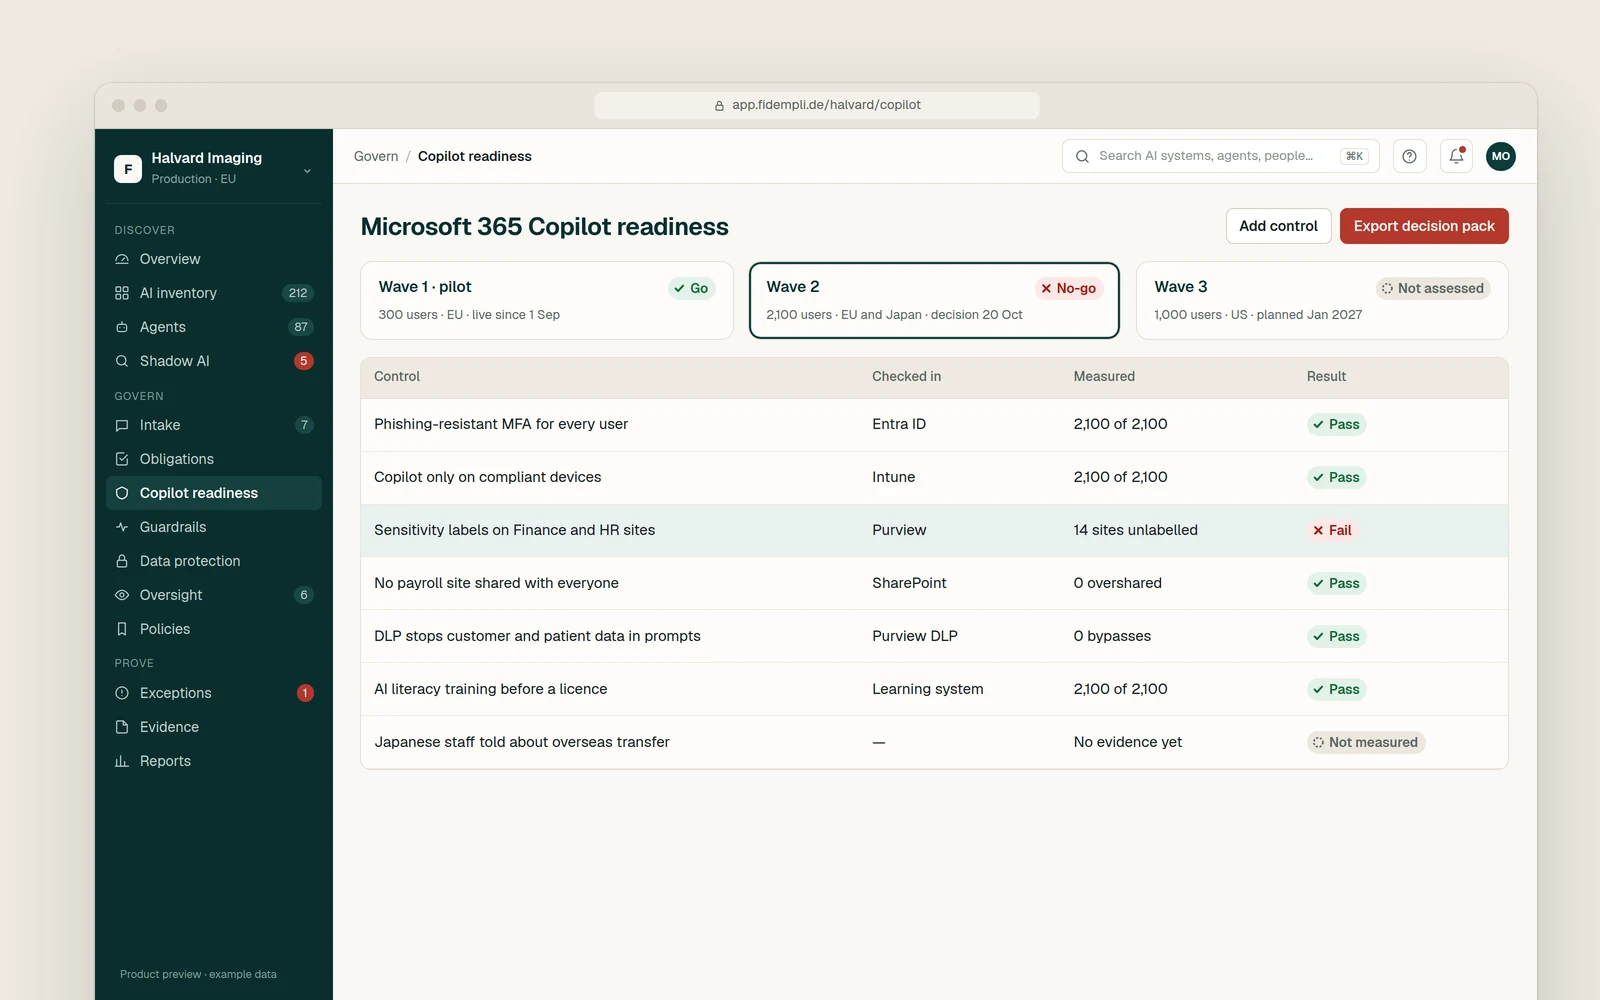
Copilot readiness

Know from live tenant data whether Microsoft 365 Copilot is safe to switch on.

  • Controls checked against Entra ID, Intune, Purview and SharePoint
  • Go or no-go per rollout wave
  • "Not measured" never counts as a pass
Learn more: Copilot readiness
Microsoft 365 Copilot rollout gate with controls checked in Entra ID, Intune, Purview and SharePoint
Product preview with example data

03 · Protect

Keep sensitive data and high-stakes actions under control.

Guardrails sit between your people, your agents and every AI model. Personal and health data is removed or pseudonymised first, and the decisions that matter wait for a person.

Learn more: Protect
Protect

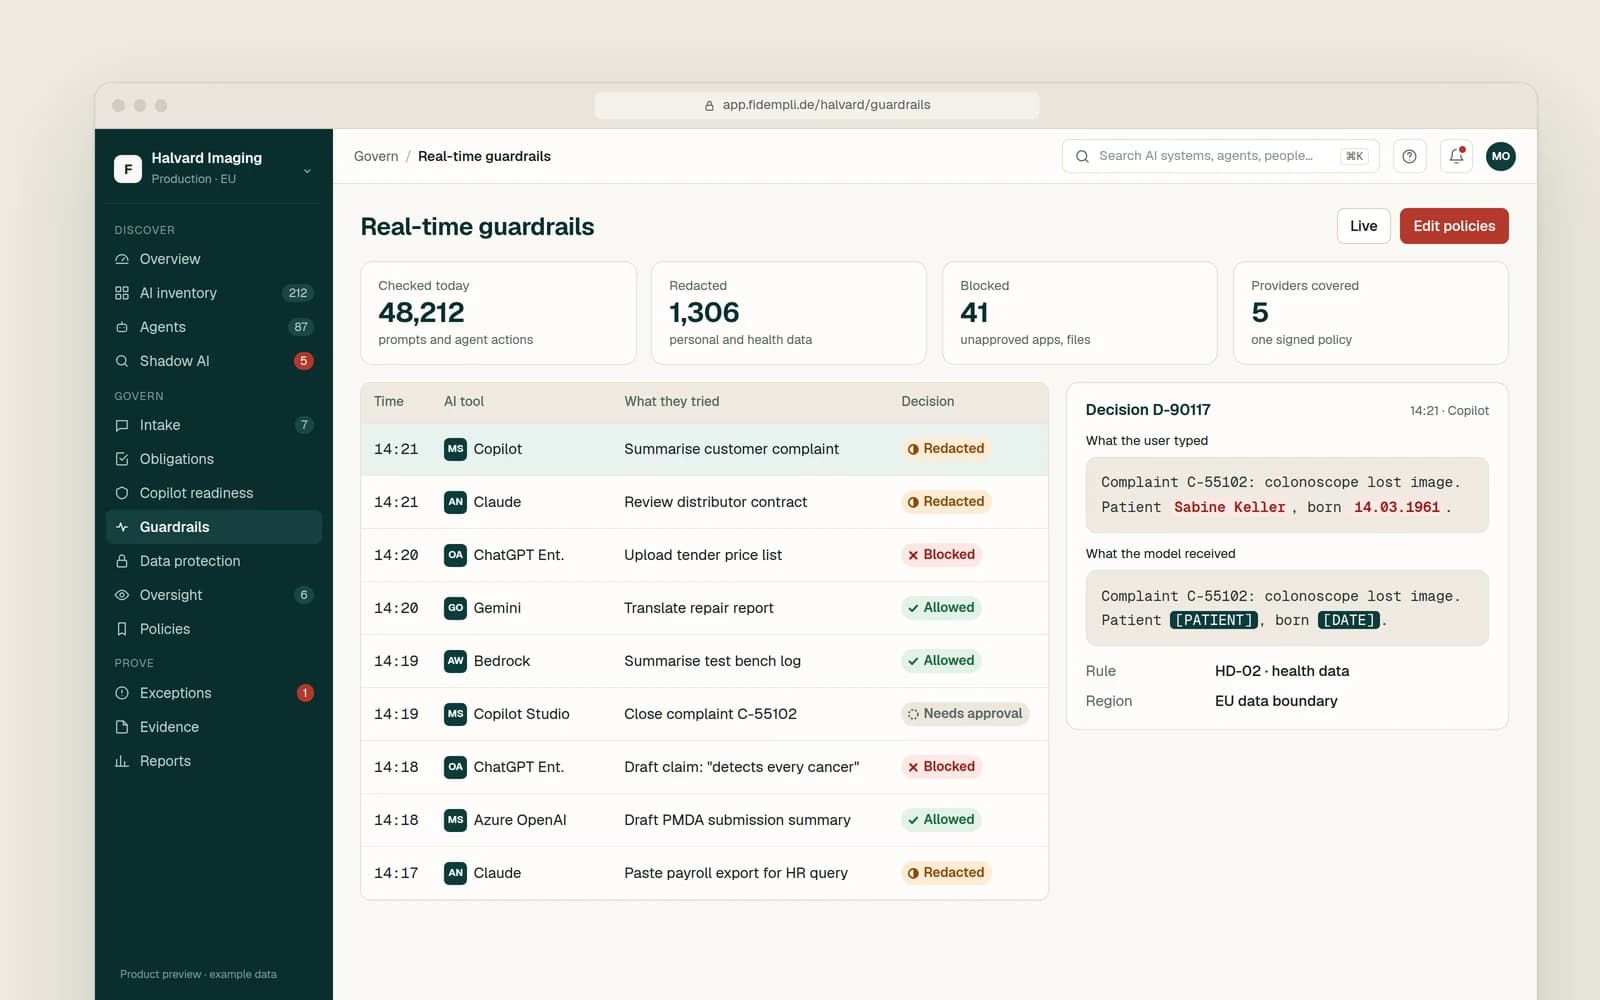
Real-time guardrails

Stop personal and confidential data reaching any AI model, with one policy for every provider.

  • Every prompt and agent action checked before it reaches the model
  • Allow, redact, block or send to a person, with the reason recorded
  • One signed policy for Microsoft, OpenAI, Anthropic, Google and AWS
Learn more: Real-time guardrails
Live guardrail decisions across AI tools with one prompt shown before and after redaction
Product preview with example data
Protect

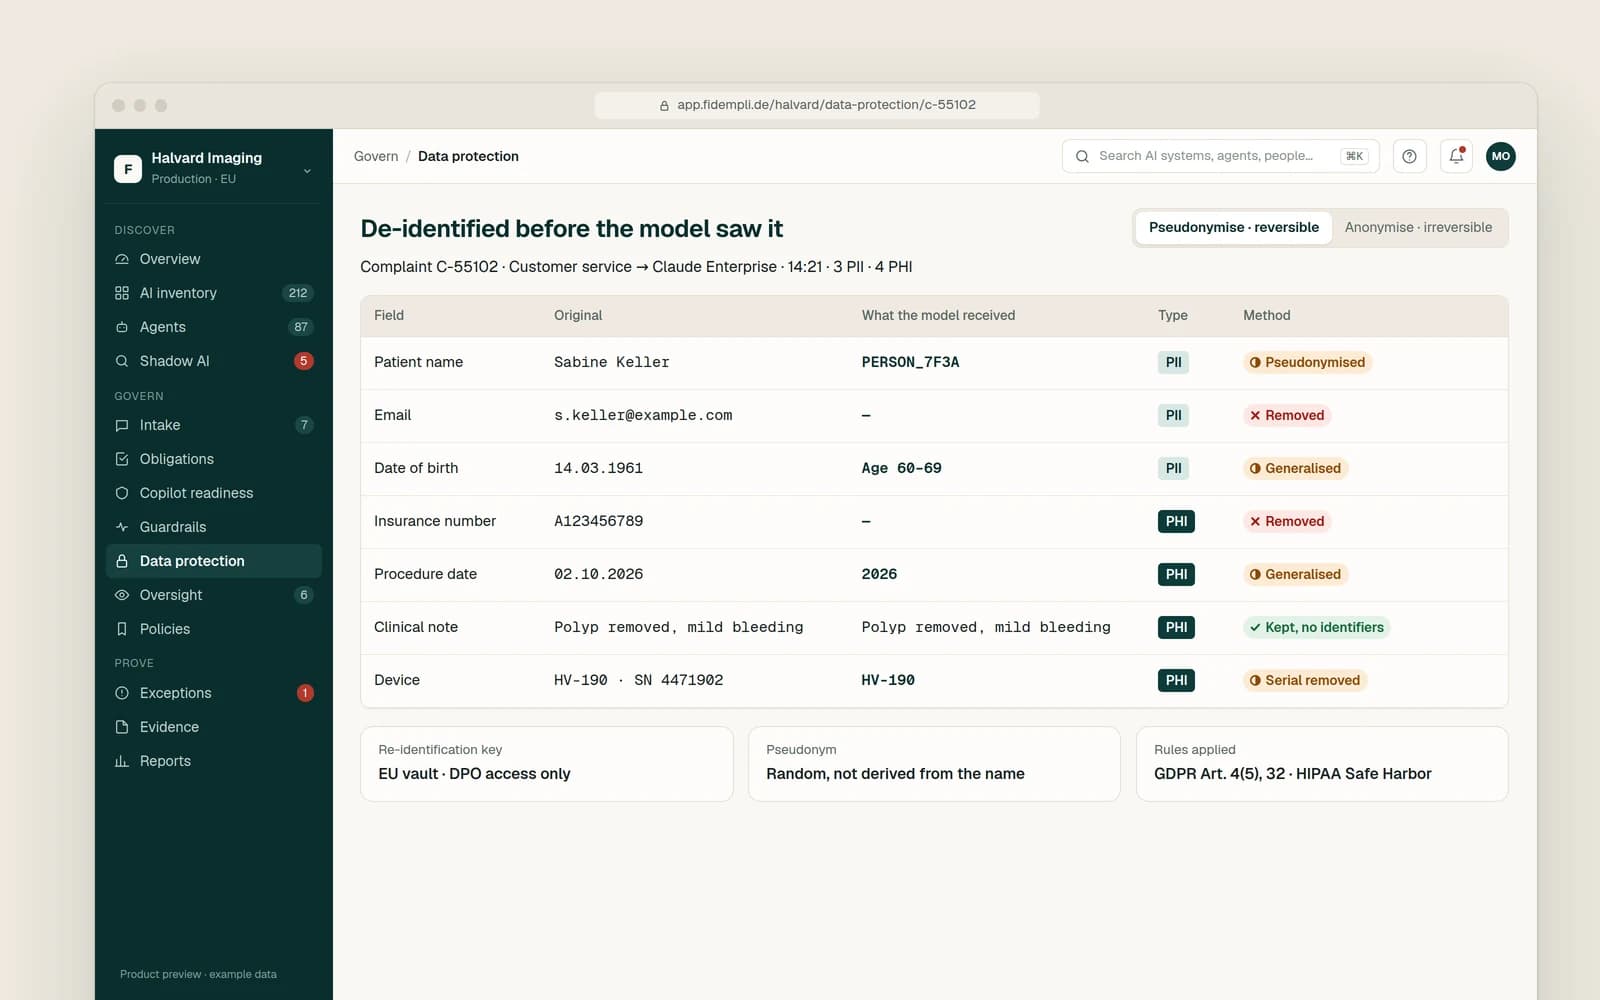
PII and PHI protection

Personal and health data is anonymised or pseudonymised before any AI model sees it, with the key kept in the EU.

  • Finds names, contact details, insurance numbers, dates and serial numbers
  • Pseudonymise reversibly or anonymise irreversibly, field by field
  • Re-identification keys stay in an EU vault with access for the data protection officer only
Learn more: PII and PHI protection
A customer complaint de-identified field by field before it was sent to an AI model
Product preview with example data
Protect

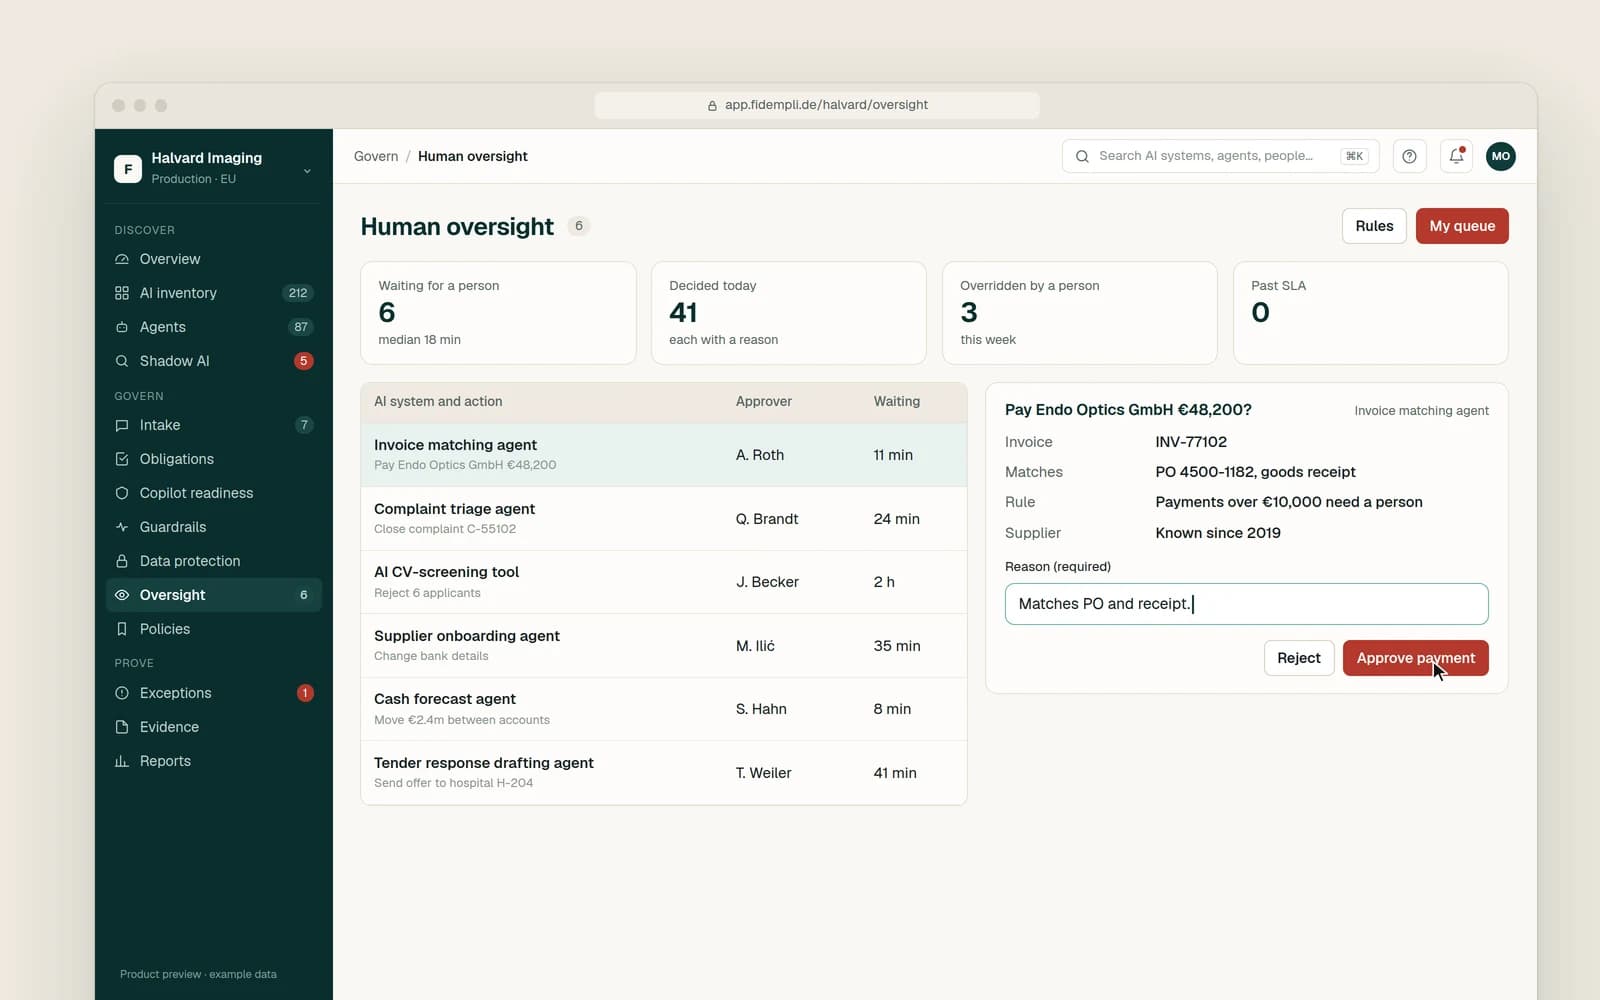
Human oversight

High-stakes AI decisions and agent actions wait for a named person, who records why.

  • Payments, record changes and rejections above your thresholds wait for a person
  • Every approval or rejection needs a reason, kept in the audit trail
  • Queues, approvers and waiting times for every type of decision
Learn more: Human oversight
Queue of agent actions waiting for a person, with a payment open for approval
Product preview with example data

04 · Prove

Show auditors, authorities and the board what happened.

Every decision is recorded with the policy version, the reason and the people involved. Exceptions are watched by live checks, and evidence is ready when someone asks.

Learn more: Prove
Prove

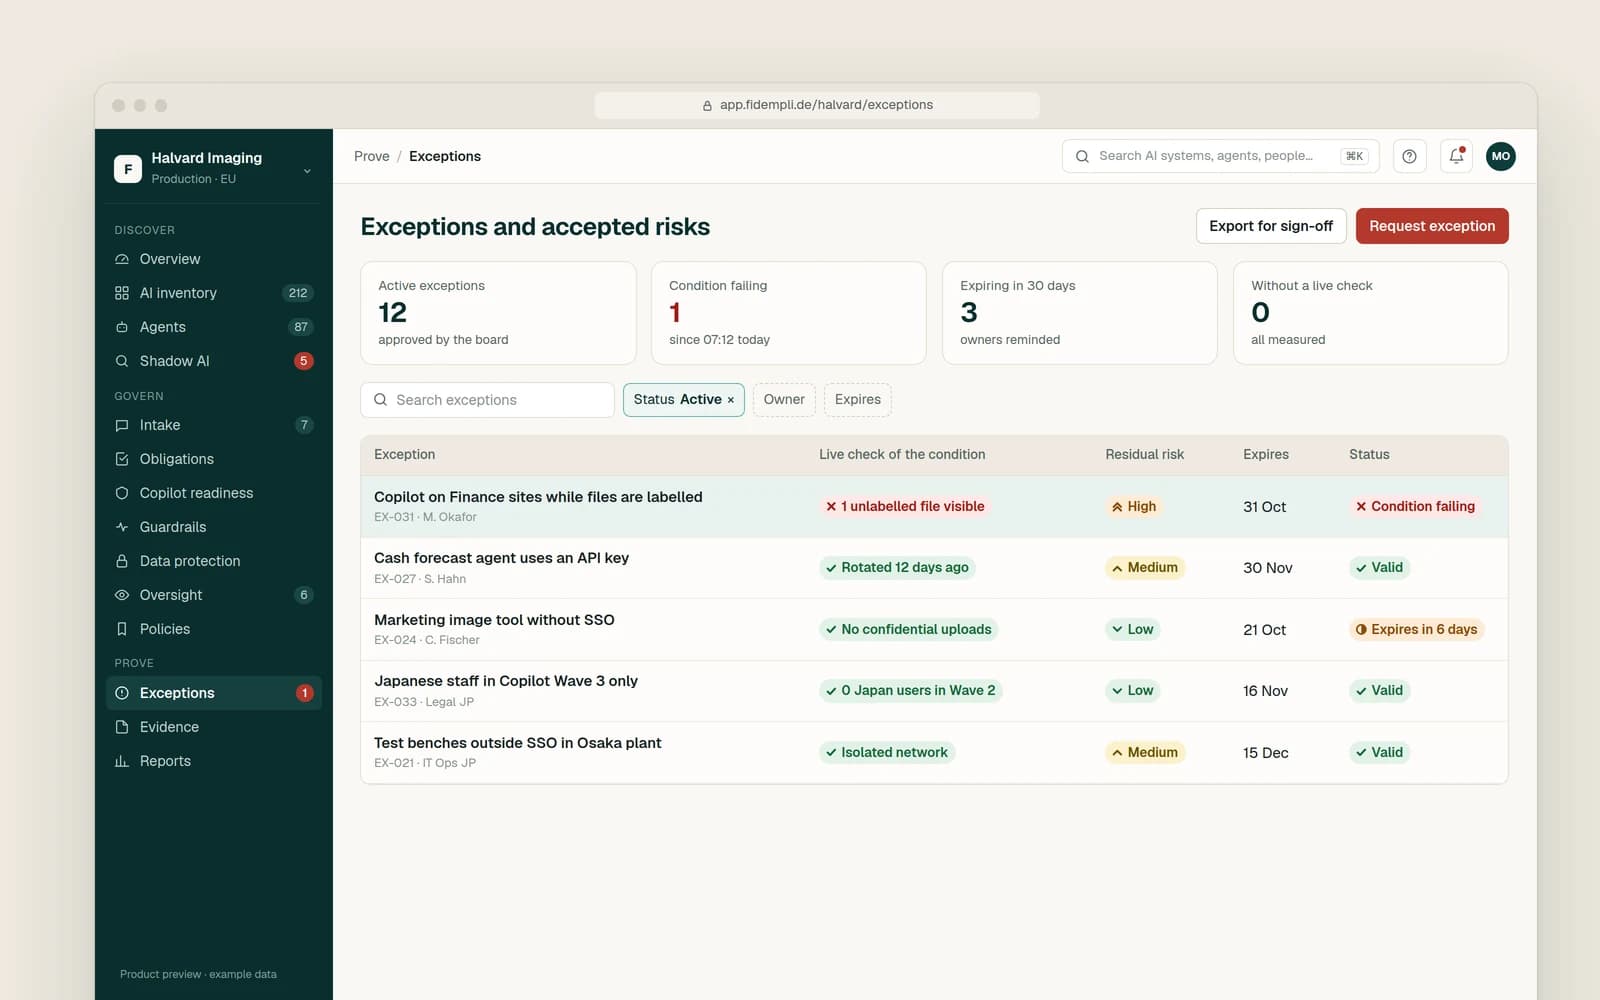
Exceptions and accepted risk

Every accepted risk has an owner, an expiry date and a live check behind it.

  • Owner, compensating control, residual risk and expiry for each exception
  • A live check watches the condition behind each exception
  • Owners are reminded before an exception expires
Learn more: Exceptions and accepted risk
Exception register with live checks, where one exception's condition is failing
Product preview with example data
Prove

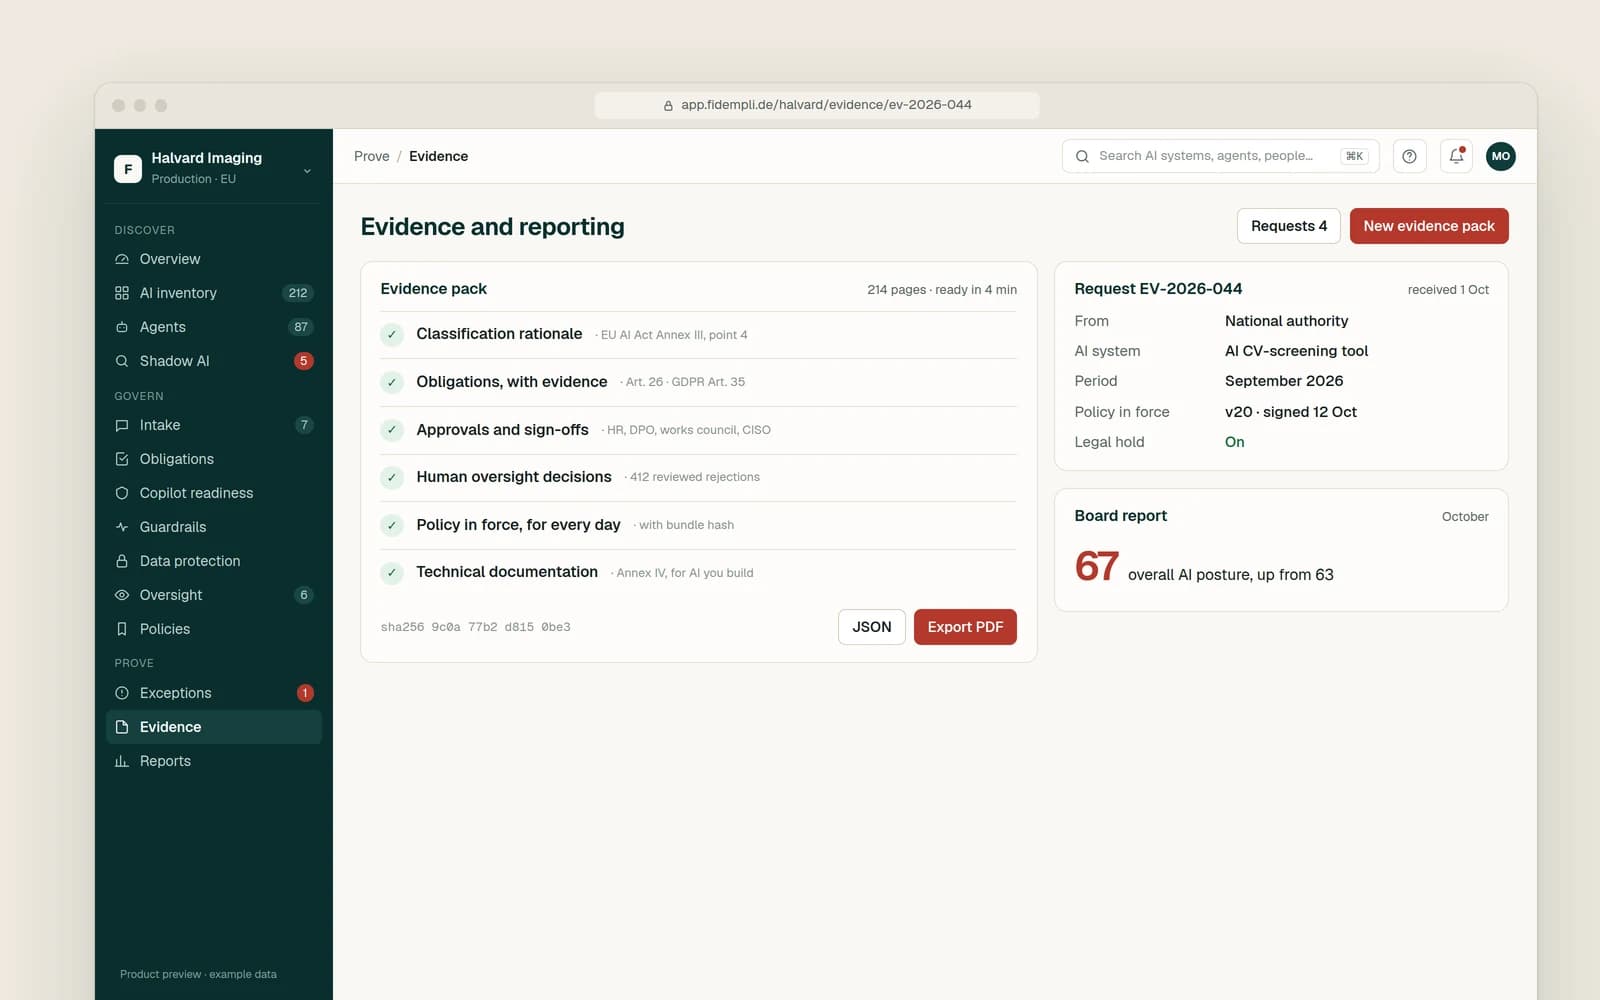
Evidence and reporting

Answer auditors and authorities in minutes, and give the board one AI risk view.

  • Evidence packs with classification, obligations, approvals and policy versions
  • Policy in force for any date, with signatures
  • Board report built from decision logs, not self-assessment
Learn more: Evidence and reporting
Evidence pack for an authority request next to the request details and the board posture score
Product preview with example data

Deployment and data sovereignty

Run it where your regulator expects it.

The same platform in different deployment modes, with control over keys and data location.

SaaS, EU region

Fastest start. EU-hosted in Frankfurt.

At launch

Private cloud

In your own cloud tenant.

At launch

On-premises

In your own data centre.

At launch

Air-gapped

No outbound connection at all.

At launch

Key control

Fidempli-managed keys At launchBring your own key At launchYour HSM At launch
Deployment options in detail

See it on your own AI estate.

The platform launches in December 2026. Design partners start earlier.