The Fidempli AI governance platform launches in December 2026. Design-partner places are open.Apply now →
Fidempli

AI Governance, Privacy & AI Security

Find the weaknesses in your AI before attackers do.

Tested AI applications, prioritised findings with fixes, and controls that keep prompt injection and data leakage in check.

The problem

AI applications are attacked through language, not only code. A hidden instruction in an email, a web page or a shared document can make a copilot or agent leak data or take actions nobody intended.

Agents now read mailboxes, query databases and call APIs with real permissions. RAG applications can return documents the user should never see. Classic penetration tests do not cover these risks, and most AI applications go live without a dedicated test.

What we do

AI Security & Red Teaming

  1. Model the threats

    We map each AI application: models, prompts, data sources, tools, identities and users, and identify how it can be attacked and what an attacker could reach.

  2. Review architecture and permissions

    We check agent identities, connector permissions, retrieval access control and output handling against least privilege and the OWASP Top 10 for LLM Applications.

  3. Test and red team

    We attack the application with direct and indirect prompt injection, jailbreaks, system prompt extraction, data leakage and attempts to misuse tools and agent actions.

  4. Test RAG and connected data

    We test whether retrieval respects user permissions, whether poisoned documents change answers and whether sensitive data leaks through the index.

  5. Fix and retest

    We prioritise findings by risk, help your teams fix them and retest, so you know the fix works.

  6. Put guardrails in place

    We set up input and output filters, human approval for high-impact agent actions, logging and monitoring for the applications that need them.

How we deliver

Consulting · Professional services · Managed services

Consulting

Our security consultants model the threats, review the architecture and advise on secure design for copilots, agents and AI applications.

Professional services

Our testers run the red teaming in your environment, and our engineers implement fixes, guardrails and permission changes with your teams.

Managed services

We retest AI applications after changes and on a schedule, and monitor guardrails and agent permissions as a managed service.

AI automation in this service

  • Automated prompt injection and jailbreak test runs from maintained attack libraries, with results reviewed by a tester
  • Automated review of agent and connector permissions from Entra ID, Copilot Studio and cloud AI platforms
  • Automated retests of fixed findings after each change to prompts, models or data sources

What you get

  • Threat model per AI application
  • Test report with findings rated by risk and mapped to the OWASP Top 10 for LLM Applications
  • Remediation plan with concrete fixes
  • Retest results
  • Guardrail and permission recommendations per application

Frameworks

  • OWASP LLM Top 10
  • ISO/IEC 27001
  • EU AI Act

In detail

What we test

  • Microsoft 365 Copilot and Copilot Studio agents
  • Chatbots and AI assistants
  • RAG applications
  • AI agents with tool and API access
  • AI features in SaaS and custom applications

OWASP Top 10 for LLM Applications, examples

  • Prompt injection
  • Sensitive information disclosure
  • Improper output handling
  • Excessive agency
  • System prompt leakage
  • Vector and embedding weaknesses

Application security around the model

  • Code review and analysis
  • Static application security testing (SAST)
  • Dynamic application security testing (DAST)
  • Software composition analysis
  • Penetration testing

Platform

After the project, the Fidempli platform keeps it running

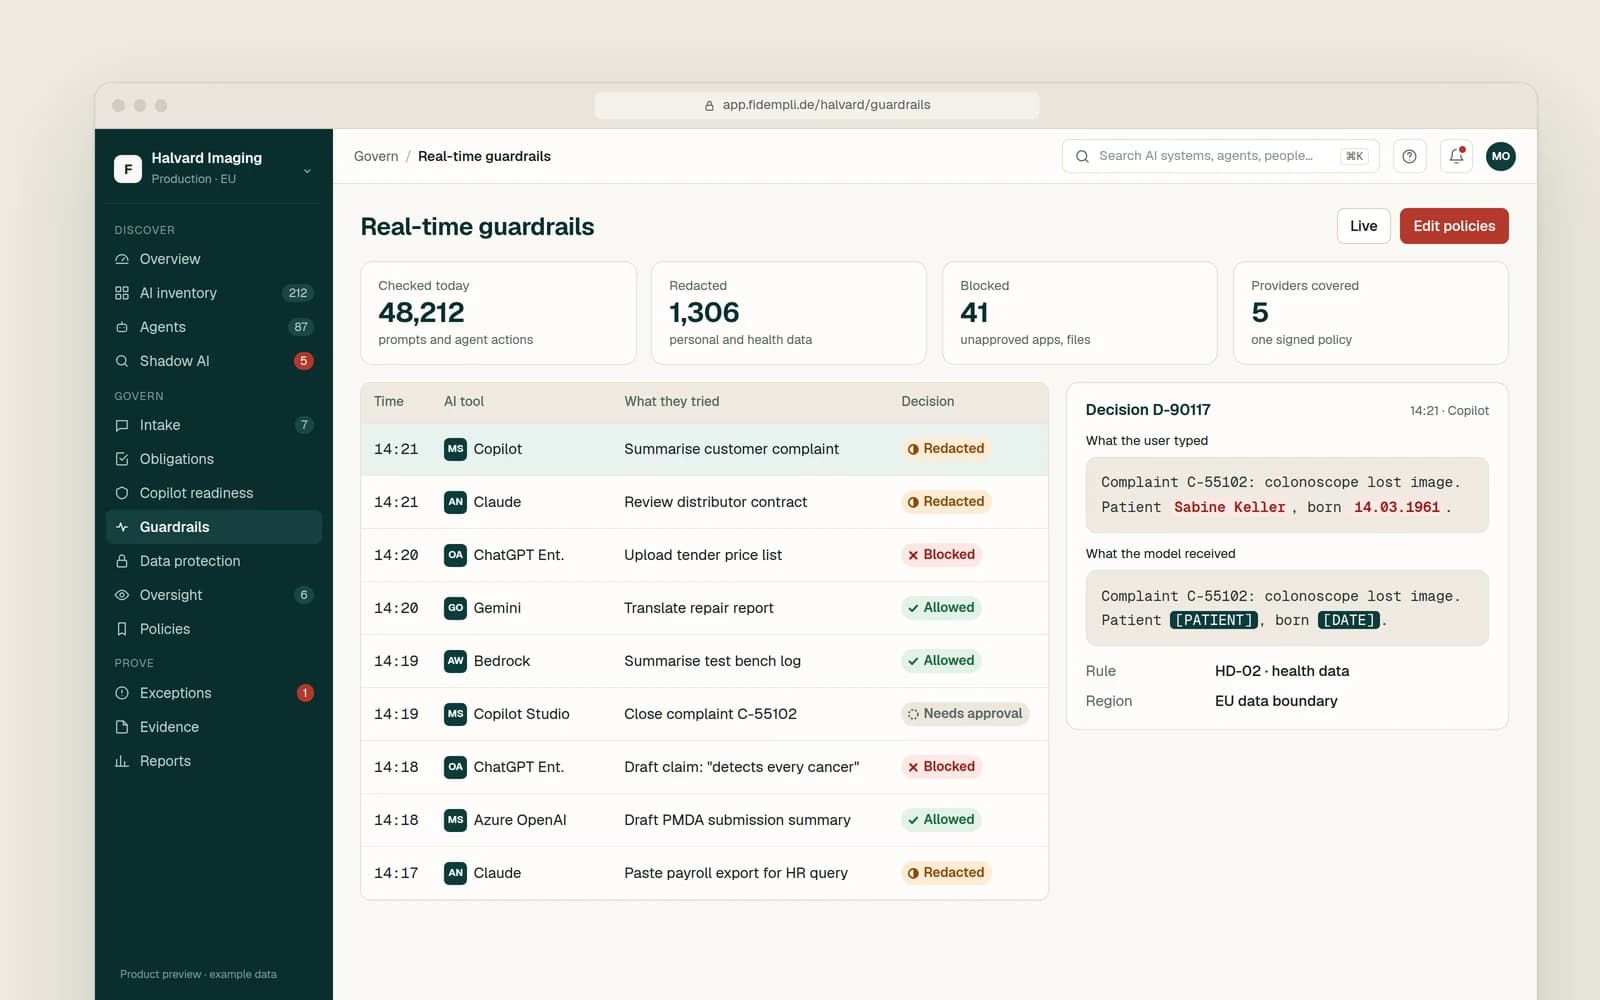
From December 2026 the Fidempli platform applies the guardrails live: every prompt and agent action is checked before it reaches the model, and high-impact actions wait for a person.

Explore the platform
Live guardrail decisions across AI tools with one prompt shown before and after redaction
Product preview with example data

Frequently asked questions

How is this different from a penetration test?

A penetration test looks at infrastructure and application code. AI red teaming also attacks the model's behaviour, its prompts, its data sources and the actions agents can take. We combine both where it makes sense.

Can you test Microsoft 365 Copilot?

Yes. We test how Copilot and Copilot Studio agents handle indirect prompt injection, oversharing and data from connected sources, within the limits of Microsoft's terms for testing.

Do you test in production?

We prefer a test environment that mirrors production. Where we test in production, we agree scope, test accounts and limits with you in advance.

What is the OWASP Top 10 for LLM Applications?

A widely used list of the most important security risks for applications built on large language models, from prompt injection to excessive agency. We use it to structure tests and findings.

Does the EU AI Act require security testing?

For high-risk AI systems, the Act requires an appropriate level of accuracy, robustness and cybersecurity. Independent of regulation, any AI with access to data or systems should be tested before it goes live.

More services in this pillar

Start with a 30-minute AI risk conversation.

A senior consultant replies within one business day. Or join the 3–5 design partners shaping the platform before launch.