The Fidempli AI governance platform launches in December 2026. Design-partner places are open.Apply now →
Fidempli

Cybersecurity & Privacy

Cloud and application security, from strategy to 24×7 operations.

Cloud platforms and applications that are configured securely, tested and watched.

The problem

Most cloud incidents start with a misconfiguration: a public storage bucket, an over-privileged role, a missing log. With several cloud providers and many teams deploying, settings drift faster than anyone checks them.

Applications add their own weaknesses through custom code and open-source components. Your AI workloads run on the same platforms, so a weak cloud foundation is also a weak foundation for AI.

What we do

Cloud Security

  1. Assess your cloud and applications

    We review cloud architecture, configuration, identities and logging on AWS, Microsoft Azure, Google Cloud and OpenText, and test your applications for weaknesses.

  2. Set the strategy

    We define your target architecture and operating model, compare on-premises and cloud options, and build the business case and capacity plan.

  3. Test your applications

    We combine code review, SAST, DAST, software composition analysis and penetration testing, and give developers findings they can act on.

  4. Harden and fix

    We fix configuration gaps, tighten identities and network rules and set secure baselines for new workloads, including AI services.

  5. Operate and optimise

    We run and monitor your cloud around the clock, report on consumption, optimise costs and manage your cloud vendors.

How we deliver

Consulting · Professional services · Managed services

Consulting

We assess your cloud architecture and applications and give you a prioritised plan, from strategy and migration to secure baselines.

Professional services

We implement secure configurations, integrate security testing into your delivery pipeline and support migrations in your environment.

Managed services

We run your cloud 24×7: operations, monitoring, consumption reporting, cost optimisation and vendor management.

AI automation in this service

  • Automated configuration checks across AWS, Azure and Google Cloud against your secure baseline, with drift reported to the owning team.
  • Automated SAST, DAST and software composition analysis in the delivery pipeline, with findings triaged and de-duplicated before a person reviews them.
  • Automated consumption reports that flag unused and oversized resources.

What you get

  • Cloud security assessment with prioritised findings
  • Cloud strategy, target architecture and business case
  • Application security test and penetration test reports
  • Secure configuration baselines per cloud platform
  • Monitoring, operations and consumption reports

Frameworks

  • ISO/IEC 27001
  • NIS2
  • DORA
  • GDPR

In detail

Application security consulting

  • Code review and analysis
  • Static application security testing (SAST)
  • Dynamic application security testing (DAST)
  • Software composition analysis
  • Penetration testing

Cloud and hyperscaler consulting

  • AWS
  • Microsoft Azure
  • Google Cloud Platform (GCP)
  • OpenText

Cloud security consulting

  • Cloud strategy and architecture
  • Cloud migration assessment and proofs of concept
  • Maturity assessment and gap analysis
  • Multi-cloud vendor analysis
  • Target operating model: on-premises versus cloud
  • Capacity planning and cost analysis
  • Business case preparation

Managed cloud services

  • 24×7 operation and service management
  • Cloud monitoring
  • Consumption monitoring, reporting and optimisation
  • Vendor relationship management

Platform

After the project, the Fidempli platform keeps it running

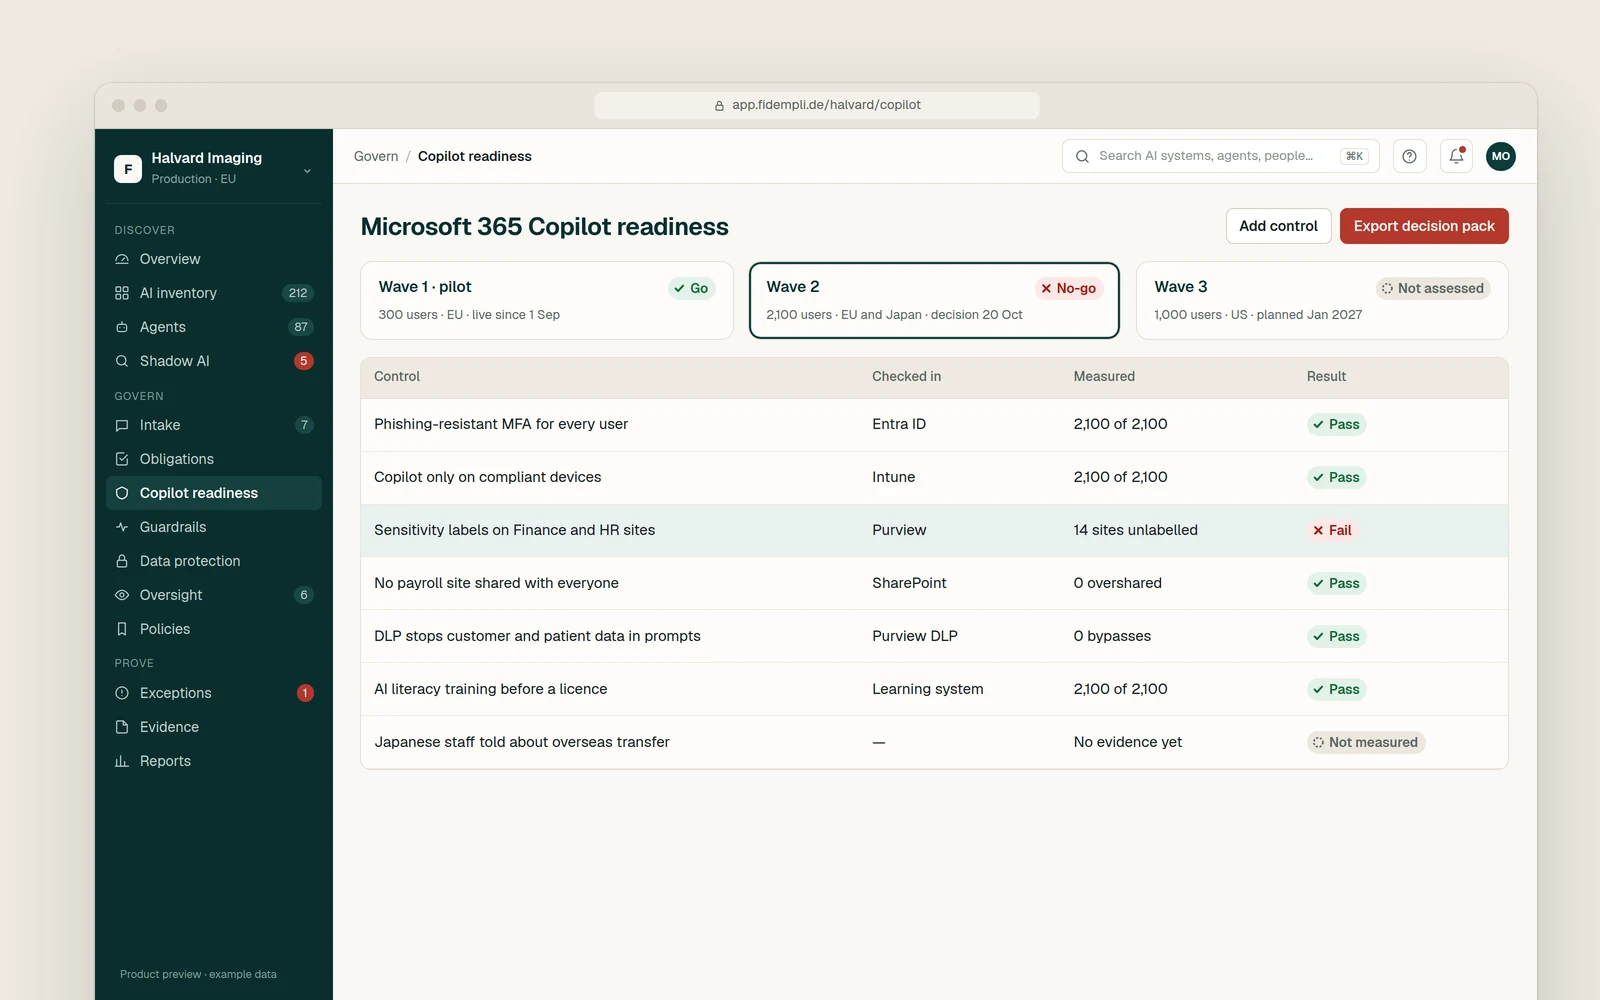
From December 2026, the Fidempli platform connects to Microsoft 365, AWS and Google and keeps track of the AI services running in your cloud, including whether your Microsoft 365 tenant is ready for Copilot.

Explore the platform
Microsoft 365 Copilot rollout gate with controls checked in Entra ID, Intune, Purview and SharePoint
Product preview with example data

Frequently asked questions

Which cloud platforms do you cover?

AWS, Microsoft Azure, Google Cloud Platform and OpenText. Many of our clients use more than one, and we assess them together.

What is the difference between SAST, DAST and penetration testing?

SAST analyses source code without running it. DAST tests the running application from outside. A penetration test is a manual, targeted attack by a specialist that finds weaknesses automated tools miss.

Can you work with our in-house cloud team?

Yes. We can advise your team, implement alongside it or take over operations completely. You decide how much stays in-house.

Do you also secure AI workloads in the cloud?

Yes. AI services run on the same cloud platforms, so we include their identities, network access, logging and data flows in the assessment.

Does cloud security help with NIS2 and DORA?

Both require security in the acquisition, development and operation of ICT systems. Secure baselines, testing and monitoring are part of the evidence you need.

More services in this pillar

Start with a 30-minute AI risk conversation.

A senior consultant replies within one business day. Or join the 3–5 design partners shaping the platform before launch.