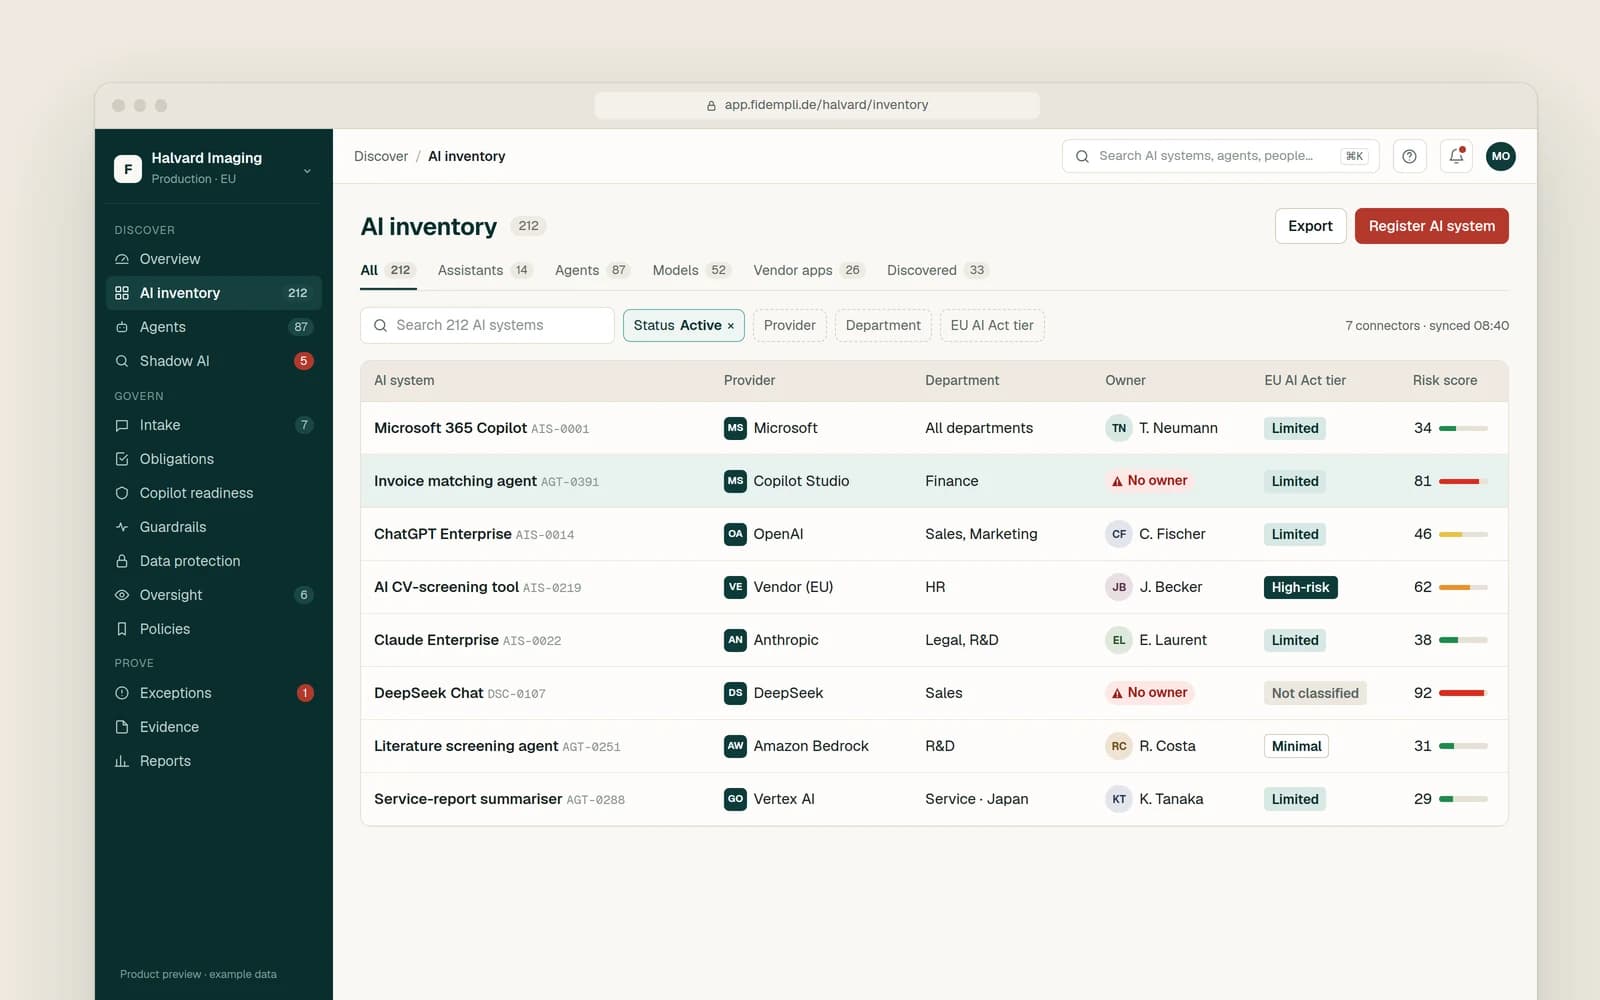
Most organisations cannot say how many AI systems they use. Copilots, chatbots, agents and AI features inside existing software spread across departments, and staff use tools nobody approved, often with customer or employee data.
The EU AI Act has banned certain practices and required AI literacy since February 2025, and GDPR applies to every prompt that contains personal data. Without an inventory, nobody can say which obligations apply, where the risks are or what to fix first.
What we do
AI Readiness Assessment
Agree the scope
We agree the business units and systems in focus, name the contacts on your side and set up read-only access to the data sources we need, such as Microsoft 365, Entra ID and Defender for Cloud Apps.
Build the AI inventory, including shadow AI
We find the AI tools, models, agents and AI features in use, approved or not, and record owner, purpose, users and the data each one touches.
Classify each system under the EU AI Act
For each system we determine your role as provider or deployer and the risk category: prohibited, high-risk, transparency obligations or minimal risk. The reasoning is written down.
Review privacy and security
We check legal basis, the need for a DPIA, data flows and transfers outside the EU, and review identities, permissions, data exposure and guardrails for the systems that matter most.
Prioritise and brief the board
We turn the findings into a roadmap with owners, effort and quick wins, and present it to your management in a form they can decide on.
Packages
Essentials3 weeksFor organisations that need a clear picture of their AI quickly.
AI inventory incl. shadow AI
EU AI Act classification per system
Privacy and security review of the main AI systems
Roadmap and management summary
Price [Price]
Standard4–5 weeksFor organisations with several copilots, agents or AI applications in use.
Everything in Essentials
Privacy review in depth, incl. DPIA screening and data transfers
Security review of identities, agent permissions and data exposure
Microsoft 365 Copilot readiness check
Roadmap with owners, effort and board briefing
Price [Price]
Standard + Red Team5–6 weeksFor organisations that build or run their own AI applications, agents or RAG systems.
Everything in Standard
AI security testing (red teaming) of selected AI systems
Prompt injection and jailbreak tests
Data leakage tests, incl. RAG and connected data sources
Findings mapped to the OWASP Top 10 for LLM Applications
Price [Price]
The assessment fee is credited against a Fidempli platform subscription.
How we deliver
Consulting · Professional services · Managed services
Consulting
Our consultants run the assessment with your IT, security, data protection and legal teams and give you an independent view of where you stand.
Professional services
Where a finding needs a quick fix, such as blocking a risky AI app or tightening Copilot sharing settings, our engineers implement it in your environment.
Managed services
After the assessment, we keep the inventory and classifications current as a managed service, so the result does not go out of date.
AI automation in this service
Automated discovery of AI apps and agents from Microsoft 365, Entra ID sign-in and Defender for Cloud Apps data, not questionnaires alone
Automated EU AI Act pre-classification of each system, reviewed and confirmed by a consultant
Automated checks of identity, sharing and data loss prevention settings that affect Microsoft 365 Copilot
What you get
AI inventory with owner, purpose, provider and data for every system, including shadow AI
EU AI Act classification per system, with your role and the reasoning
Privacy and security findings, rated by risk
Prioritised roadmap with owners, effort and quick wins
Management summary for the board
Frameworks
EU AI Act
GDPR
OWASP LLM Top 10
ISO/IEC 42001
Platform
After the project, the Fidempli platform keeps it running
The inventory and classifications load into the Fidempli platform when it launches in December 2026. Live connectors then keep them current, and new AI uses go through intake instead of slipping past.
A sponsor, contacts in IT, security, data protection and the business units, and read-only access to the data sources in scope. We agree the details in the scoping call.
How do you find shadow AI?
We analyse sign-in, cloud app and proxy data to see which AI apps staff actually use, and combine it with short interviews in the business units.
Which package fits us?
Essentials gives a fast, complete picture. Standard adds depth on privacy, permissions and Copilot. Standard + Red Team adds hands-on security testing for AI applications and agents you build or run yourself.
Is the EU AI Act classification final?
We classify each system against the Act and record the reasoning, so your legal team can review and confirm it. Borderline cases are marked as such.
What happens after the assessment?
You can work through the roadmap yourself, with our professional services, or with us running it as a managed service. The results also form the starting point in the Fidempli platform.