Most organisations manage AI risk case by case. One team runs a review, another writes a policy, and nobody can show how decisions are made across the company or who owns them.
ISO/IEC 42001:2023 sets out what an AI management system needs: scope, roles, risk and impact assessment, controls and records. Customers, auditors and boards increasingly ask for it. Building it on paper alone leaves you with documents that drift away from what is actually running.
What we do
AI Risk Management & ISO/IEC 42001
Scope and gap analysis
We define the scope of your AI management system and compare your current practice with ISO/IEC 42001 and the NIST AI RMF.
AI risk framework
We design your risk and impact assessment method, risk criteria and treatment options, aligned with the Govern, Map, Measure and Manage functions of the NIST AI RMF.
Policies and roles
We write your AI policy and supporting procedures and set roles, responsibilities and approval paths, building on an existing ISO/IEC 27001 system where you have one.
Build the AIMS
We select and document the Annex A controls, prepare the Statement of Applicability and set up the records the standard requires.
Internal audit and management review
We run an internal audit against ISO/IEC 42001, support your first management review and track corrective actions.
Certification support
We prepare you for the stage 1 and stage 2 audits by an accredited certification body and support you during them. We do not certify.
How we deliver
Consulting · Professional services · Managed services
Consulting
We assess your current AI risk practice against ISO/IEC 42001 and the NIST AI RMF and give you a prioritised roadmap.
Professional services
We build the framework, policies, controls and records with your teams and take you through internal audit to certification.
Managed services
We run the AI management system with you: risk reviews, internal audits, management review input and surveillance audit preparation.
AI automation in this service
Automated gap analysis that maps your existing policies and ISO/IEC 27001 controls to ISO/IEC 42001 clauses and Annex A controls.
Automated pre-fill of AI risk and impact assessments from the AI inventory and intake records.
Automated evidence collection for internal audits, with each record linked to the control it supports.
What you get
Gap analysis against ISO/IEC 42001 and the NIST AI RMF
AI risk and impact assessment method
AI policy, procedures and role descriptions
Statement of Applicability with selected Annex A controls
AI risk register with owners and treatment plans
Internal audit report and corrective action plan
Certification readiness checklist
Frameworks
ISO/IEC 42001
NIST AI RMF
EU AI Act
ISO/IEC 27001
GDPR
Platform
After the project, the Fidempli platform keeps it running
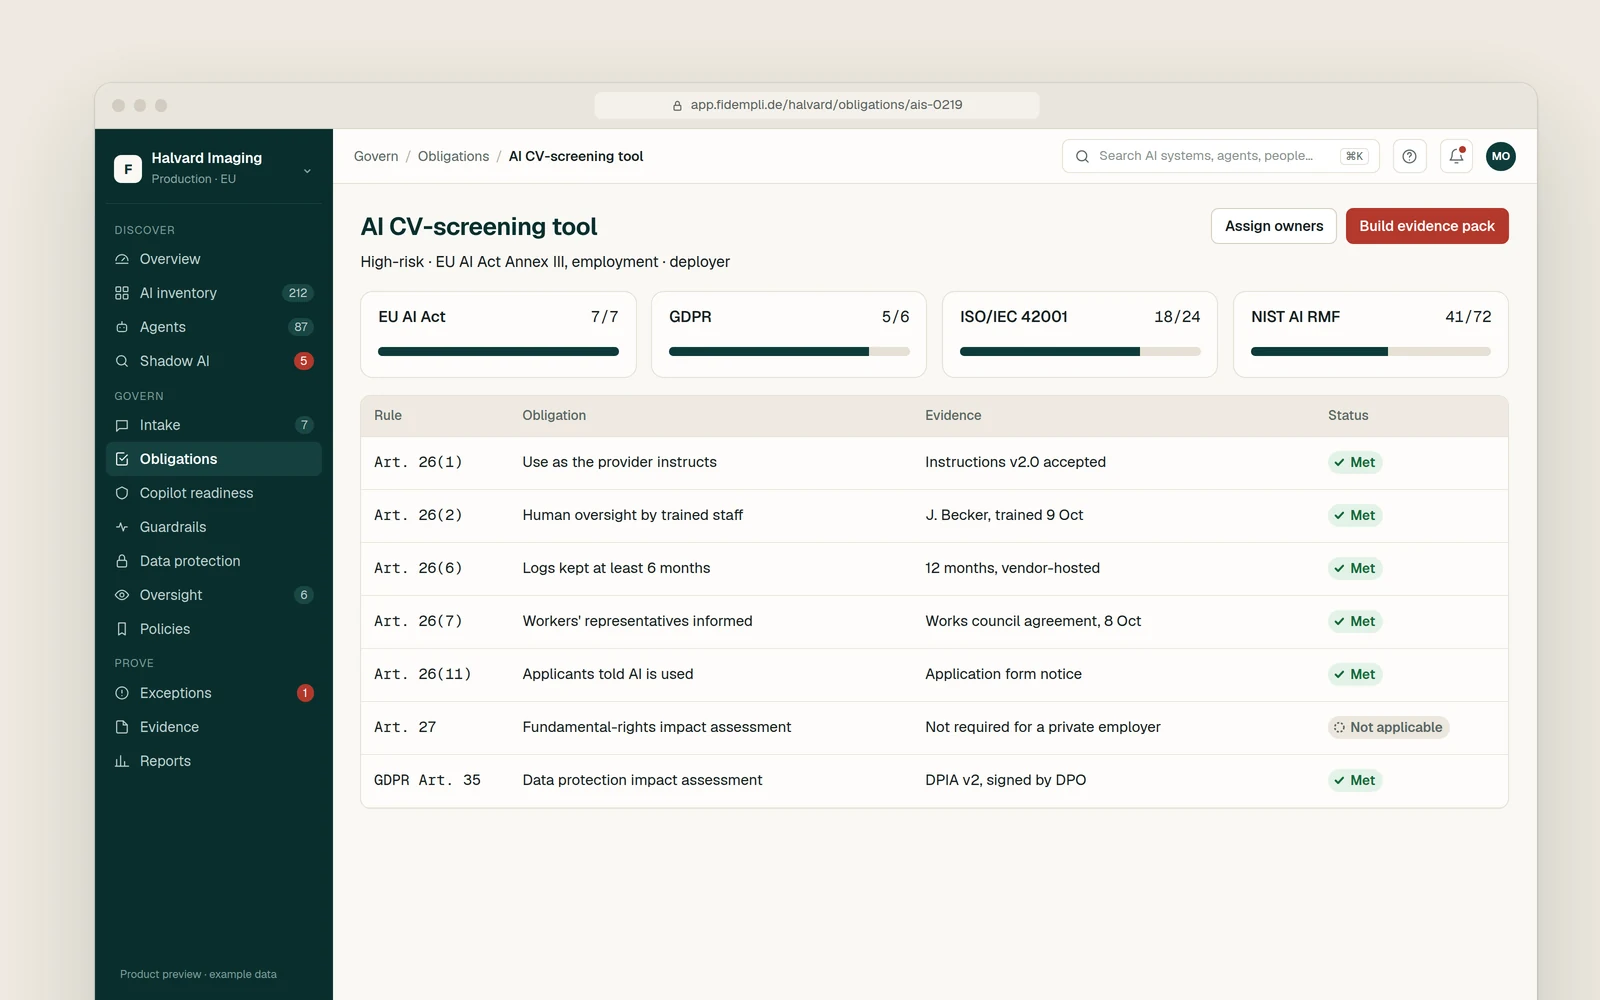
From December 2026 the Fidempli platform keeps your AI management system current: inventory, risk assessments, controls and evidence are maintained from live data, so the next audit starts from records, not a document hunt.
No. Certification is done by an accredited certification body. We prepare you for the audit and support you through it, so the two roles stay independent.
We already have ISO/IEC 27001. Does that help?
Yes. ISO/IEC 42001 uses the same management system structure, so your existing processes for documents, internal audit and management review can be extended rather than rebuilt.
How does the NIST AI RMF fit in?
The NIST AI RMF is a voluntary framework with four functions: Govern, Map, Measure and Manage. We use it to structure your risk method and map it to ISO/IEC 42001, so one set of work serves both.
Does ISO/IEC 42001 make us compliant with the EU AI Act?
Not on its own. The standard gives you a management system that supports many AI Act duties, such as risk management, documentation and oversight. We map your AI systems to their specific AI Act obligations separately.
Do we need the platform to build an AIMS?
No. We can build it with your existing tools. The platform helps keep inventory, risk assessments and evidence current once the system is running.