
Solutions
Built for the rules you answer to.
Each solution maps the requirements of a framework, product or industry to the platform capabilities and services that meet them.
By framework
EU AI Act
The bans on prohibited practices and the AI literacy duty apply since February 2025. Fidempli shows which of your AI systems the Act covers, what each one owes, and the proof that you delivered it.
Learn more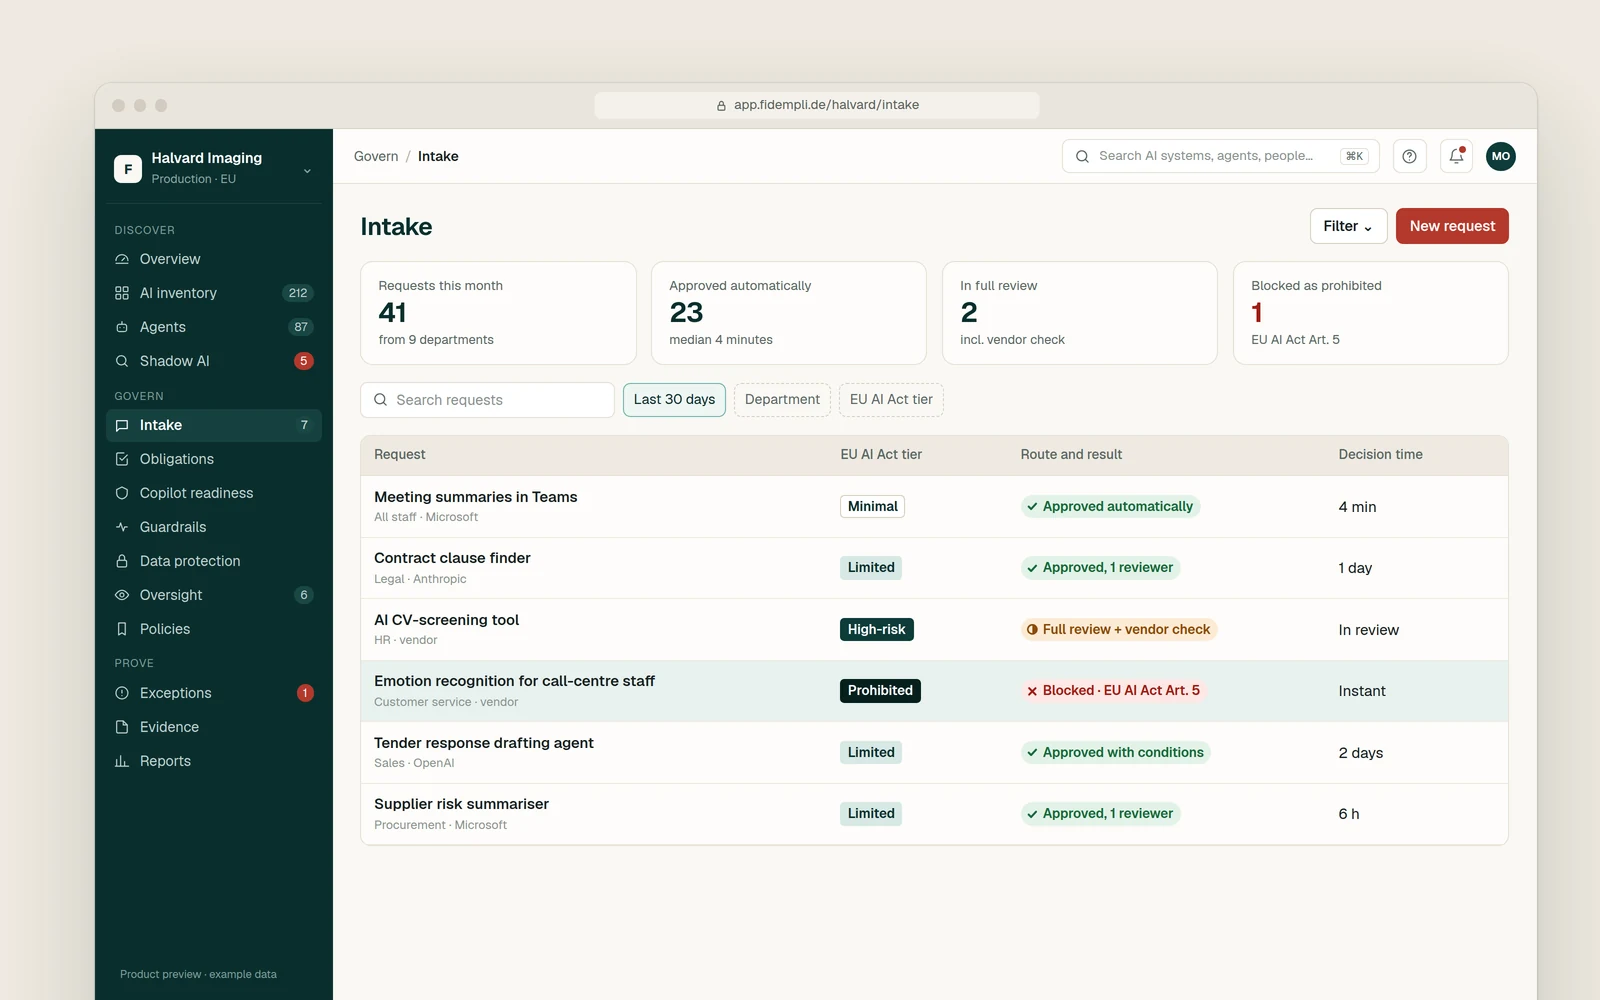
GDPR and data protection
Personal data in prompts, uploads and agent actions is still personal data. Fidempli finds where it goes, removes or pseudonymises it before it reaches a model, and records why.
Learn more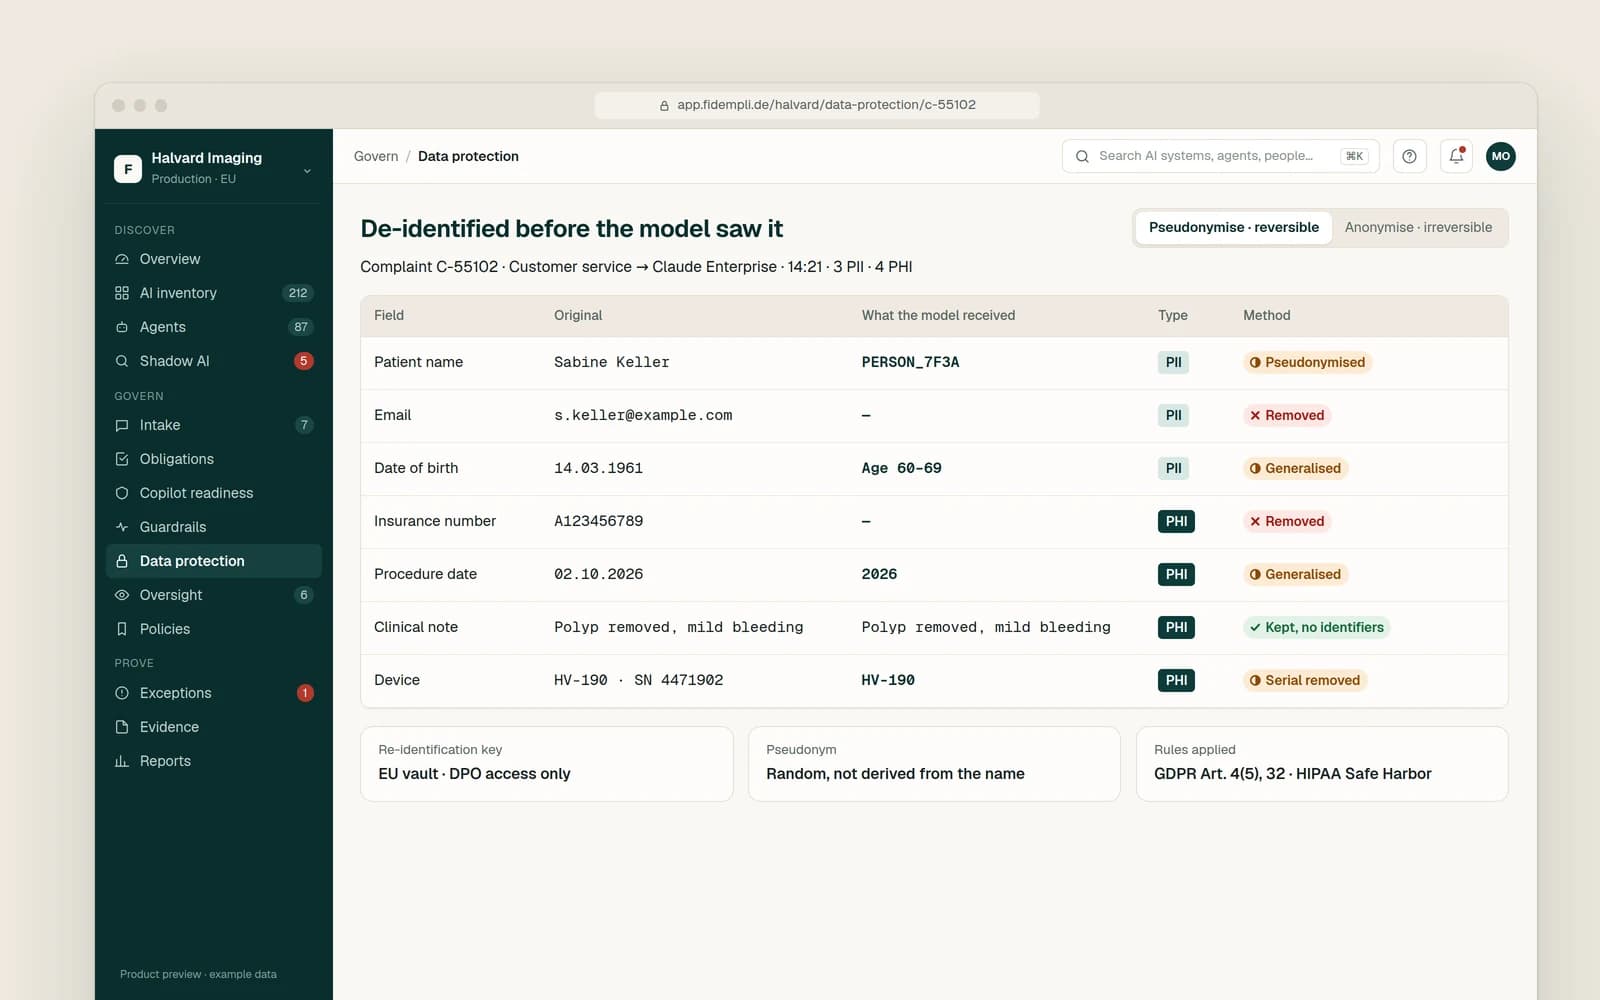
ISO/IEC 42001
ISO/IEC 42001 asks for an AI management system: an inventory, risk assessment, controls, roles and records. Fidempli gives you the records an auditor asks for, kept current by live data.
Learn more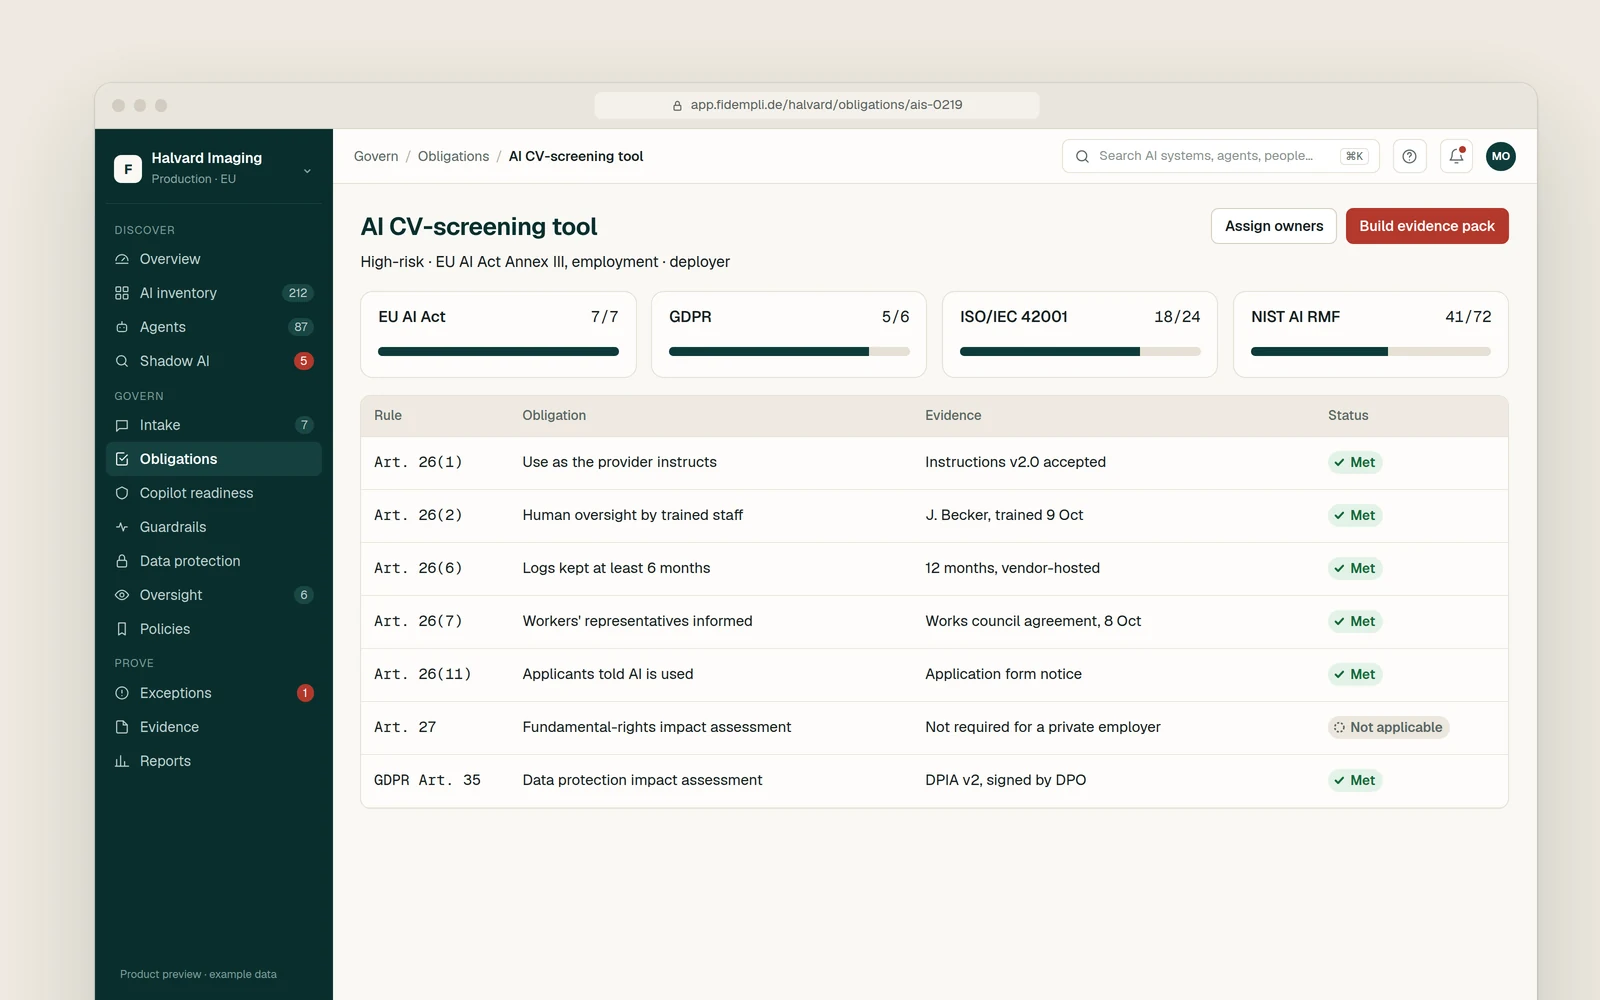
NIST AI RMF
The NIST AI Risk Management Framework organises AI risk work into four functions. Fidempli covers each one with live data, so you can show progress, not just intent.
Learn more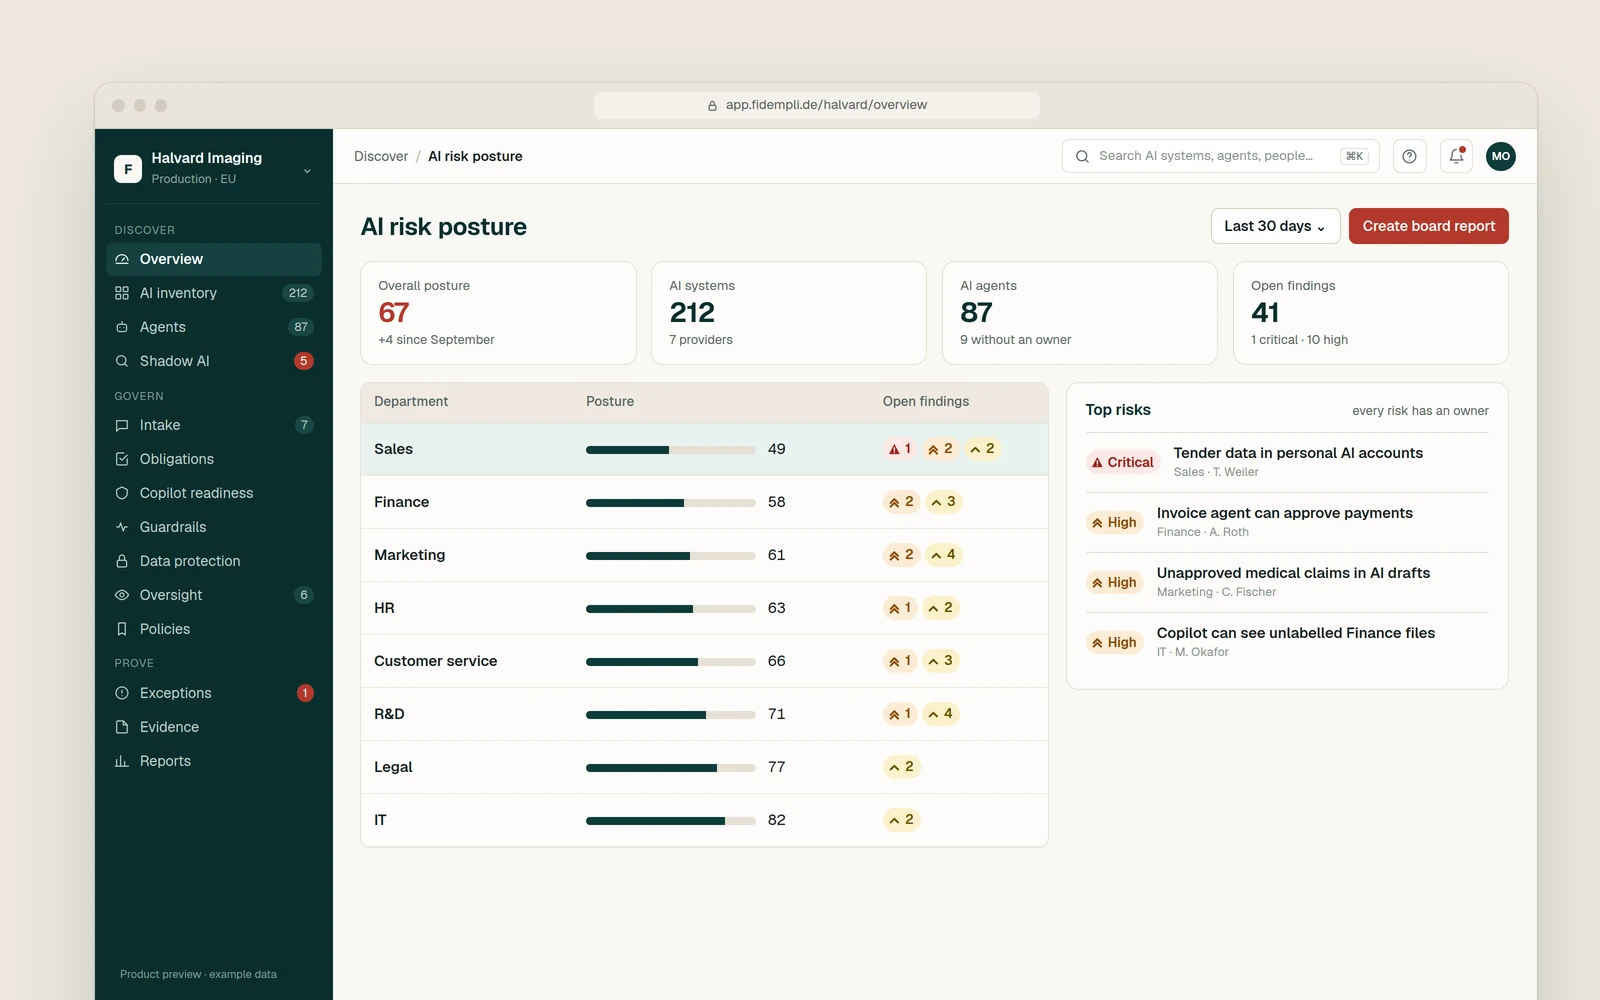
NIS2 and DORA
NIS2 and DORA require you to manage ICT and supplier risk, control access and report incidents. AI tools, agents and providers are now part of that estate.
Learn more
By industry
Healthcare and MedTech
Patient data, regulated documents and medical device rules leave little room for error. Fidempli keeps health data out of AI models and gives you evidence that fits regulated quality systems.
Learn moreIndustries
We work with regulated, data-heavy European organisations. These are the regulations we work with in each industry.
Learn moreFidempli provides governance, risk and compliance advisory and works alongside your legal counsel. We do not provide legal advice.
Start with the framework that matters most to you.
Our consultants assess where you stand; the platform keeps it current.