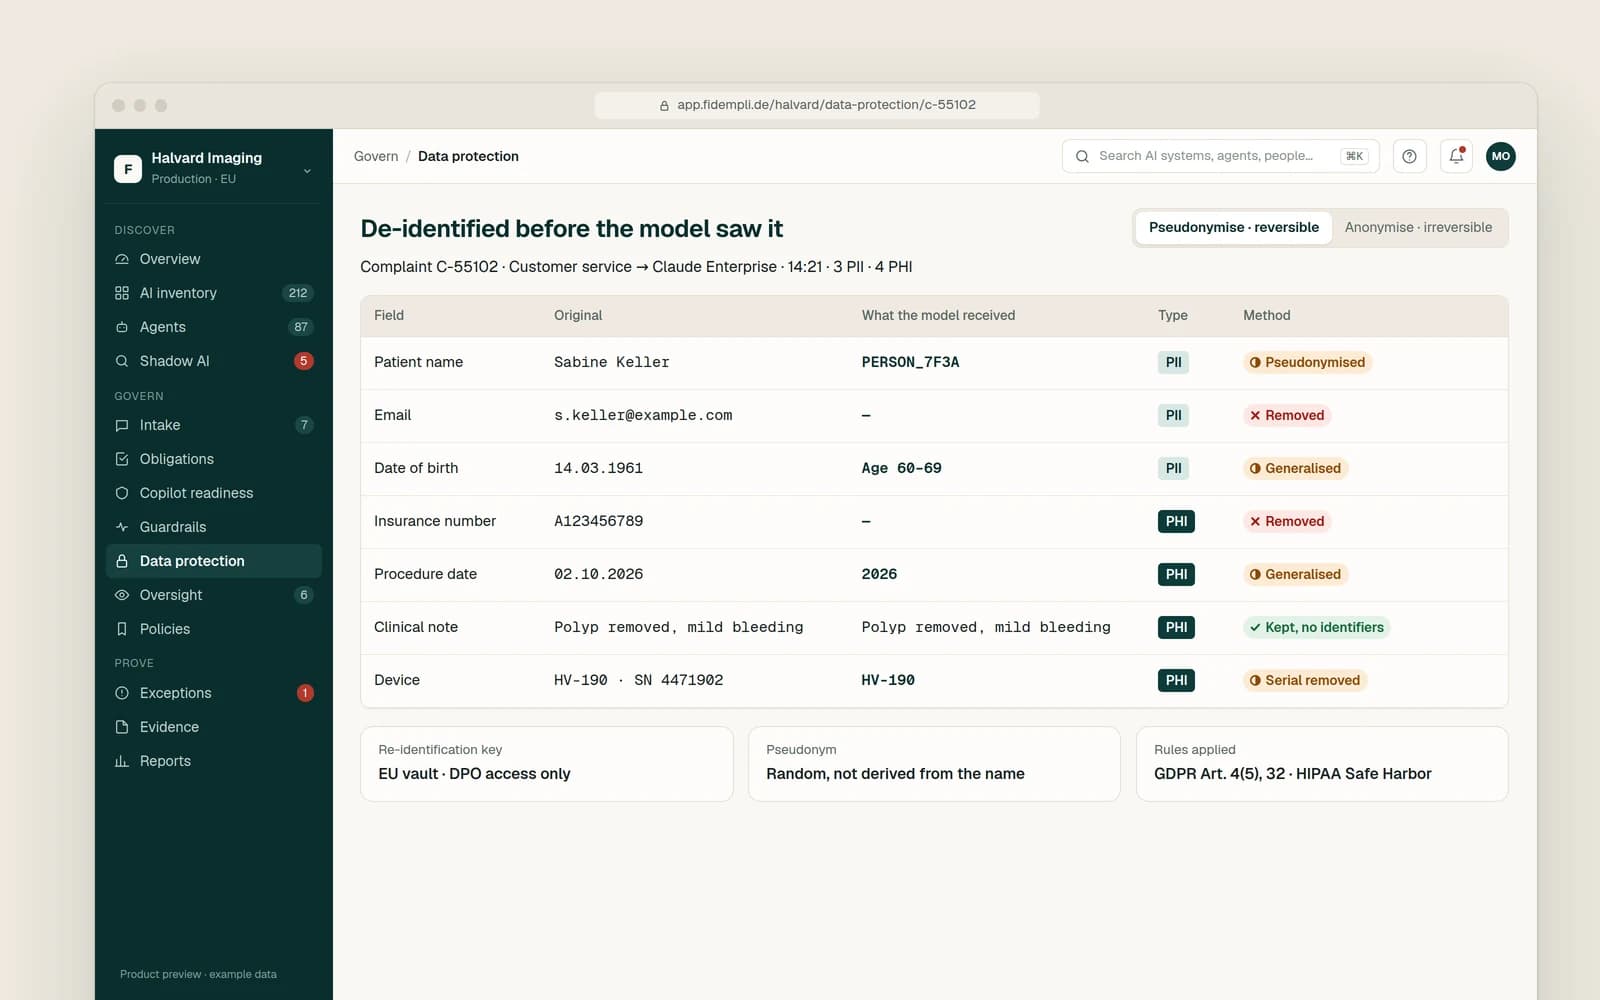
Personal data reaches AI through many routes: prompts and uploads, documents indexed for retrieval (RAG), training and fine-tuning data, logs kept by the provider. Each route is processing under GDPR, and many are not in any record.
Data protection officers are asked to approve AI tools without knowing where the data goes, who the processor is or whether it leaves the EU. Without that picture, every new AI use becomes a delay or a gamble.
What we do
AI Privacy & Data Protection
Map the data flows
For each AI use we trace which personal data goes into prompts, uploads, retrieval indexes, training data and logs, and where it is stored and processed.
Establish purpose and legal basis
We set the purpose and legal basis under Articles 5 and 6, identify special categories of data under Article 9, and check where automated decisions under Article 22 may arise.
Carry out the DPIA
We screen each AI use for the need for a data protection impact assessment under Article 35 and carry it out where required, with risks and measures documented.
Review processors and transfers
We review the AI providers' data processing agreements under Article 28, their use of your data, retention and transfers outside the EU under Chapter V.
Update the records of processing
We add each AI use to your records of processing activities under Article 30, so the record reflects how AI is actually used.
Build in technical safeguards
We design data protection by design under Article 25 and security of processing under Article 32: minimisation, pseudonymisation, access control on retrieval and retention limits.
How we deliver
Consulting · Professional services · Managed services
Consulting
Our privacy consultants assess your AI uses, carry out DPIAs and advise your data protection officer and business owners on each decision.
Professional services
Our engineers implement the safeguards in your environment, such as sensitivity labels, data loss prevention, access control on RAG sources and pseudonymisation.
Managed services
We review new AI uses, keep DPIAs and the records of processing current, and monitor how personal data flows into AI tools as a managed service.
AI automation in this service
Automated pre-fill of DPIA drafts from inventory and intake data, for the privacy team to complete and approve
Automated detection of personal and health data in sample prompts, uploads and RAG sources
Automated generation of records of processing entries for each AI use
What you get
Data flow map per AI use, incl. prompts, RAG, training data and logs
Legal basis and purpose per AI use
DPIAs for the AI uses that need one
Processor and transfer review of AI providers
Updated records of processing activities
Technical and organisational measures, prioritised
Frameworks
GDPR
EU AI Act
ISO/IEC 27001
In detail
Topics covered
Principles, purpose and legal basis (Art. 5, 6)
Special categories of data (Art. 9)
Automated individual decisions (Art. 22)
Data protection by design (Art. 25)
Processors and AI providers (Art. 28)
Records of processing activities (Art. 30)
Security of processing (Art. 32)
Data protection impact assessment (Art. 35)
Transfers outside the EU (Chapter V)
Privacy by design for AI in your software
SaaS products
Enterprise platforms
CRM
ERP
HRMS
Custom applications
Platform
After the project, the Fidempli platform keeps it running
When the Fidempli platform launches in December 2026, it applies the result in daily use: personal and health data is pseudonymised or removed before any AI model sees it, and each DPIA stays linked to the AI system it covers.
Only where there is a purpose, a legal basis and a provider contract that fits. We help you set clear rules per tool and add technical controls, so the rule does not depend on memory alone.
Does every AI use need a DPIA?
No. Article 35 requires one where processing is likely to result in a high risk to people. Many AI uses, such as profiling, HR decisions or large-scale processing of health data, typically meet that bar. We screen each use and document the outcome either way.
Does our AI provider use our data for training?
That depends on the product, the contract and the settings. We review the terms and configuration of each provider and record what applies.
What about personal data in RAG and training data?
Documents indexed for retrieval and data used for training or fine-tuning are processing too. We check purpose, minimisation and access control, so the AI only returns what the user is allowed to see.
We already have a data protection team. What do you add?
AI-specific knowledge of how copilots, agents and RAG systems handle data, plus engineers who implement the controls. Your data protection officer stays in charge of the decisions.