The Fidempli AI governance platform launches in December 2026. Design-partner places are open.Apply now →
Fidempli

Govern

Decide on each AI use in proportion to its risk.

One intake for every new AI use. Each request is classified, routed to the right reviewers and mapped to the obligations that apply, with the evidence attached.

Capabilities

Govern

Intake and approval

Approve low-risk AI in minutes, review high-risk AI properly, and block prohibited uses outright.

  • One intake form for new AI use cases, tools and agents
  • Automatic classification by EU AI Act tier, with the reasoning recorded
  • Vendor review and approvals routed by risk; prohibited practices cannot be approved
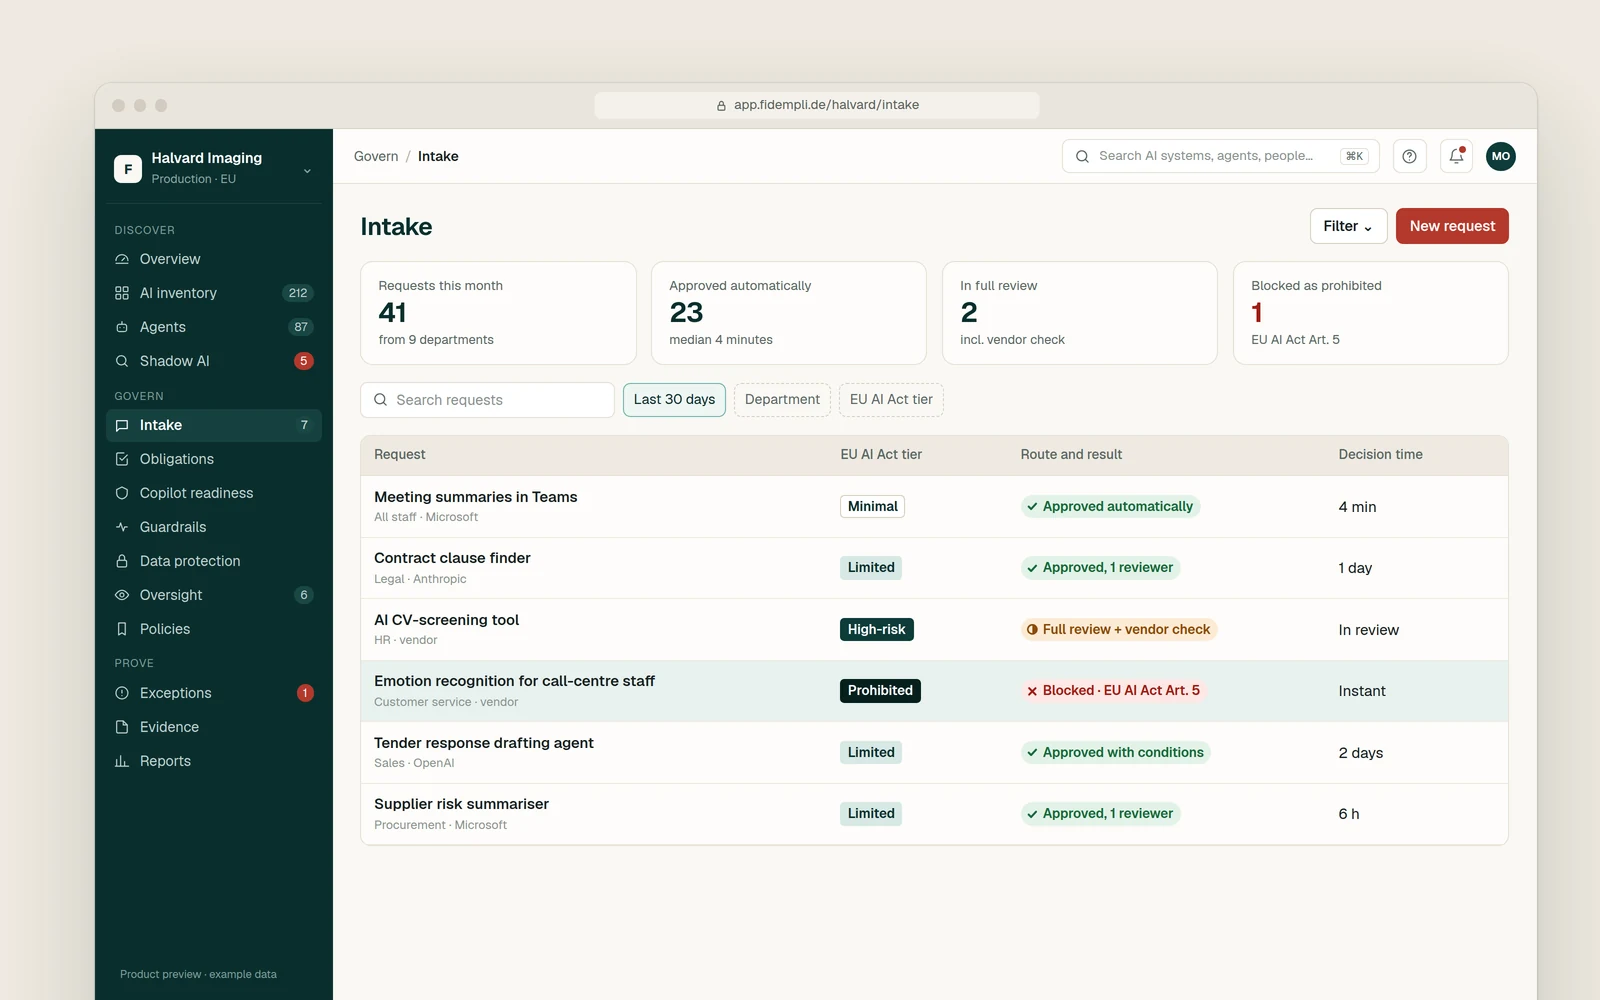
Intake queue with requests routed by EU AI Act tier, from automatic approval to a blocked prohibited use
Product preview with example data
Govern

Compliance mapping

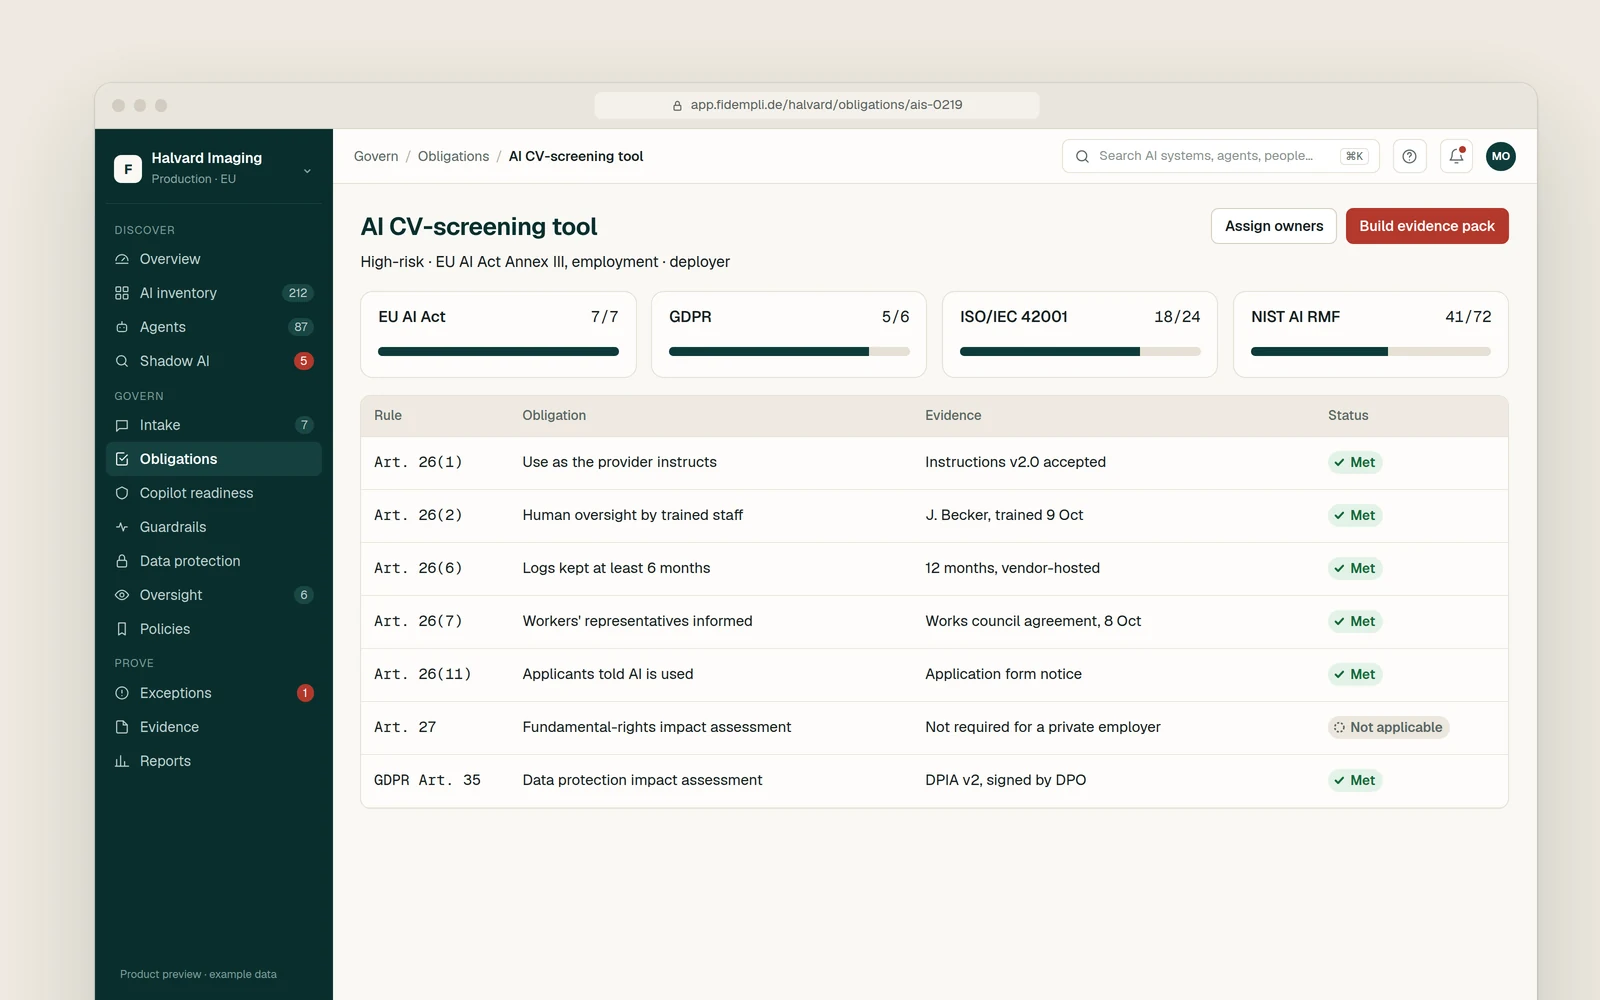
Map each AI use to its EU AI Act duties, plus GDPR, ISO/IEC 42001 and NIST AI RMF, with evidence.

  • Obligations per AI system, with owner, status and evidence
  • Coverage per framework and per AI system
  • "Not applicable" recorded with the reason
Obligations for a high-risk HR tool with coverage per framework and evidence per obligation
Product preview with example data
Govern

Copilot readiness

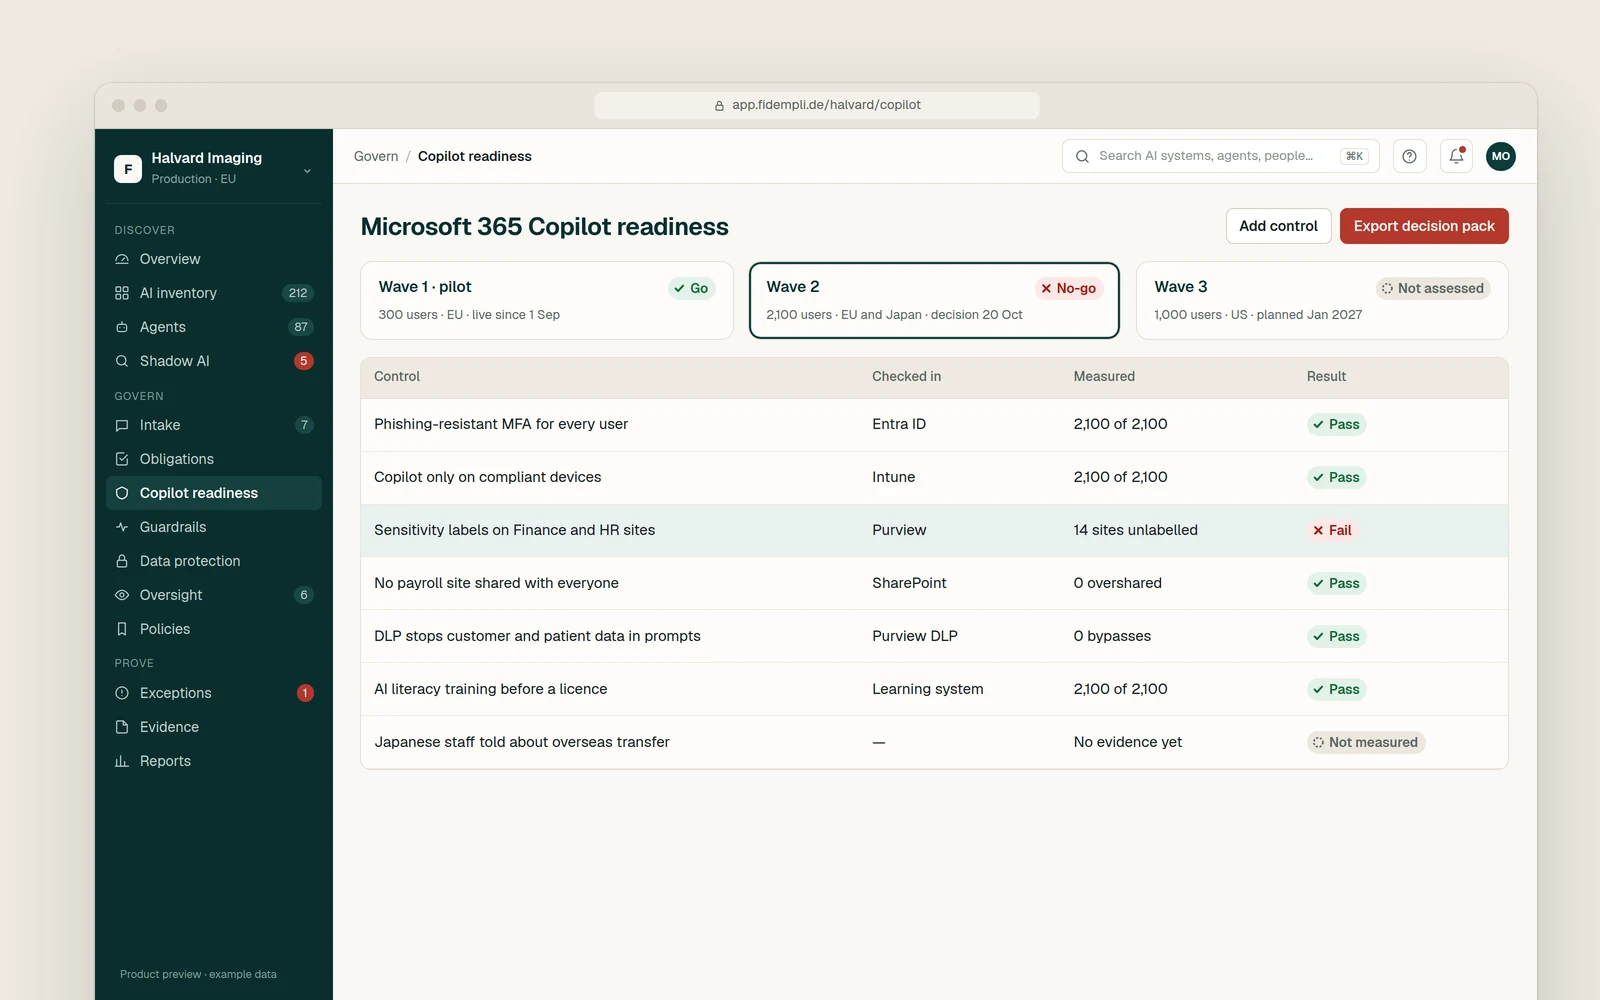
Know from live tenant data whether Microsoft 365 Copilot is safe to switch on.

  • Controls checked against Entra ID, Intune, Purview and SharePoint
  • Go or no-go per rollout wave
  • "Not measured" never counts as a pass
Microsoft 365 Copilot rollout gate with controls checked in Entra ID, Intune, Purview and SharePoint
Product preview with example data

See it on your own AI estate.

The platform launches in December 2026. Design partners start earlier.