Security rules now come from several directions. NIS2, implemented in Germany by the NIS2UmsuCG, makes management bodies responsible for cybersecurity risk management. DORA has applied to financial entities since 17 January 2025. Customers ask for ISO/IEC 27001.
Many organisations answer each request separately, with spreadsheets, scattered policies and controls nobody checks. That costs time at every audit and leaves gaps between what is written and what actually runs.
What we do
GRC, ISO 27001, NIS2 & DORA
Scope and gap analysis
We define the scope and compare your current controls with ISO/IEC 27001:2022, NIS2 and, for financial entities, DORA.
Risk assessment
We identify, assess and communicate information security risks and agree a treatment plan with the risk owners.
Build the ISMS
We write the policies, define roles and processes and select the applicable controls from the 93 in Annex A, documented in a Statement of Applicability.
Implement controls
We help your teams put the controls in place, including incident handling, supplier management and ICT third-party risk.
Audit and certification readiness
We run internal audits and a management review, close findings and prepare you for the certification audit.
Monitor and improve
We monitor compliance and risks over time and keep the ISMS current as your organisation and the rules change.
How we deliver
Consulting · Professional services · Managed services
Consulting
We assess your security governance against ISO/IEC 27001, NIS2 and DORA and give you a prioritised roadmap.
Professional services
We build the ISMS with you: policies, risk register, Statement of Applicability, processes and audit preparation.
Managed services
We run ongoing GRC activities for you: risk reviews, internal audits, control monitoring and regulatory change tracking.
AI automation in this service
Automated mapping of your existing controls to ISO/IEC 27001 Annex A, NIS2 and DORA, so one control serves several frameworks.
Automated evidence collection from Microsoft 365, Entra ID and cloud platforms for access, logging and configuration controls.
Automated reminders for risk reviews, policy reviews and expiring exceptions.
What you get
Gap analysis against ISO/IEC 27001, NIS2 and DORA
Risk register and risk treatment plan
ISMS policies and Statement of Applicability
Internal audit report and management review
Certification readiness assessment
Compliance roadmap
Frameworks
ISO/IEC 27001
NIS2
DORA
GDPR
In detail
Advisory and consulting
Strategic roadmapping
Tailored solutions
Proactive risk management
Continuous support and optimisation
Continuous improvement
Audit and assurance
Security assessments
Regulatory compliance monitoring
Actionable recommendations
Continuous improvement
Compliance services: ISO 27001
Strategic planning
Comprehensive assessment
Risk management
Implementation
Continuous improvement
Risk management
Risk identification
Risk assessment
Risk communication
Risk treatment and recommendations
Continuous monitoring
Technology solutions
Threat intelligence: malware, ransomware and insider risk
Integration and configuration
Scalable security infrastructure
Compliance monitoring
Platform
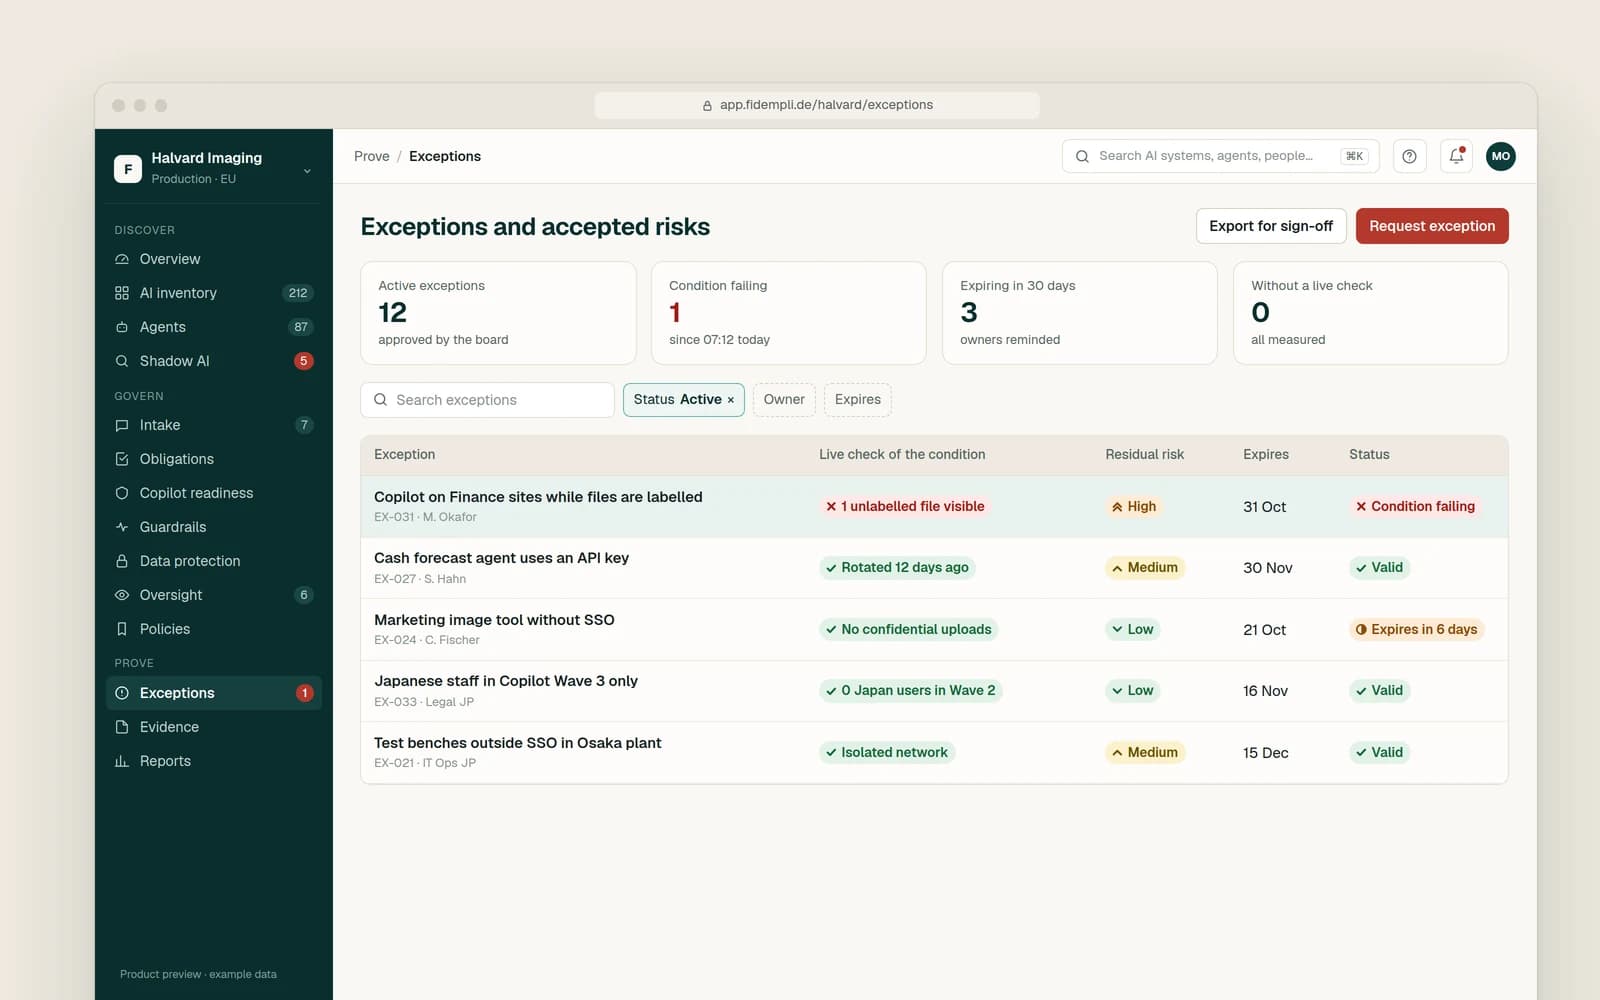
After the project, the Fidempli platform keeps it running
From December 2026, the Fidempli platform tracks every accepted risk with an owner, an expiry date and a live check, and keeps evidence ready for auditors. AI-related controls sit next to your ISMS, not in a separate spreadsheet.
No. Certification is done by an accredited certification body. We build the ISMS with you and prepare you for the certification audit.
How many controls does ISO/IEC 27001:2022 have?
Annex A lists 93 controls in four themes: organisational, people, physical and technological. You decide which apply and justify it in the Statement of Applicability.
Does NIS2 apply to us?
It depends on your sector and size. We check whether you fall under NIS2 and, in Germany, the NIS2UmsuCG, and which obligations follow.
We are a financial entity. Do we need DORA and NIS2?
For financial entities in scope, DORA sets the rules for ICT risk management, incident reporting, resilience testing and ICT third-party risk. We help you work out which rules apply to you and build one set of controls for both.
Does an existing ISO/IEC 27001 certificate help with NIS2 and DORA?
Yes, it is a good basis. Both still have specific requirements, such as incident reporting, that we map and close as gaps.