Home Solutions GDPR and data protection GDPR and data protection
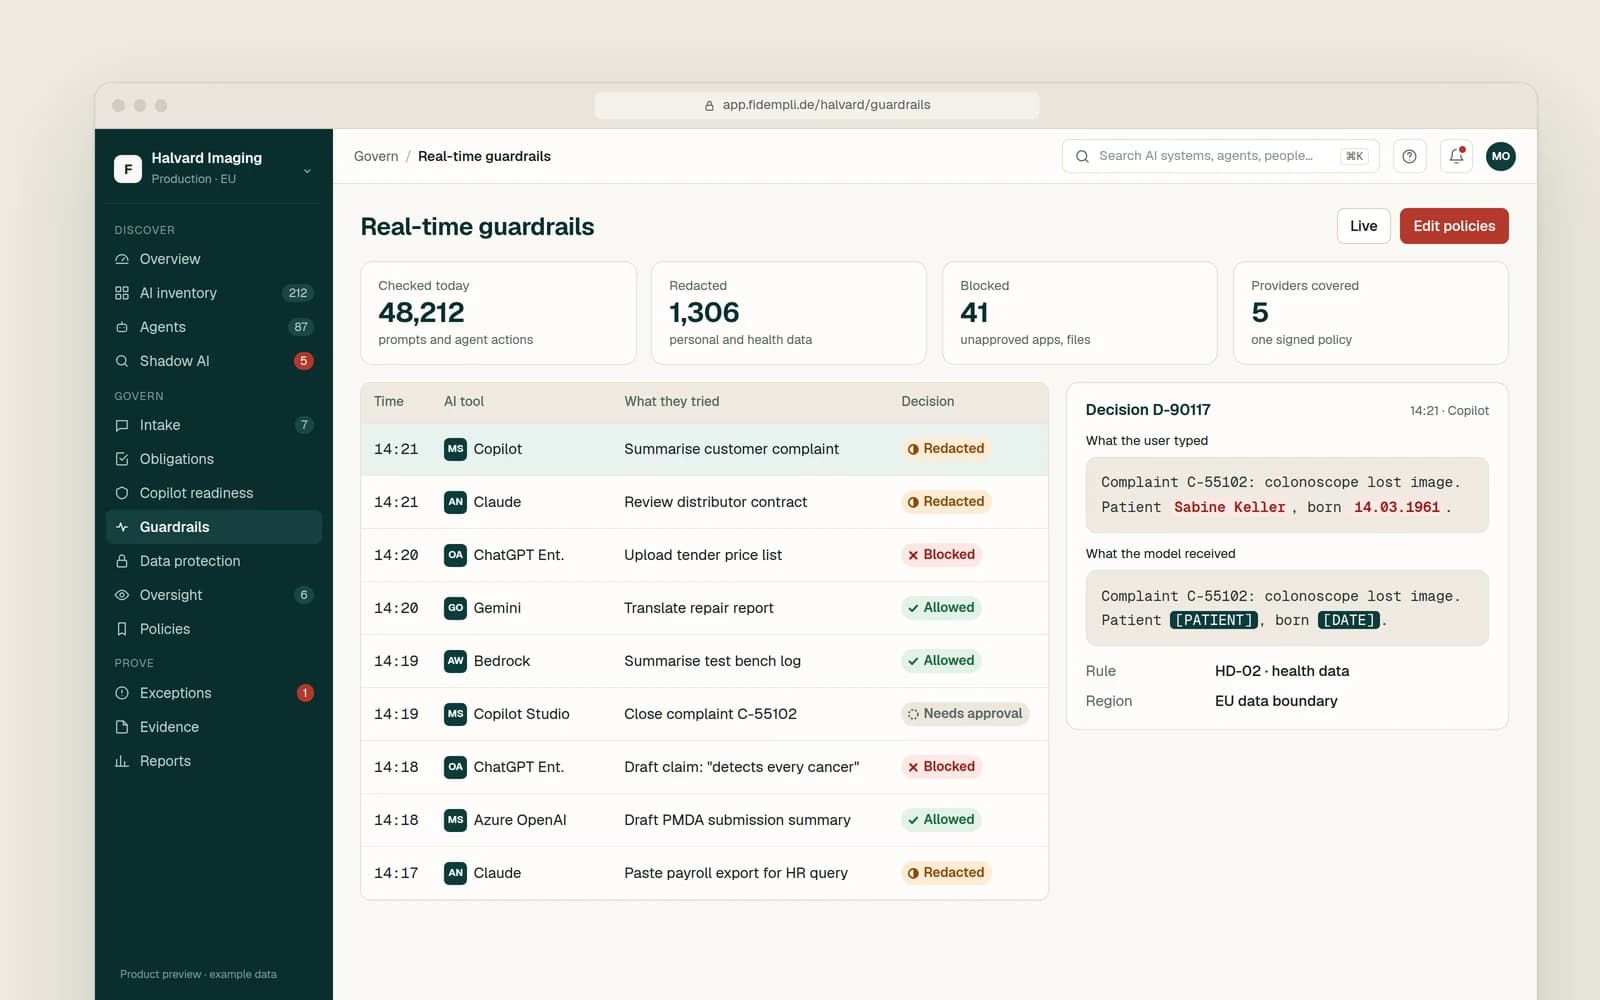
Use AI without losing control of personal data. Personal data in prompts, uploads and agent actions is still personal data. Fidempli finds where it goes, removes or pseudonymises it before it reaches a model, and records why.
Product preview with example data How Fidempli handles it
GDPR requirements, mapped to the platform. Requirement How Fidempli handles it Capability Lawfulness and purpose limitation (Art. 5, 6) Each AI use is registered with its purpose and owner before it goes live Intake and approval AI inventory Special categories, such as health data (Art. 9) Health data is detected and removed or pseudonymised before any model sees it PII and PHI protection Data protection by design (Art. 25) Guardrails apply one policy to every AI provider Real-time guardrails Security of processing and pseudonymisation (Art. 32, 4(5)) Re-identification keys kept in an EU vault with access for the DPO only PII and PHI protection International transfers (Art. 44) Unapproved AI apps that store data outside the EU are found and can be blocked Shadow AI Impact assessment (Art. 35) DPIA tracked as an obligation for each AI system that needs one Compliance mapping
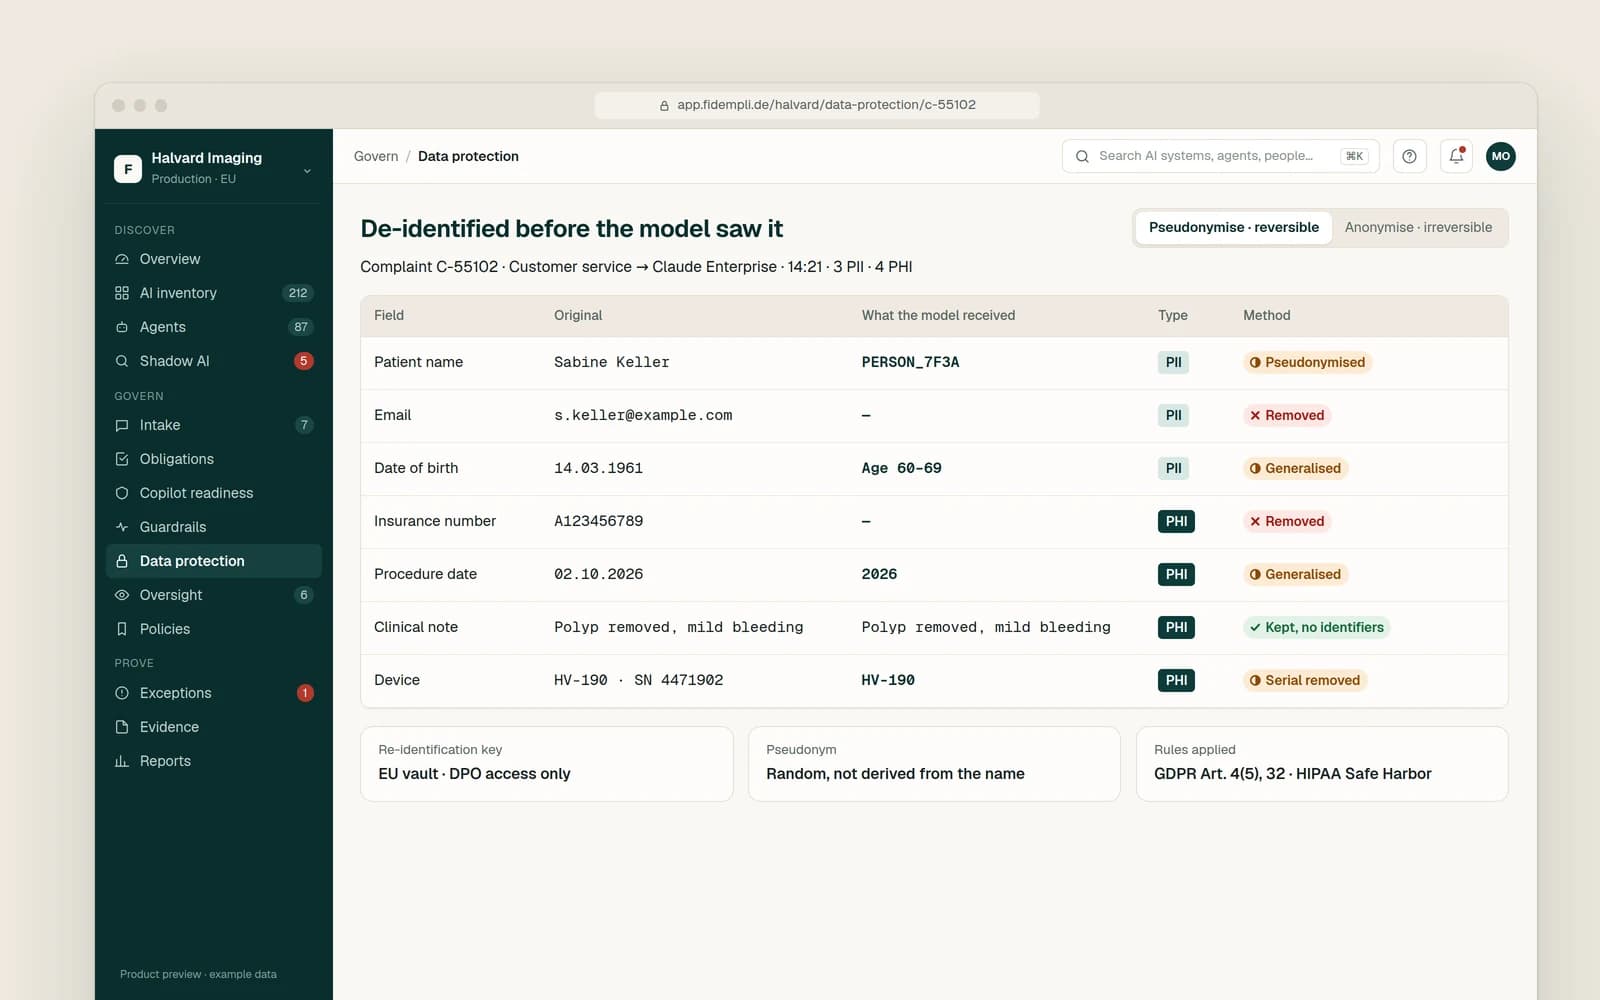
De-identified, field by field. Choose per field whether data is pseudonymised, generalised or removed, and see exactly what the model received.
Names, contact details, insurance numbers, dates and serial numbers Reversible pseudonymisation or irreversible anonymisation Every decision recorded with the rule that applied Product preview with example data Related services
Consulting · Professional services · Managed services Other solutions Fidempli provides governance, risk and compliance advisory and works alongside your legal counsel. We do not provide legal advice.
Start with the framework that matters most to you. Our consultants assess where you stand; the platform keeps it current.