The Fidempli AI governance platform launches in December 2026. Design-partner places are open.Apply now →
Fidempli

Cybersecurity & Privacy

Security strategy and architecture.

A security programme and target architecture your teams can build to, including for AI.

The problem

Security often grows tool by tool and project by project. The result is overlapping products, gaps between them and no shared picture of where the organisation is heading.

NIS2, DORA and the GDPR expect security to be planned and built in, not added after go-live. AI adds new data flows, identities and suppliers that most architectures were not designed for.

What we do

Security Strategy & Architecture

  1. Assess

    We review your current security organisation, controls, architecture and cloud estate and assess their maturity.

  2. Set the strategy

    We define your security programme with priorities, roles, budget lines and a roadmap tied to your business and regulatory requirements.

  3. Design the target architecture

    We design the target security architecture for identity, data, network, cloud and AI, with clear principles and building blocks.

  4. Build in security and privacy by design

    We embed privacy by design and security by design across your software lifecycle, from requirements to release.

  5. Plan the cloud

    We shape your cloud strategy and architecture, assess migrations and prepare the business case.

  6. Guide delivery

    We support your teams during implementation with architecture reviews and decisions.

How we deliver

Consulting · Professional services · Managed services

Consulting

We assess your security posture and define the strategy, target architecture and roadmap.

Professional services

We work with your engineering and cloud teams to put the architecture and secure-by-design practices into place.

Managed services

We act as your ongoing security architecture function, reviewing designs and keeping the roadmap current.

AI automation in this service

  • Automated identity and cloud configuration checks against your target architecture and baseline.
  • Automated mapping of your existing controls to ISO/IEC 27001 Annex A, NIS2 and DORA requirements.
  • Automated threat modelling drafts from architecture diagrams and data flows, reviewed by our architects.

What you get

  • Security maturity assessment and gap analysis
  • Security strategy and multi-year roadmap
  • Target security architecture with principles and building blocks
  • Secure-by-design and privacy-by-design requirements for your software lifecycle
  • Cloud strategy, target operating model and business case
  • Architecture decision records

Frameworks

  • ISO/IEC 27001
  • NIS2
  • DORA
  • GDPR
  • EU CRA

In detail

Secure by design for software

  • SaaS products
  • Enterprise platforms
  • CRM
  • ERP
  • HRMS
  • Custom applications

Cloud strategy and architecture

  • Cloud strategy and architecture
  • Cloud migration assessment and proofs of concept
  • Maturity assessment and gap analysis
  • Multi-cloud vendor analysis
  • Target operating model: on-premises versus cloud
  • Capacity planning and cost analysis
  • Business case preparation

Platform

After the project, the Fidempli platform keeps it running

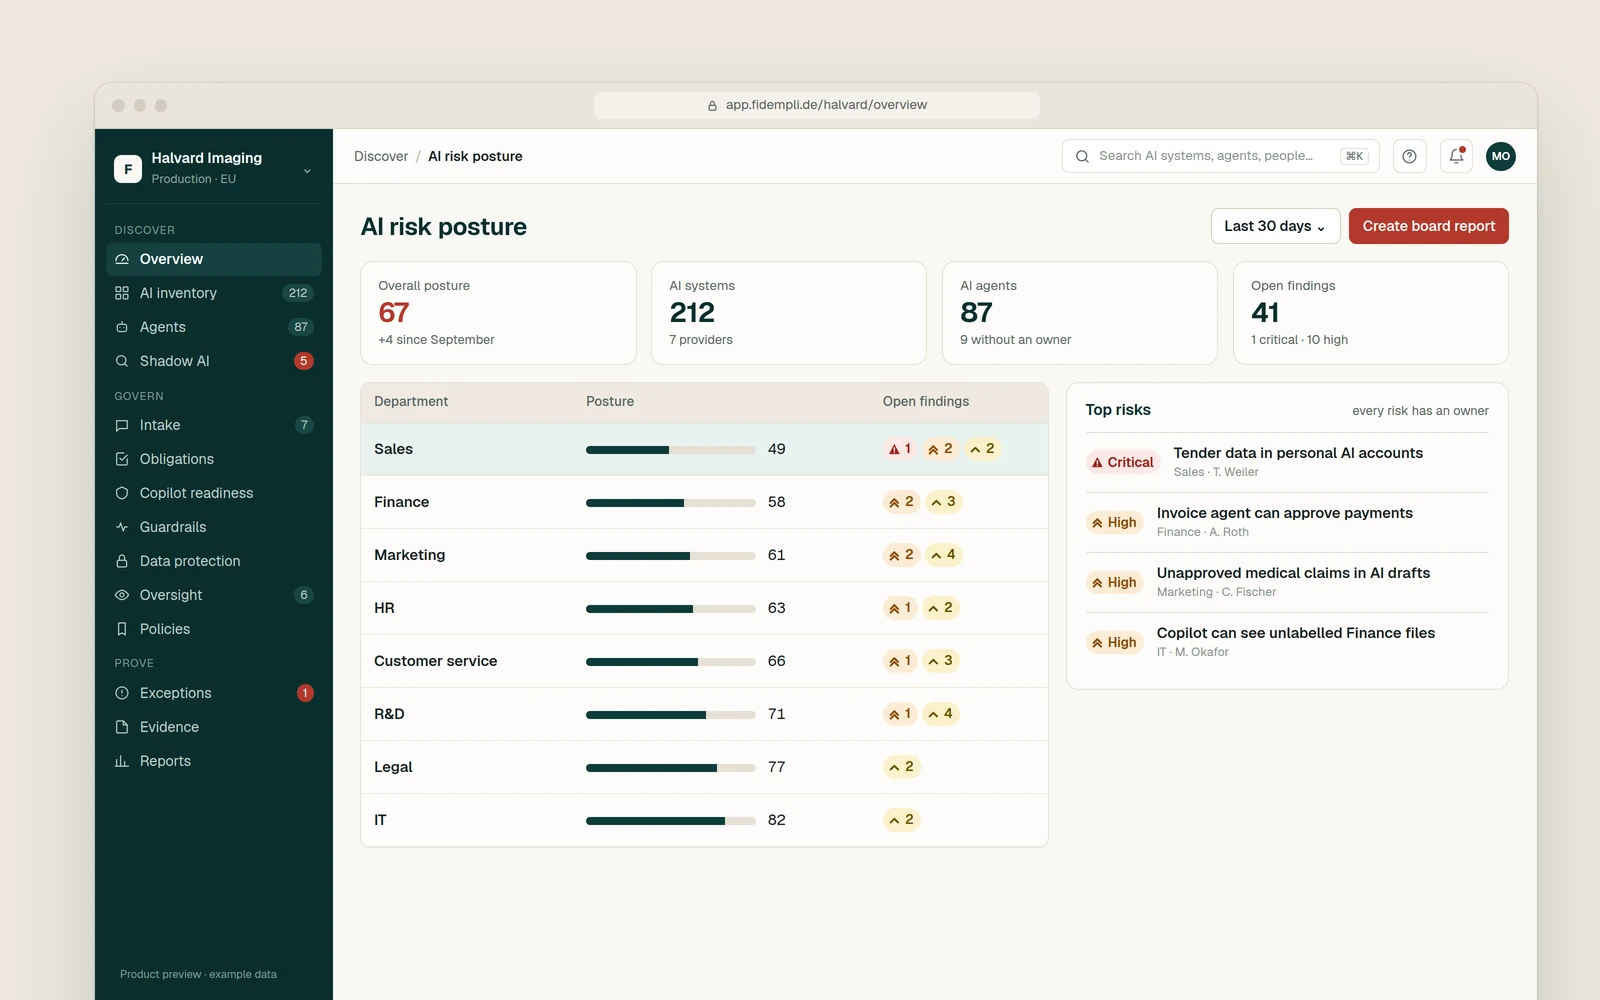
From December 2026 the Fidempli platform brings the AI part of your architecture under control: AI tools, agents and providers in one inventory, with guardrails and evidence that match your target design.

Explore the platform
Fidempli AI risk posture dashboard with posture by department and the top risks
Product preview with example data

Frequently asked questions

Do you recommend specific products?

We design to your requirements first and only then assess products. Products are chosen to fit the architecture, not the other way round.

Can you work with our existing architecture team?

Yes. We often add capacity or a second view to an existing team, and agree who owns which decisions at the start.

How does secure by design work in practice?

We add security and privacy requirements, threat modelling, reviews and testing to each stage of your software lifecycle, for SaaS, enterprise platforms, CRM, ERP, HRMS and custom applications.

Does the strategy cover NIS2 and DORA?

Yes, where they apply to you. We map the strategy and architecture to their risk management, supplier and incident requirements, alongside ISO/IEC 27001.

Where does AI fit in?

AI tools, agents and providers are part of the target architecture, with identity, data protection and oversight designed in from the start.

More services in this pillar

Start with a 30-minute AI risk conversation.

A senior consultant replies within one business day. Or join the 3–5 design partners shaping the platform before launch.