Home Solutions EU AI Act EU AI Act
EU AI Act compliance, from inventory to evidence. The bans on prohibited practices and the AI literacy duty apply since February 2025. Fidempli shows which of your AI systems the Act covers, what each one owes, and the proof that you delivered it.
Product preview with example data How Fidempli handles it
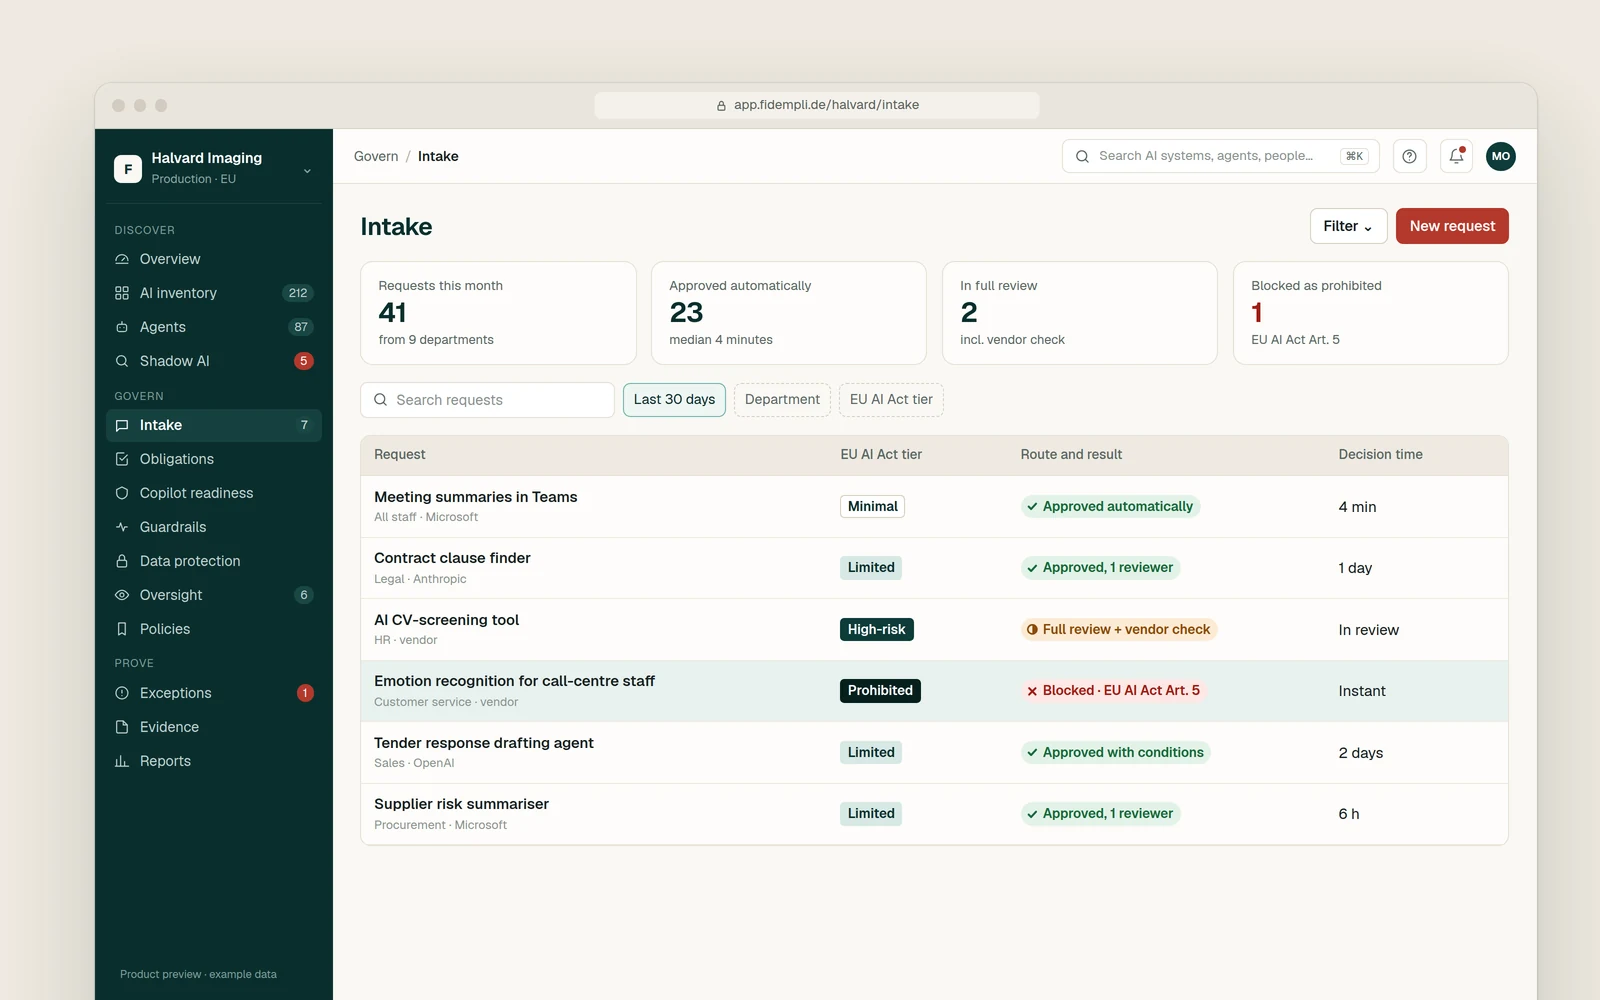
Every obligation, mapped to a capability. Requirement How Fidempli handles it Capability Know which AI you run AI inventory across every provider, with owners and departments AI inventory Shadow AI Prohibited practices (Art. 5) Prohibited uses are blocked at intake; no one in your organisation can approve them Intake and approval Classify high-risk AI (Art. 6, Annex III) Automatic classification with the reasoning recorded, reviewed by a person Intake and approval Deployer duties (Art. 26) Human oversight, logs, informing workers and affected people, each with evidence Compliance mapping Human oversight AI literacy (Art. 4) Training completion checked before access to AI tools Copilot readiness Technical documentation (Art. 11, Annex IV) Built from platform records for the AI you develop yourself Evidence and reporting Answer an authority An evidence pack with policy versions, decisions and approvals in minutes Evidence and reporting
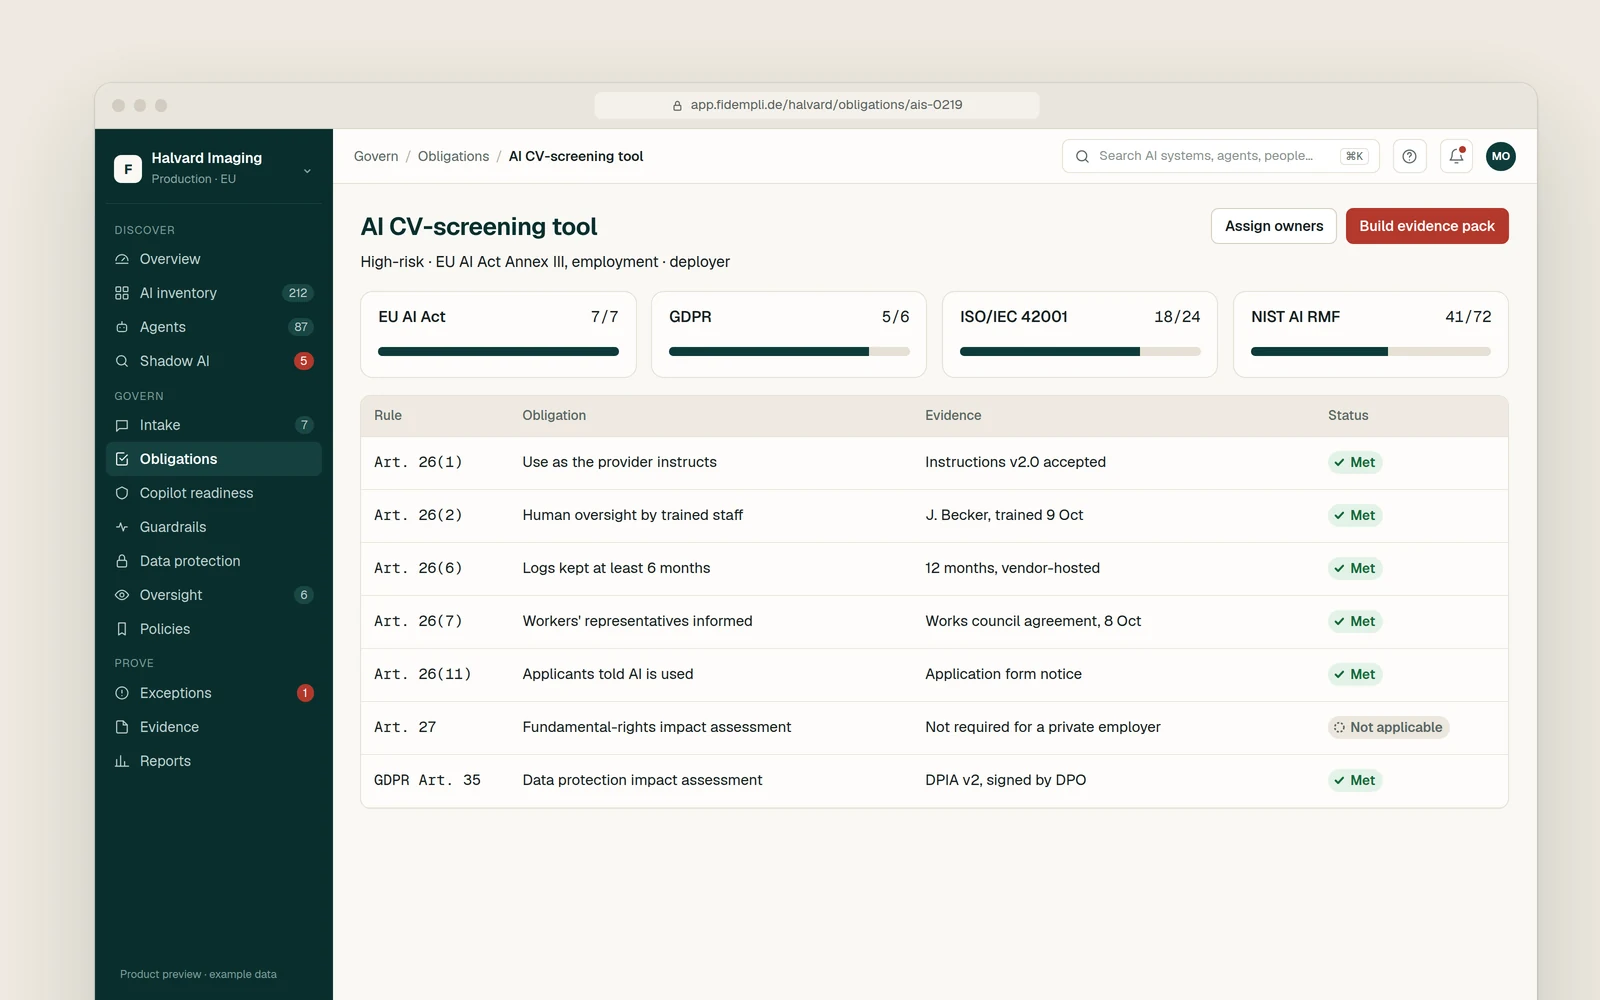
One set of evidence, several frameworks. The same records count towards GDPR, ISO/IEC 42001 and NIST AI RMF, so your teams document once.
Coverage per framework and per AI system Evidence attached to each obligation, with owner and date "Not applicable" recorded with the reason, for example Art. 27 for private employers Product preview with example data Related services
Consulting · Professional services · Managed services Other solutions Fidempli provides governance, risk and compliance advisory and works alongside your legal counsel. We do not provide legal advice.
Start with the framework that matters most to you. Our consultants assess where you stand; the platform keeps it current.