The Fidempli AI governance platform launches in December 2026. Design-partner places are open.Apply now →
Fidempli

Cybersecurity

Privileged access management, from strategy to daily operation.

Admin rights that exist only when needed, are approved, recorded and reviewed.

The problem

Privileged accounts are the keys attackers look for first: domain and cloud administrators, database owners, service accounts and emergency accounts. In many organisations they have standing rights, shared passwords and no record of what was done with them.

ISO/IEC 27001 Annex A control 8.2 asks for privileged access rights to be restricted and managed, and NIS2 and DORA expect strict access control as part of ICT risk management. Auditors ask who had admin access, when and why, and spreadsheets cannot answer that.

What we do

Privileged Access Management

  1. Find privileged accounts

    We discover admin, service, application and emergency accounts across directories, cloud platforms, servers, databases and network devices, and assign an owner to each.

  2. Set the PAM strategy

    We define which accounts are vaulted, which access is granted just in time, how approvals work and which sessions are recorded, and choose the tools that fit your environment.

  3. Vault and rotate credentials

    We move privileged credentials into a vault, rotate them automatically and remove hard-coded passwords from scripts and applications.

  4. Introduce just-in-time access

    We replace standing admin rights with time-limited, approved elevation, for example with Microsoft Entra Privileged Identity Management or your PAM platform.

  5. Record and review

    We set up session recording and alerts for high-risk actions and run regular reviews of privileged rights with the account owners.

  6. Run PAM as a service

    We onboard new systems and accounts, handle rotation issues, maintain the platform and report on privileged access every month.

AI automation in this service

  • Automated discovery of new admin, service and app accounts in Entra ID, Active Directory and cloud platforms, flagged until they are vaulted or removed.
  • Automated detection of standing admin rights and unused privileges, feeding the privileged access reviews.
  • Automated summaries of recorded admin sessions, so reviewers start with the high-risk actions.

What you get

  • Inventory of privileged accounts with owners and risk rating
  • PAM strategy, target model and roadmap
  • Deployed vault with credential rotation
  • Just-in-time elevation and approval workflows
  • Session recording and alerting for high-risk actions
  • Privileged access review records and monthly reports

Frameworks

  • ISO/IEC 27001
  • NIS2
  • DORA
  • GDPR

In detail

Accounts covered

  • Domain and cloud administrators
  • Server, database and network admins
  • Service and application accounts
  • Emergency (break-glass) accounts
  • Third-party and vendor access
  • Non-human identities such as AI agents with elevated rights

Typical platforms

  • Microsoft Entra Privileged Identity Management
  • CyberArk
  • Delinea
  • BeyondTrust
  • Cloud-native tools in AWS, Azure and Google Cloud

Platform

After the project, the Fidempli platform keeps it running

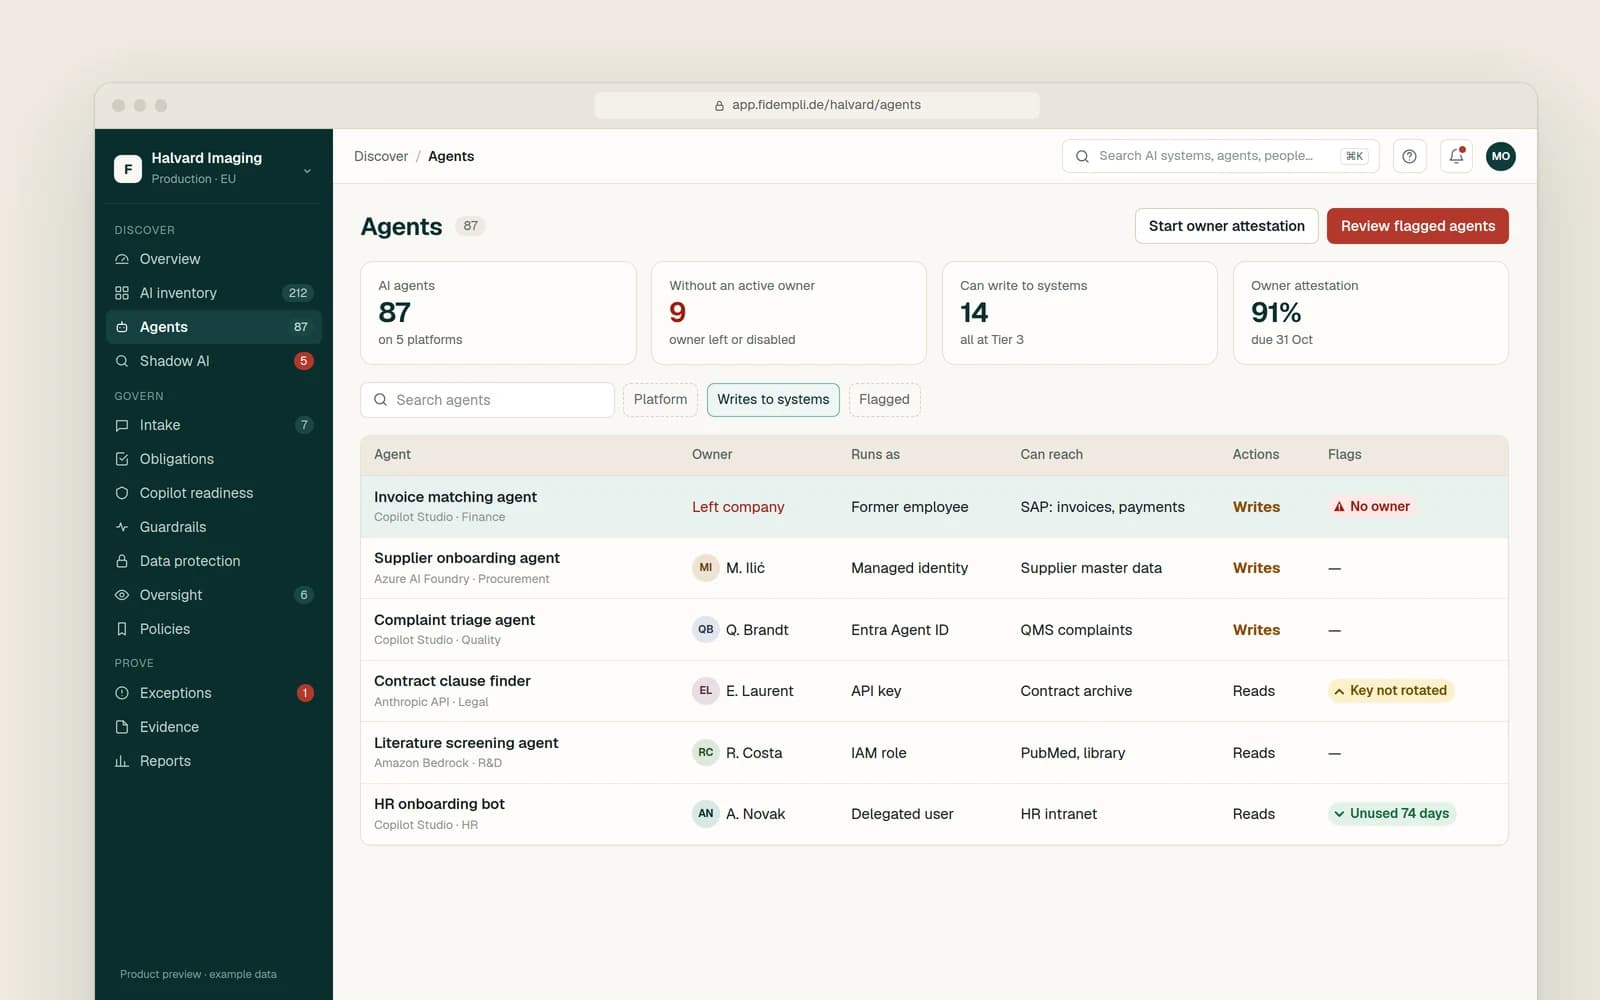
From December 2026, the Fidempli platform shows which AI agents and service accounts act with elevated rights, who owns them and whether their access was approved, next to your PAM records.

Explore the platform
Agents across five platforms with owner, identity, reach, actions and flags
Product preview with example data

Frequently asked questions

What is the difference between IAM and PAM?

IAM manages all identities and their access. PAM adds stronger controls for the small number of accounts that can change systems or read everything: vaulting, just-in-time elevation and session recording.

Do you work with a specific PAM product?

No. We work with the platform you already have or help you choose one. Microsoft Entra PIM covers many Microsoft and Azure cases; dedicated PAM platforms add vaulting and session recording for servers, databases and network devices.

What does PAM as a service include?

We onboard new systems and accounts, keep credential rotation working, maintain and upgrade the platform, run privileged access reviews with your owners and report every month. Approvals stay with your named owners.

How do you handle emergency accounts?

Break-glass accounts are kept to a minimum, protected with strong authentication, stored in the vault, excluded only where needed from conditional access rules and monitored so every use triggers an alert and a review.

Does PAM help with ISO 27001, NIS2 and DORA?

Yes. ISO/IEC 27001 Annex A 8.2 covers privileged access rights, and NIS2 and DORA expect strict access control. Vault records, approvals and session logs are evidence auditors accept.

More services in this domain

Start with a 30-minute AI risk conversation.

A senior consultant replies within one business day. Or join the 3–5 design partners shaping the platform before launch.