The GDPR asks organisations not only to comply but to be able to show it (Article 5(2)). That means records of processing, notices, processor contracts, a working process for rights requests and a plan for data breaches, all kept current.
Companies working between Europe and Japan also face Japan's Act on the Protection of Personal Information (APPI). Since the amendments in force from April 2022 it requires certain breaches to be reported to the Personal Information Protection Commission and sets stricter rules for transfers out of Japan. Two sets of rules often end up as two sets of paperwork.
What we do
Privacy Programme (GDPR and APPI)
Gap assessment
We compare your current practice with the GDPR, the German BDSG and TDDDG and, where you handle personal data from Japan, the APPI, and give you a prioritised list of gaps.
Governance and policies
We set roles and responsibilities, write or update the privacy policy, retention rules and internal guidelines, and define how privacy decisions are made.
Records of processing
We build or update your records of processing activities under Article 30 GDPR, with purposes, legal bases, recipients, transfers and retention for each activity.
Notices, consent and contracts
We review privacy notices, consent and cookie processes, data processing agreements and transfer mechanisms, including transfers between the EU and Japan.
Rights requests and breaches
We set up processes to answer data subject requests within the GDPR deadline of one month and to assess and report breaches within 72 hours, and align them with APPI reporting duties.
Run and improve
We train staff, review the programme regularly and keep it current as your business, your vendors and the rules change.
How we deliver
Consulting · Professional services · Managed services
Automated drafts of records of processing entries from your application and vendor inventory, reviewed by our consultants.
Automated intake, identity checks and deadline tracking for data subject requests.
Automated reminders for policy reviews, retention deadlines and expiring processor contracts.
What you get
GDPR and APPI gap assessment with priorities
Records of processing activities
Privacy policy, retention rules and internal guidelines
Reviewed notices, consent processes and processor agreements
Processes for data subject requests and data breaches
Privacy roadmap and training plan
Frameworks
GDPR
BDSG
TDDDG
APPI (Japan)
In detail
GDPR and German law
Accountability (Art. 5(2), 24)
Records of processing (Art. 30)
Transparency and notices (Art. 12–14)
Data subject rights (Art. 15–22)
Processors (Art. 28)
Breach notification (Art. 33, 34)
BDSG and employee data
TDDDG for cookies and similar technologies
Japan's APPI
Purpose of use and notice
Security control measures
Reporting of certain breaches to the PPC and notifying individuals
Transfers to third parties outside Japan
Pseudonymously processed information
EU–Japan mutual adequacy
Platform
After the project, the Fidempli platform keeps it running
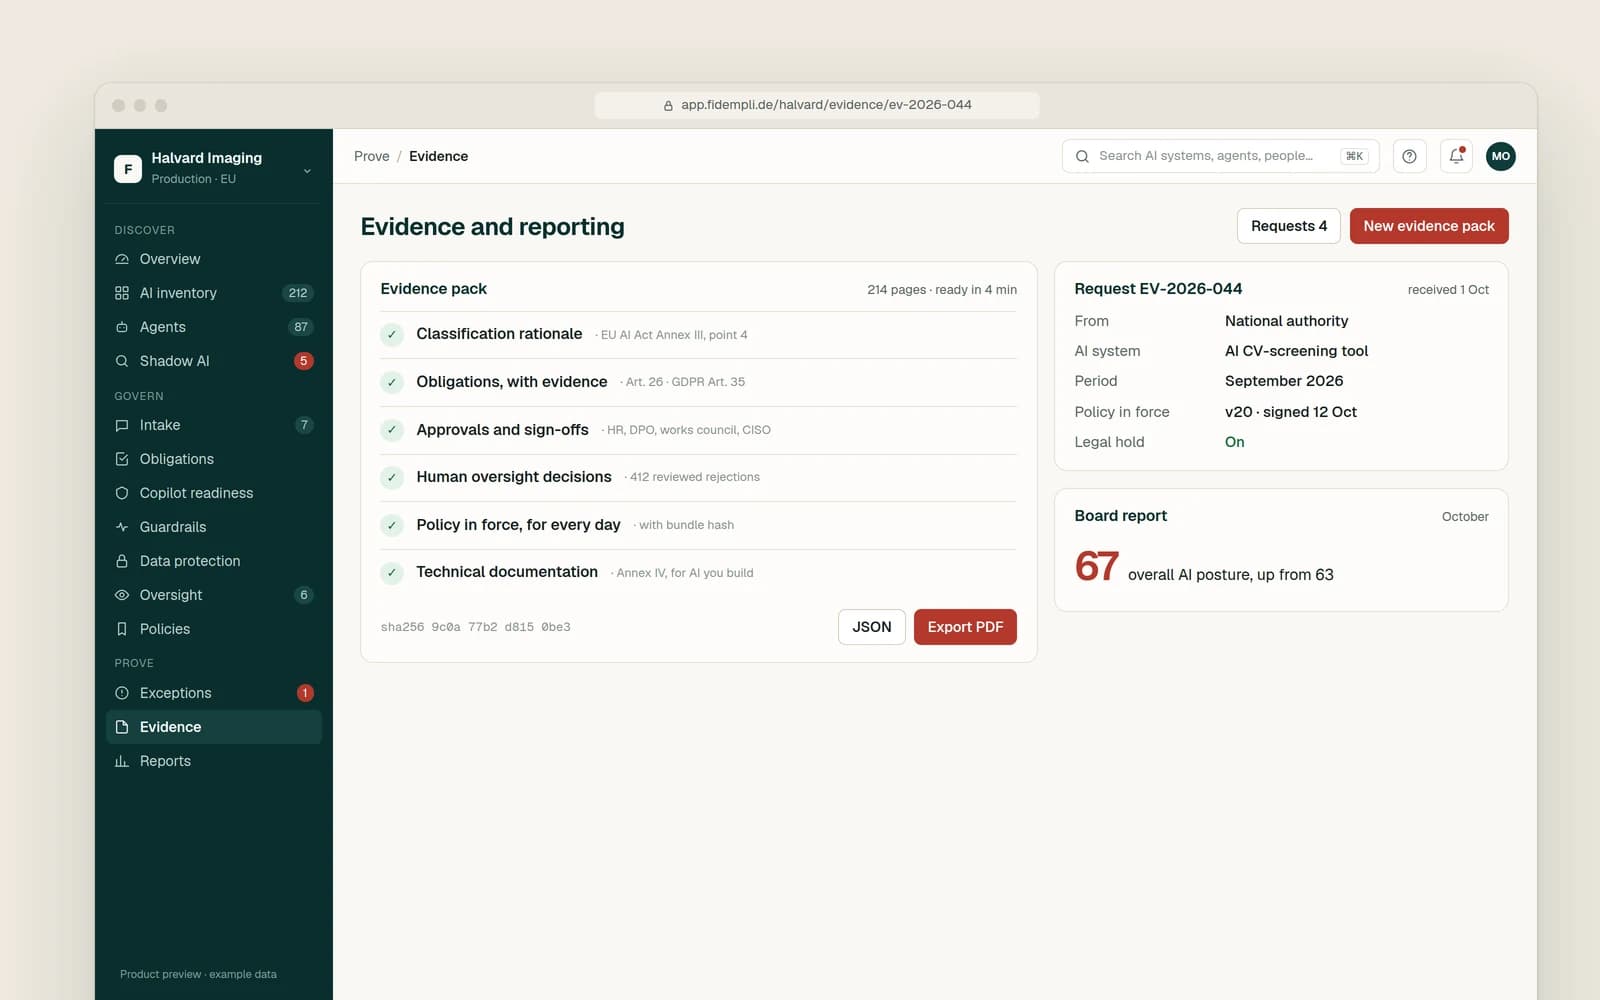
From December 2026, the Fidempli platform adds the AI part of your privacy programme: every AI system with its purpose, data categories and DPIA, ready to feed your records of processing.
Many of our clients work between Europe and Japan. Both laws ask for clear purposes, security measures, breach handling and transfer rules, so one programme with Japanese specifics added avoids duplicate work.
Can personal data flow between the EU and Japan?
The EU and Japan recognise each other's data protection as adequate since 2019, so personal data can generally flow from the EU to Japan without additional transfer tools, subject to supplementary rules on the Japanese side. Transfers out of Japan to other countries follow the APPI's own rules.
How fast must we answer a data subject request?
Under the GDPR without undue delay and within one month, which can be extended by two further months for complex or numerous requests if you inform the person.
Do you replace our data protection officer?
No. We support the person who holds the role. If you need an external data protection officer, that is a separate service.
Is this legal advice?
We give practical compliance support. For questions that need legal advice in the strict sense, we work with your legal team or external counsel.